Potential for backdoors in foreign telecom gear draws FCC's attention
Full article877 words · extracted from cyberscoop.com · click to collapse
Get our latest cybersecurity news first on Google.
Federal Communications Commission Chairman Ajit Pai wants to bar U.S. telecommunications providers from buying equipment and services he says could give foreign-government hackers a foothold into the supply chain.
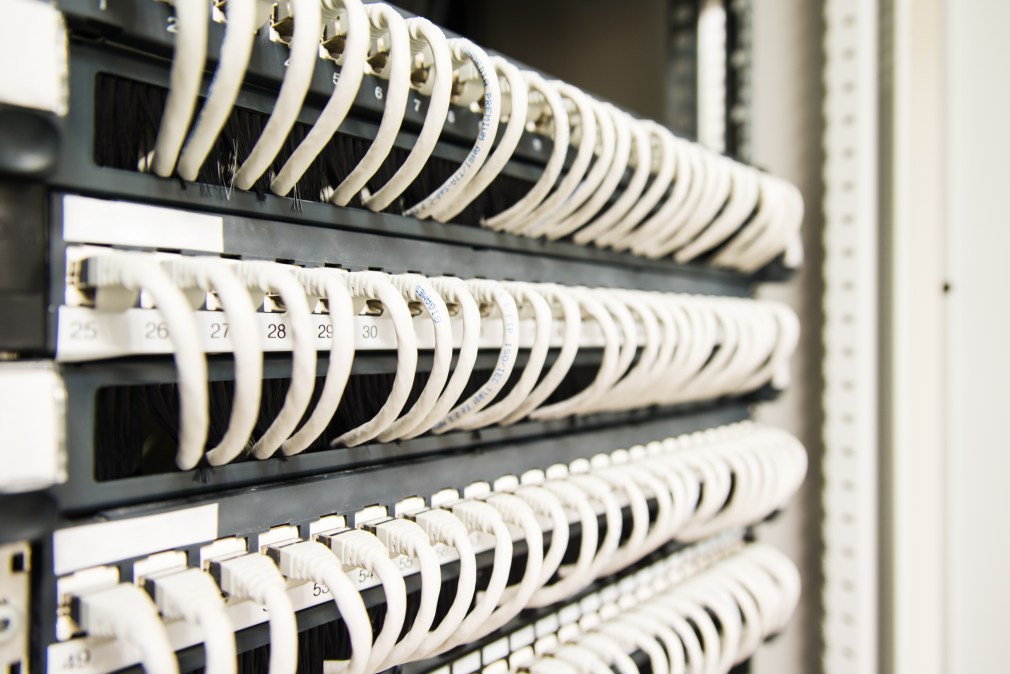
Federal Communications Commission Chairman Ajit Pai wants to inhibit U.S. telecommunications providers from buying equipment and services he says could give foreign-government hackers a foothold in U.S. networks.
A draft FCC proposal, released Tuesday, would prevent companies from using the commission’s $8.5 billion Universal Service Fund (USF) to buy routers, switches, and other gear from companies that “pose a national security threat to United States communications networks or the communications supply chain,” the FCC said in a statement.
Backdoors in networking equipment “can provide an avenue for hostile governments to inject viruses, launch denial-of-service attacks, steal data, and more,” Pai said.
The USF helps telecoms companies provide service in high-cost and rural areas in the U.S. The FCC plans to vote on the proposal April 17. The proposal wouldn’t be a blanket ban on buying such gear, because telecoms could use their own funds to do so rather than drawing from the USF, an FCC spokesperson told CyberScoop.
Cybersecurity experts have long considered the supply chain to be one of the thorniest challenges in the field because vulnerabilities introduced early in the development process can be extremely difficult to detect. Aware of such backdoors in software or hardware, hackers can bide their time until it is ripe for an attack.
The FCC proposal comes as Congress has moved to crack down on technology companies from China and Russia, citing supply-chain security concerns. Sens. Tom Cotton, R-Ark., and Marco Rubio, R-Fla., last month introduced a bill that would ban agencies from buying equipment or services from Chinese firms Huawei and ZTE, with Cotton describing Huawei as “effectively an arm of the Chinese government.” Under the 2018 National Defense Authorization Act, U.S. federal agencies are forbidden from buying software and hardware made by Moscow-based Kaspersky Lab.
Treasury Department officials, meanwhile, are working to identify sensitive tech sectors — such as semiconductor production — in which Chinese firms could be banned from investing, Bloomberg News reported.
Such piecemeal measures against companies and countries are, however, no substitute for a broader strategy to help bolster supply-chain cybersecurity in the private sector. The Department of Homeland Security has recently given shape to that strategy by offering a risk-assessment service for critical-infrastructure operators’ supply chains. The nascent program will advise companies on how they can close gaps in their procurement policies.
“As our cyber dependence increases and the connectivity of our networks and assets and data continue to grow, your risk — each of you individually in this room, each of your entities’ risk — becomes my risk,” DHS Secretary Kirstjen Nielsen told energy executives March 1.
More Scoops
Supply chain challenges loom large in quantum race, White House official says
Brad Blakestad, director of the National Quantum Coordination Office, also said encryption and measuring progress would pose challenges.
AI-generated code has made security debt a governance problem
FCC passes new cybersecurity rules for emergency systems, undersea cables
Latest Podcasts
Government
FBI officials say AI is bolstering adversaries, emphasizing need to focus on cyber basics, patching
Feds accuse China of ‘systematic’ distillation of U.S. AI models
CIA’s Michael Ellis says cyber intelligence is changing how the agency operates
The G7 tells industry to hurry up and prep for post-quantum encryption
Technology
Threats
Chinese espionage groups swarm to exploit triple-link chain of zero-days
Microsoft discloses two actively exploited zero-days among 974 vulnerabilities
Russian national extradited to US for alleged involvement in bank-account takeover scheme
Jail time for Maine child in 764 marks turning point in federal law enforcement
Policy
Whistleblower says USPS deploying new, ‘untested’ IT systems governing mail-in ballots
‘Watershed 250’ test program in Texas looks to private sector for water cybersecurity help
Former sexual abuse victims say Grok used their images, videos to train deepfake capabilities
Cyber threats nudge Trump to sign executive order on foreign equipment in U.S. energy infrastructure
Text extracted automatically; images, tables and formatting may be missing. Original: https://cyberscoop.com/fcc-wants-to-ban-products-that-could-be-footholds-for-foreign-hackers/