Microsoft: Iranian espionage campaign targeted satellite and defense sectors
Full article755 words · extracted from cyberscoop.com · click to collapse
Get our latest cybersecurity news first on Google.
Tehran's latest hacking activity involves easy-to-detect techniques to gain access and then pivoting to stealthier methods.
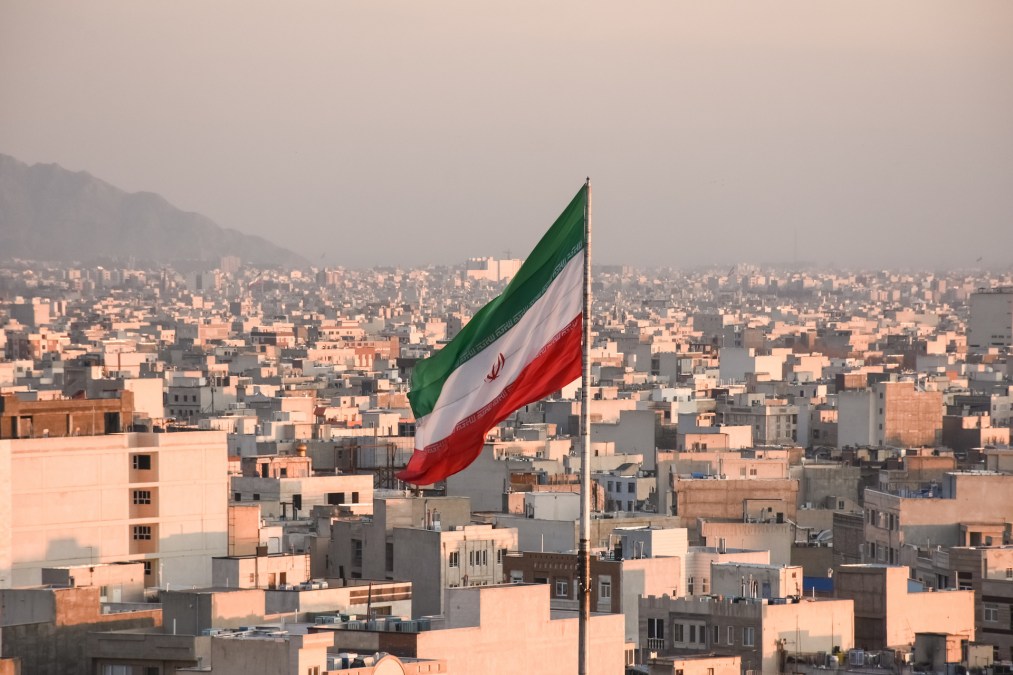
An Iranian cyber espionage group successfully compromised dozens of entities and exfiltrated data from a subset of them as part of a campaign targeting organizations in the satellite, defense and pharmaceutical sectors, Microsoft said in a report published Thursday.
The group in question — which Microsoft tracks as Peach Sandstorm but known otherwise as Holmium, APT33 or Elfin — compromised the accounts as part of a high volume of password spray attacks, where attackers try one known password against a list of usernames. The campaign began in February and targeted thousands of organizations, according to Microsoft.
Microsoft did not say where the targeted organizations are based but noted that previous Peach Sandstorm activity occurred during a “rise in tensions between the United States and the Islamic Republic of Iran.” Researchers have linked some of the group’s previous operations to the devastating destructive Shamoon malware attacks that targeted Saudi Aramco, the oil company, in 2012 and other targets in subsequent years.
The news comes on the heels of an incipient deal between the U.S. and Iranian governments that would allow banks to transfer $6 billion in frozen Iranian oil funds and see U.S. authorities release of five Iranian citizens held in the United States in exchange for the release of five American citizens detained in Iran, the Washington Post reported Monday.
The hacking activity disclosed on Monday took place between February and July this year, and Microsoft said that the hackers used the access they gained to maintain persistence on breached systems and carry out other, unspecified activity. Password spray attacks are noisy and easy to detect, but Microsoft researchers said that the activity is concerning because once the hackers gain access, they are in some cases pivoting toward stealthier, more sophisticated methods that represent an increase in capability compared to Peach Sandstorm’s past activity.
Researchers observed two pathways into targeted organizations associated with the campaign. The first, via the password spray route, allowed researchers to learn more about the campaign, showing, for instance, that the activity occurred almost exclusively between 9 a.m. and 5 p.m. Iran Standard Time. The second pathway saw the group attempt to exploit a pair of vulnerabilities from 2022 affecting a subset of on-premises Zoho ManageEngine products and the Confluence Server and Data Center.
More Scoops
Feds quash widespread Russia-backed espionage network spanning 18,000 devices
Forest Blizzard, a threat group attributed to Russia’s GRU, hijacked network traffic to steal credentials and tokens for Microsoft accounts and other services.
Iranian hackers launching disruptive attacks at U.S. energy, water targets, feds warn
New Russian state-sponsored APT quickly gains global reach, hitting expansive targets
Latest Podcasts
Government
FBI officials say AI is bolstering adversaries, emphasizing need to focus on cyber basics, patching
CIA’s Michael Ellis says cyber intelligence is changing how the agency operates
The G7 tells industry to hurry up and prep for post-quantum encryption
Jail time for Maine child in 764 marks turning point in federal law enforcement
Technology
Threats
Policy
Whistleblower says USPS deploying new, ‘untested’ IT systems governing mail-in ballots
‘Watershed 250’ test program in Texas looks to private sector for water cybersecurity help
Former sexual abuse victims say Grok used their images, videos to train deepfake capabilities
Cyber threats nudge Trump to sign executive order on foreign equipment in U.S. energy infrastructure
Text extracted automatically; images, tables and formatting may be missing. Original: https://cyberscoop.com/iran-peach-sandstorm-apt33/