Full article260 words · extracted from securelist.com · click to collapse



There are new variants of Bagle circulating actively at the moment: Email-Worm.Win32.Bagle.ax and Email-Worm.Win32.Bagle.ay. When the worms search the victim machines for email addresses to send themselves to, they won’t send emails to addresses containing the following text:
|
|
|
By doing this, the new Bagles are hiding from antivirus companies. This explains the relatively small number of samples that we’ve received so far.
Here’s a sample of what a Bagle.ay message looks like:
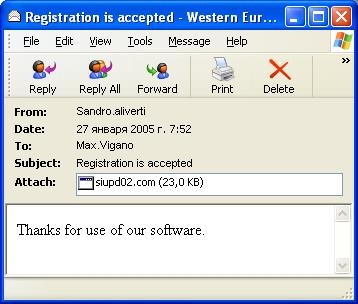
Full description of the new Bagles will be available in the Virus Encyclopedia in the near future.
Update If the infected attachment has a .cpl extension, it will be detected as Email-Worm.Win32.Bagle.at.
Latest Webinars
Reports
Kaspersky researchers have discovered new Mirage Kitten attacks using previously undocumented malware families: NodeRabbit in Node.js and PollCat in JavaScript.
Our experts discovered a new CoolClient backdoor variant with a kernel-mode rootkit driver that hides malicious processes, files, and network connections from security tools and threat analysts.
Kaspersky experts break down a new Armored Likho campaign that poses as a fundraising efforts and delivers a new Still Toolkit aimed at stealing Telegram data and eavesdropping on victims.
Kaspersky researchers reveal previously undocumented malware attributed to Mirage Kitten (UNC1549, Smoke Sandstorm, Nimbus Manticore): NightLedger backdoor, ArcBridge, and BridgeHead tunneling tools.
Text extracted automatically; images, tables and formatting may be missing. Original: https://securelist.com/email-worm-win32-bagle-ax-and-bagle-ay/29953/