Vulnerability disclosure policies eyed for federal contractors in Senate bill
Full article844 words · extracted from cyberscoop.com · click to collapse
Get our latest cybersecurity news first on Google.
The legislation from Sens. Warner and Lankford would require federal contractors to adhere to NIST’s guidelines on VDPs.
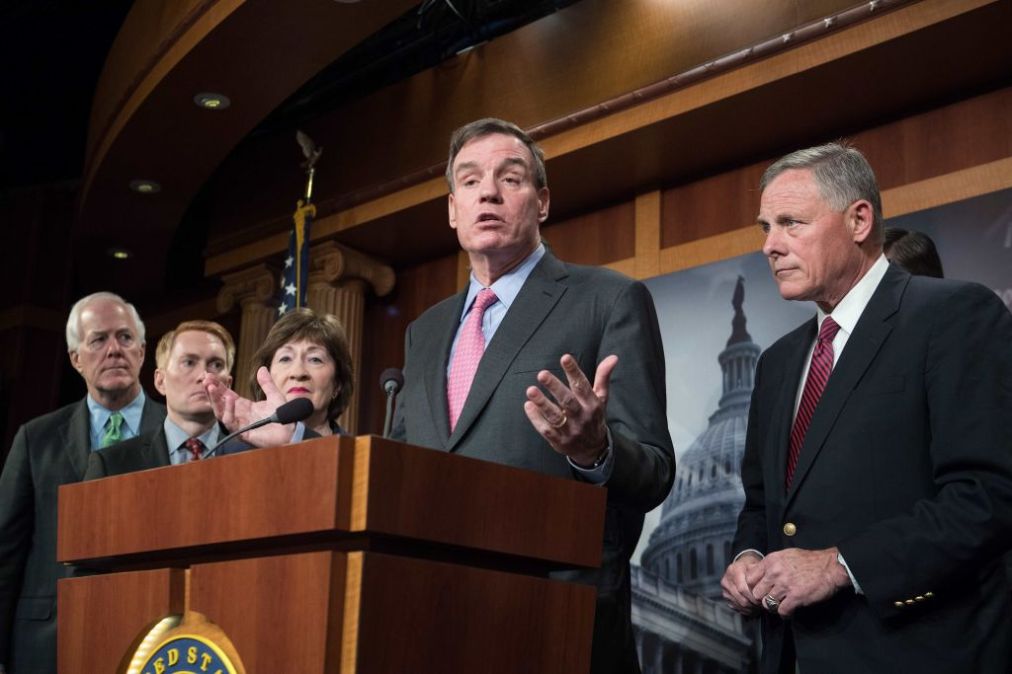
Federal contractors would be required to implement vulnerability disclosure policies that align with National Institute of Standards and Technology guidelines under a bipartisan Senate bill introduced last week.
The Federal Contractor Cybersecurity Vulnerability Reduction Act of 2024 from Sens. Mark Warner, D-Va., and James Lankford, R-Okla., is a companion to legislation from Rep. Nancy Mace, R-S.C., which was advanced by the House Oversight Committee in May.
The bill from Warner and Lankford on vulnerability disclosure policies (VDPs) aims to create a structure for contractors to receive reports of vulnerabilities in their products and then act against them before an attack occurs.
“VDPs are a crucial tool used to proactively identify and address software vulnerabilities,” Warner said in a statement. “This legislation will ensure that federal contractors, along with federal agencies, are adhering to national guidelines that will better protect our critical infrastructure, and sensitive data from potential attacks.”
While current federal law requires civilian agencies to have VDPs, there is no such standard for federal contractors. The bill would address that discrepancy by instituting a requirement for contractors and mandating that they accept, assess, and manage the vulnerability reports they receive.
“Federal agencies and contractors must be quickly made aware of cyber vulnerabilities, so they can resolve them,” Lankford said in a statement. “By strengthening cybersecurity efforts, contractors and agencies can keep their focus on serving the American people and keep data and systems safe from cybercrimes and hacking.”
A fact sheet accompanying the release of the bill referenced the 2015 Office of Personnel Management data breach, that was made possible by vulnerabilities in systems used by two contractors that stored data on federal employee background checks. This legislation, the fact sheet noted, would ensure that “good-faith security researchers” can reach out directly to federal contractors without having to provide additional reporting to an agency.
The bill would require the Office of Management and Budget to spearhead Federal Acquisition Regulation updates, a move intended to guarantee that contractors’ VDPs align with current federal agency requirements. The Secretary of Defense would have the same obligations for Defense Federal Acquisition Regulation Supplement contract standards.
The press release announcing the legislation included statements of support from Palo Alto Networks and HackerOne, whose chief legal and policy officer, Ilona Cohen, said the bill “addresses a critical gap” in U.S. cybersecurity.
“This proactive approach to security will ensure that businesses are actively protecting government systems, critical infrastructure, and sensitive data from exploitation by malicious actors,” she said.
More Scoops
Sen. Wyden urges feds to discard older, insecure, public-facing VPNs
In a letter first reported by CyberScoop, Ron Wyden, D-Ore., said ‘devastating’ attacks on the federal government have accumulated due to the tech.
GCVE launches as a decentralized system for tracking software vulnerabilities
Why federal IT leaders must act now to deliver NIST’s post-quantum cryptography transition
Latest Podcasts
Government
FBI officials say AI is bolstering adversaries, emphasizing need to focus on cyber basics, patching
Feds accuse China of ‘systematic’ distillation of U.S. AI models
CIA’s Michael Ellis says cyber intelligence is changing how the agency operates
The G7 tells industry to hurry up and prep for post-quantum encryption
Technology
Threats
Policy
Whistleblower says USPS deploying new, ‘untested’ IT systems governing mail-in ballots
‘Watershed 250’ test program in Texas looks to private sector for water cybersecurity help
Former sexual abuse victims say Grok used their images, videos to train deepfake capabilities
Cyber threats nudge Trump to sign executive order on foreign equipment in U.S. energy infrastructure
Text extracted automatically; images, tables and formatting may be missing. Original: https://cyberscoop.com/federal-contractor-vulnerability-disclosure-policies-senate-bil/