Lawmakers must incentivize cyber protection for critical infrastructure
Full article1,194 words · extracted from cyberscoop.com · click to collapse
Get our latest cybersecurity news first on Google.
In a world where critical infrastructure networks are increasingly digitalized and interconnected, cyber risk is growing as a significant threat to our nation’s security, safety.
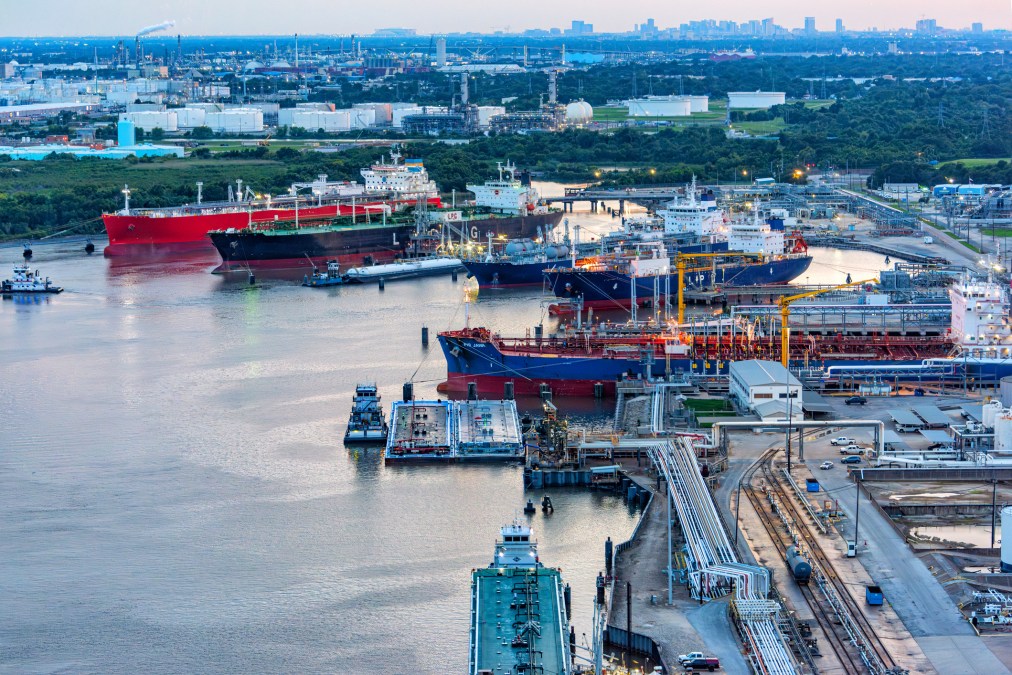
National headlines, federal advisories, and the President’s Council of Advisors on Science and Technology warn of unprecedented threats by nation-state actors, criminals, and terrorists as digital connections create access to networks that could endanger the health and safety of every American. Power grids can go down, water systems can be poisoned, pipelines can rupture, vehicles can crash, and medical care can be disrupted — consequences not experienced in data or software exploitation as these outcomes could kill people.
Given this threat landscape, federal policymakers are keen to explore how insurance products can improve the nation’s cyber risk management. To protect the public from catastrophic cyber events, the nation must facilitate the establishment of mandatory cyber safety engineering standards for the technologies and systems essential to our livelihood.
A recent congressional hearing touched upon insurance incentives to reduce critical infrastructure cyber risk similar to what homeowners receive for having an active security system or for safe driver discounts. The White House also confirmed this month that it is working on cyber insurance policy proposals for “catastrophic” incidents to “manage risk and not avoid risk” by starting with actuary assessments to examine companies’ cybersecurity practices, protections, and more. The emphasis on proactive risk management is welcome news in the current vicious cycle of ransomware attacks across all sectors. In the current model, cyber insurers may incentivize bad behavior by offering quick paths to pay the criminals.
Managing risk must start with legally recognized “standards of care” in each Operational Technology (OT) vertical to promulgate safety and security standards and engineering guidance. For example, historically, there’s been a mutual business interest in mitigating risks from fire, electricity, mechanical malfunctions, and structural failures. As a result, established engineering standards allow insurers to develop affordable risk transfer mechanisms. Without standards, the risk is extreme, leading to skyrocketing premiums, high deductibles, and significant exclusions, ultimately resulting in minimal coverage, if any.
Safeguarding the public requires applying cyber safety to the engineering of everything we build, from cars and robots to buildings and physical infrastructure. These standards must go beyond “secure by design” principles for software. Firewalls, passwords, and air gaps don’t work in a converged ecosystem of cyber-physical systems. Cyber-Informed Engineering must become a mandatory cyber safety set of requirements; it can’t be voluntary. The National Institute of Standards and Technology must specifically address the need for critical systems to protect life and property. While continuous discovery, assessment, and governance across the engineering environment are foundational to avoid catastrophic loss, more must be done.
Given the $1.2 trillion authorized in the bipartisan Infrastructure Investment and Jobs Act, now is the time to build resiliency into our critical infrastructure. New critical infrastructure systems must incorporate approved products and technologies specifically designed to mitigate cyber risk. Then, insurers can effectively assess the remaining risk to determine levels of mitigation or transfer costs. Cyber risks impacting physical safety should only be transferred from owners to insurers if mandatory risk mitigation programs are developed, prioritized, funded, and monitored.
A taxpayer-funded backstop for cyber insurance requiring the U.S. Treasury to support claims for catastrophic cyber incidents that lead to death and physical destruction may cause more harm than good. Reinsurers could take advantage of the backstop by offloading potential risks — such as infrastructure attacks or state-backed attacks — to the government. While the U.S. has a similar program for national floods, it prioritizes relief for recovery over incentivizing investments to preclude flood claims in the first place. Every dollar spent transferring cyber risk is a lost opportunity to reduce public safety risk. We cannot gamble with a moral hazard risk in our nation’s infrastructure where policyholders engage in riskier behavior after purchasing insurance because they are protected from consequences that are much more threatening when uninsured.
Active collaboration between the asset owners and operators, their engineers, and insurers is crucial and indispensable in developing effective cyber risk management strategies prioritizing public safety. Stakeholders can collectively enhance their cyber defenses and minimize impacts by aligning interests on cyber safety standards and sharing insights on emerging threats and vulnerabilities. This collaborative approach fosters a safety culture of continuous improvement and knowledge-sharing to stay ahead of evolving cyber threats by maturing defenses accordingly.
The White House and Congress must ensure that public policy prioritizes risk mitigation over easing risk transfer mechanisms to shape a more resilient ecosystem. With lives at stake, we need to invest nationally in consequence avoidance, not post-catastrophic consequence management.
Lucian Niemeyer is a U.S. Air Force veteran, a former Senate Armed Services Committee staff member, a White House official, and Assistant Secretary of Defense. He runs a nonprofit organization, BuildingCyberSecurity.org, committed to enhancing human cybersecurity and physical safety in the built environment.
Alison King is the vice president of government affairs at Forescout Technologies, an OT Cyber Coalition executive member, and a senior fellow at the McCrary Institute for Cyber & Critical Infrastructure Security at Auburn University.
More Scoops
Sen. Wyden urges feds to discard older, insecure, public-facing VPNs
In a letter first reported by CyberScoop, Ron Wyden, D-Ore., said ‘devastating’ attacks on the federal government have accumulated due to the tech.
Open-source security is posing challenges governments can’t easily solve
CISA is rethinking how it prioritizes risks and vulnerabilities for feds, private sector
Latest Podcasts
Government
FBI officials say AI is bolstering adversaries, emphasizing need to focus on cyber basics, patching
Feds accuse China of ‘systematic’ distillation of U.S. AI models
CIA’s Michael Ellis says cyber intelligence is changing how the agency operates
The G7 tells industry to hurry up and prep for post-quantum encryption
Technology
Threats
Chinese espionage groups swarm to exploit triple-link chain of zero-days
Microsoft discloses two actively exploited zero-days among 974 vulnerabilities
Russian national extradited to US for alleged involvement in bank-account takeover scheme
Attackers exploit zero-days in consistently besieged SonicWall product
Policy
Whistleblower says USPS deploying new, ‘untested’ IT systems governing mail-in ballots
‘Watershed 250’ test program in Texas looks to private sector for water cybersecurity help
Former sexual abuse victims say Grok used their images, videos to train deepfake capabilities
Cyber threats nudge Trump to sign executive order on foreign equipment in U.S. energy infrastructure
Text extracted automatically; images, tables and formatting may be missing. Original: https://cyberscoop.com/cyber-insurance-critical-infrastructure-engineering-standards-congress/