NSO Group's latest spyware on par with nation
Full article961 words · extracted from cyberscoop.com · click to collapse
Get our latest cybersecurity news first on Google.
The analysis offers a window into the level of spyware the embattled spyware firm offered clients around the world.
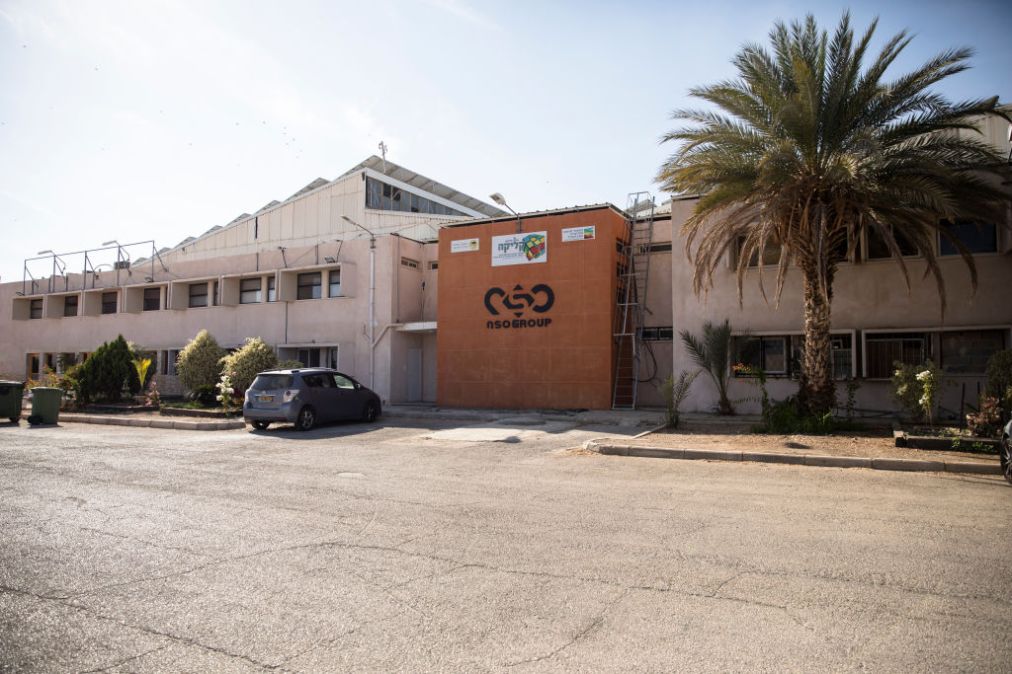
When Apple announced Nov. 23 that it filed a lawsuit against Israeli spyware firm NSO Group, it claimed that the firm and its clients “devote the immense resources and capabilities of nation-states to conduct highly targeted cyberattacks.” An independent analysis published Wednesday backs that claim up.
Google Project Zero researchers Ian Beer and Samuel Groß took a deep dive into FORCEDENTRY, the malware developed by NSO Group that allowed adversaries to infect targeted Apple devices — without the owner’s knowledge — with NSO Group’s Pegasus spyware. The researchers concluded that it’s “one of the most technically sophisticated exploits” they’ve ever seen, rivaling “those previously thought to be accessible to only a handful of nation states.”
Previous iterations of the Pegasus software required the victim to click a link in an SMS message. But FORCEDENTRY was an example of NSO Group’s zero-click exploitation technology, where no interaction from the target was required.
“Short of not using a device, there is no way to prevent exploitation by a zero-click exploit,” the researchers wrote Wednesday. “It’s a weapon against which there is no defense.”
The analysis details how FORCEDENTRY exploited a since-patched vulnerability in Apple’s iMessage SMS service processing of GIF image files. A vulnerability in the way iMessage rendered GIFs, involving 1990s-era scanning and compression software, allowed for a malicious PDF to be loaded and opened without the target’s knowledge, giving an adversary access to data in other areas of the device.
“It’s pretty incredible,” the researchers wrote, “and at the same time, pretty terrifying.”
Two patches from Apple, one in September and the other in October, corrected the issues in that processing protocol that enabled this vulnerability, the researchers note.
“It’s really sophisticated stuff,” John Scott-Railton, senior researcher at Citizen Lab, told Wired, which first wrote about the Project Zero analysis. “And when it’s wielded by an all-gas, no-brakes autocrat, it’s totally terrifying.”
Citizen Lab, a human rights group based in Toronto, discovered FORCEDENTRY in September during an analysis of a Saudi activits’ phone. It turned the information over to Apple, and also provided a sample of FORCEDENTRY to the Project Zero researchers.
NSO Group’s malware has been under scrutiny for years as an enabling factor for authoritarian governments around the world to target human rights activists, journalists and political opponents. The U.S. government added the company to its sanctions list on Nov. 4, making it difficult for the company to interact with any U.S. business.
On Tuesday, a group of U.S. lawmakers asked the Treasury Department and State Department to sanction NSO Group, along with surveillance firms in the United Arab Emirates and in Europe.
The pressure has mounted to the point that the company is reportedly mulling a shutdown of its Pegasus unit and a possible sale.
NSO Group did not immediately respond to a request for comment, but has frequently denied wrongdoing and touted the benefits of its technology in combatting crime. Apple declined to comment.
More Scoops
Pegasus, NoviSpy variant spyware found on devices of Serbian activists
It’s the first Pegasus infection of 2026 that Citizen Lab is forensically confirming, and the SHARE Foundation said it’s the biggest wave of spyware surveillance in Serbia…
Someone infected a spyware probe overseer with spyware
Meta accuses NSO Group of defying spyware injunction, files contempt of court complaint
Latest Podcasts
Government
FBI officials say AI is bolstering adversaries, emphasizing need to focus on cyber basics, patching
Feds accuse China of ‘systematic’ distillation of U.S. AI models
CIA’s Michael Ellis says cyber intelligence is changing how the agency operates
The G7 tells industry to hurry up and prep for post-quantum encryption
Technology
FCC proposes public scorecard to rate telecoms on anti-robocall efforts
Wyden seeks upgraded NSA security guidance on commercial VPN use
The Collective Cyber Defense letter wrote your next vendor questionnaire
Former sexual abuse victims say Grok used their images, videos to train deepfake capabilities
Threats
Microsoft discloses two actively exploited zero-days among 974 vulnerabilities
Russian national extradited to US for alleged involvement in bank-account takeover scheme
Attackers exploit zero-days in consistently besieged SonicWall product
Jail time for Maine child in 764 marks turning point in federal law enforcement
Policy
Whistleblower says USPS deploying new, ‘untested’ IT systems governing mail-in ballots
‘Watershed 250’ test program in Texas looks to private sector for water cybersecurity help
Cyber threats nudge Trump to sign executive order on foreign equipment in U.S. energy infrastructure
Election official says Tina Peters would be consultant, won’t have access to election systems
Text extracted automatically; images, tables and formatting may be missing. Original: https://cyberscoop.com/nso-group-spyware-forcedentry-nation-state-hackers/