U.S. Cyber Command chief calls for debate around hacking unit's authorities
Full article915 words · extracted from cyberscoop.com · click to collapse
Get our latest cybersecurity news first on Google.
Lawmakers and Pentagon leadership are considering plans that could one day provide U.S. Cyber Command with additional authorities to operate outside declared war zones, two senior U.S. officials acknowledged Wednesday during an open congressional hearing.
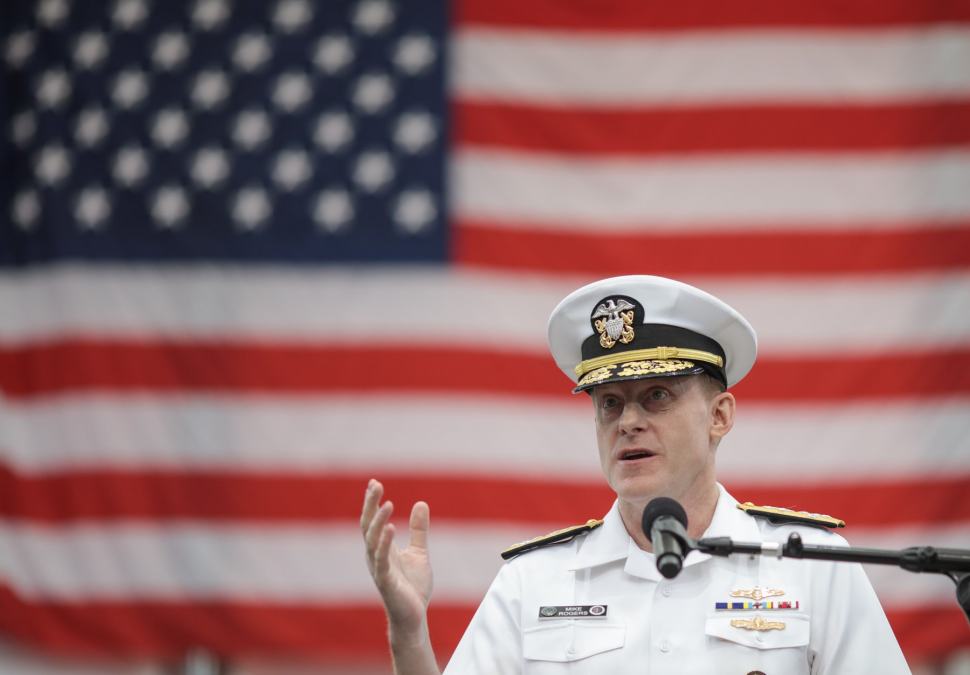
Lawmakers and Pentagon leadership are considering plans that could one day provide U.S. Cyber Command with additional authorities to more easily operate outside declared war zones, two senior U.S. officials acknowledged Wednesday during an open congressional hearing.
The testimony confirms aspects of a story CyberScoop published Wednesday about a push inside the government to give more authority to the military’s top hacking unit. That story described concerns shared in the intelligence community about the potential impact of a spike in cyberwarfare operations.
Such a shift in policy may allow Cyber Command to offer more protection to private companies, including those that own and operate what the U.S. government considers “critical infrastructure.” When it comes to offensive measures, the shift could also open the door for soldiers to hack a much wider array of targets; beyond the Middle East, where the military is already engaged in firefights.
Under existing authorities, U.S. Cyber Command typically operates on Title 10 of the U.S. Code; which largely restricts the command from hacking into computer systems where armed conflict is absent. If the government wants to hack outside of a conflict, it currently has to depend on the intelligence community, which operates under Title 50 of the U.S. Code.
Current NSA Director and head of U.S. Cyber Command Adm. Michael Rogers said Wednesday that there’s an ongoing policy discussion about U.S. Cyber Command’s future responsibilities.
“One of the questions I think we need to ask ourselves, for example with the defense industrial base or if it’s DoD’s role to partner to protect critical infrastructure, what level of ability to operate outside the [Department of Defense Information Network], would be appropriate for the cyber mission force?,” questioned Rogers. “I think that’s a good conversation for us to have.”
Rogers testified Wednesday alongside Kenneth Rapuano, assistant secretary of defense for homeland defense and global security at the Department of Defense. The hearing was Rogers’ last as the head of both the spy agency and U.S. Cyber Command.
Rogers’ expected successor, Gen. Paul Nakasone of U.S. Army Cyber Command, should be confirmed later this month via a Senate vote.
“[On offense] the area where I think we still need to get a little more speed and agility — and as Mr. Rapuano indicated it is an area that is currently under review right now — what is the level of comfort in applying those capabilities outside designated areas of hostility,” Rogers asked out loud.
“I don’t believe anyone should grant Cyber Command or Adm. Rogers a blank ticket to do whatever you want, that is not appropriate. The part I am trying to figure out is what is the appropriate balance to ensure the broader set of stakeholders have a voice.”
Rapuano also referenced challenges associated with defining “war” in the context of cyber, which can be borderless due to the interconnected nature of the internet.
“In a domain that is so novel in many respects, and for which we do not have the empirical data and experience associated with military operations per say particularly outside areas of conflict, there are some relatively ambiguous areas around ‘well what constitutes traditional military activities,'” said Rapuano. “This is something that we are looking at within the administration and we’ve had a number of discussions with members and your staffs; so that’s an area we’re looking at to understand the trades and implications of changing the current definition.”
In response, Rep. Jim Langevin, D-R.I., said that the House Armed Service Committee pledged to provide “rigorous oversight” for any impending change.
There are already certain situations where Cyber Command will be allowed to operate outside declared war zones. If the command is given direct approval from the White House through the chain of command at the Pentagon then the opportunity may present itself. But that approval process can be lengthy and arduous. Broadly speaking, the current conversation is focused around providing more leeway for Cyber Command to take action in cyberspace when appropriate.
Latest Podcasts
Government
FBI officials say AI is bolstering adversaries, emphasizing need to focus on cyber basics, patching
Feds accuse China of ‘systematic’ distillation of U.S. AI models
CIA’s Michael Ellis says cyber intelligence is changing how the agency operates
The G7 tells industry to hurry up and prep for post-quantum encryption
Technology
Threats
Microsoft discloses two actively exploited zero-days among 974 vulnerabilities
Russian national extradited to US for alleged involvement in bank-account takeover scheme
Attackers exploit zero-days in consistently besieged SonicWall product
Jail time for Maine child in 764 marks turning point in federal law enforcement
Policy
Whistleblower says USPS deploying new, ‘untested’ IT systems governing mail-in ballots
‘Watershed 250’ test program in Texas looks to private sector for water cybersecurity help
Former sexual abuse victims say Grok used their images, videos to train deepfake capabilities
Cyber threats nudge Trump to sign executive order on foreign equipment in U.S. energy infrastructure
Text extracted automatically; images, tables and formatting may be missing. Original: https://cyberscoop.com/u-s-cyber-command-chief-calls-for-debate-around-expansion-of-auth/