Parallels Desktop flaw hands any local user root on a Mac (CVE-2026-90894)
CVE-2026-90894 in Parallels Desktop for Mac lets any local user gain root via argument injection; patched in v27.0.0, PoC withheld.
JFrog researchers disclosed CVE-2026-90894, an argument injection flaw in Parallels Desktop for Mac v26.4.0 on Apple silicon that lets any local user gain root on the host. The chain combines a world-writable Unix socket for prl_disp_service (which runs as root), weak peer-credential authentication, and argument injection via --use-compress-program in the appliance extraction tar path. Alludo fixed the flaw in Parallels Desktop v27.0.0 in early September 2026; JFrog published technical details but withheld its proof-of-concept script.
- World-writable Unix socket plus weak peer-credential login enables argument injection via --use-compress-program in tar.
- Affects Parallels Desktop v26.4.0 on Apple silicon; the virtual machine need not be running.
- prl_disp_service launch daemon runs as root and starts automatically on load.
- From root, attackers can replace system software, read other users' data, and persist via launchd.
- Admins should inventory Macs running Parallels and upgrade to v27.0.0 or later.
Vulnerabilities mentionedAll →
| CVE | Vulnerability | CVSS | EPSS | Flags | Affected | Exposure | Published |
|---|---|---|---|---|---|---|---|
| CVE-2026-90894 | Local Root Privilege Escalation in Parallels Desktop via tar Argument Injection Parallels Desktop on macOS runs its prl_disp_service daemon as root and exposes it on the world-writable Unix socket /var/run/prl_disp_service.socket, where PrlSrv_LoginLocal authenticates clients purely on peer credentials without checking for a Parallels signature or administrator group membership. Once connected, any local user can call PrlSrv_InstallAppliance and supply an appliance folder path (sVmParentPath) that gets embedded in the command string tar -xf "%1" -C "%2"; because Qt's QProcess::splitCommand re-splits the string into words, an embedded quote closes the argument early and turns leftover text into attacker-chosen tar flags. macOS tar's --use-compress-program option then executes the named program, giving the attacker arbitrary code execution as root — a full local privilege escalation from any unprivileged account on the Mac. All Macs running an affected Parallels Desktop build (the advisory does not specify version ranges) with additional local user accounts are exposed. No public proof of concept is known and the CVE is not in CISA's KEV catalog, so there is no evidence of in-the-wild exploitation at this time. Do: Update Parallels Desktop to the newest available release as soon as the vendor ships a fix — no patched version is named in this advisory, so check the Parallels security bulletin directly. Until patched, treat any Mac running Parallels Desktop with local untrusted or shared accounts (e.g., guest, student lab, or kiosk logins) as exposed to full root compromise, and restrict local account creation on those machines. Monitor prl_disp_service for unexpected child processes, particularly tar invocations carrying --use-compress-program or odd -C paths from appliance installs. | 7.8 | — |
| masslikely millions of Macs (Parallels Desktop is the leading commercial macOS virtualization product; no affected-version install counts published) |
Full article365 words · extracted from helpnetsecurity.com · click to collapse
A newly disclosed vulnerability in Parallels Desktop, tracked as CVE-2026-90894 and dubbed “ParaShells,” can allow any local user on a Mac to gain root privileges on the host system.
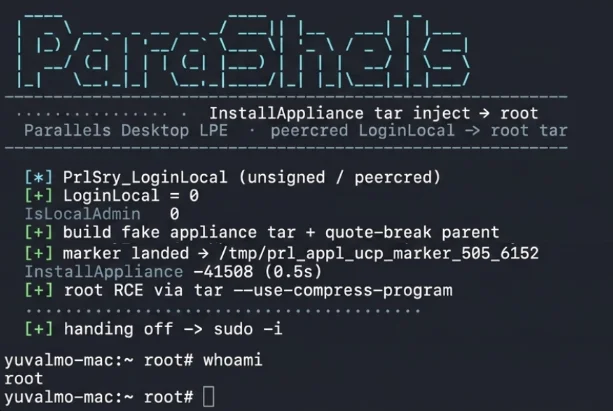
ParaShells PoC in action (Source: JFrog)
The danger is highest on developer laptops, where a single poisoned Homebrew formula or malicious npm preinstall script can go from local user to full control, and on shared university and corporate machines that have many local accounts, JFrog vulnerability research team lead Yuval Marvchick noted.
“From root, the attacker can replace system software, read other users’ data, and persist via launchd,” he added.
How the attack works
CVE-2026-90894 is an argument injection flaw that’s proven to affect Parallels Desktop for Mac v26.4.0, installed on macOS running on Apple’s own ARM-based processor. (Older builds might be vulnerable, but the researchers did not test them.)
Exploitation of ParaShells hinges on three things:
- A vulnerable version of the virtualization software being installed (but a virtual machine doesn’t have to be running)
- The prl_disp_service being active (its launch daemon starts it automatically on load, and it runs as root) and the /var/run/prl_disp_service.socket present, and
- The attacker being able to run code as any low-privileged local user.
“The exploit combines its world-writable Unix socket with weak local-client authentication and argument injection in the appliance extraction path,” Marvchick explained.
“The chain is short: A world-writable Unix socket, a login that trusts peer credentials rather than a Team ID, and an appliance unpack path that builds tar arguments using Qt string splitting. A quote in the parent path injects –use-compress-program=, and macOS tar runs the attacker’s script as uid 0 [i.e., root].”
JFrog researcher reported CVE-2026-90894 to Parallels maker Alludo, which fixed it in Parallels Desktop v27.0.0, released at the beginning of September 2026.
Two weeks later, they published the technical details, but not the one-liner proof-of-concept script they developed.
Marvchick advised organizations to pinpoint every Mac that is running Parallels Desktop, lock down local accounts running on these hosts, and upgrade to a fixed Parallels version (27.0.0 or higher).

Subscribe to our breaking news e-mail alert to never miss out on the latest breaches, vulnerabilities and cybersecurity threats. Subscribe here!
Text extracted automatically; images, tables and formatting may be missing. Original: https://www.helpnetsecurity.com/2026/09/16/parallels-desktop-cve-2026-90894-parashells-vulnerability/