DOJ regrets the error on OPM
Full article762 words · extracted from cyberscoop.com · click to collapse
Get our latest cybersecurity news first on Google.
DOJ as apologized for confusion over its announcement last month that a fraudster used information stolen in the infamous 2015 OPM data breach.
The Department of Justice has apologized for confusion over its announcement last month that a fraudster used information stolen in the infamous 2015 Office of Personnel Management breach — an episode that confounded lawmakers and ran counter to publicly available information on the breach.
The confusion began after DOJ announced on June 18 that a Maryland woman had pleaded guilty to using stolen OPM data to get car and personal loans. The public assumption had been – and still is – that Chinese hackers had stolen the data for espionage purposes.
But DOJ now says that it hasn’t yet determined whether the woman and her accomplice got the data from the OPM breach or somewhere else.
After an internal review, the U.S. Attorney’s Office for the Eastern District of Virginia appended a statement to its press release saying that “numerous victims” of the fraud self-identified as victims of the OPM breach. “The government continues to investigate the ultimate source of the [personally identifiable information] used by the defendants” and how it was obtained, the statement said.
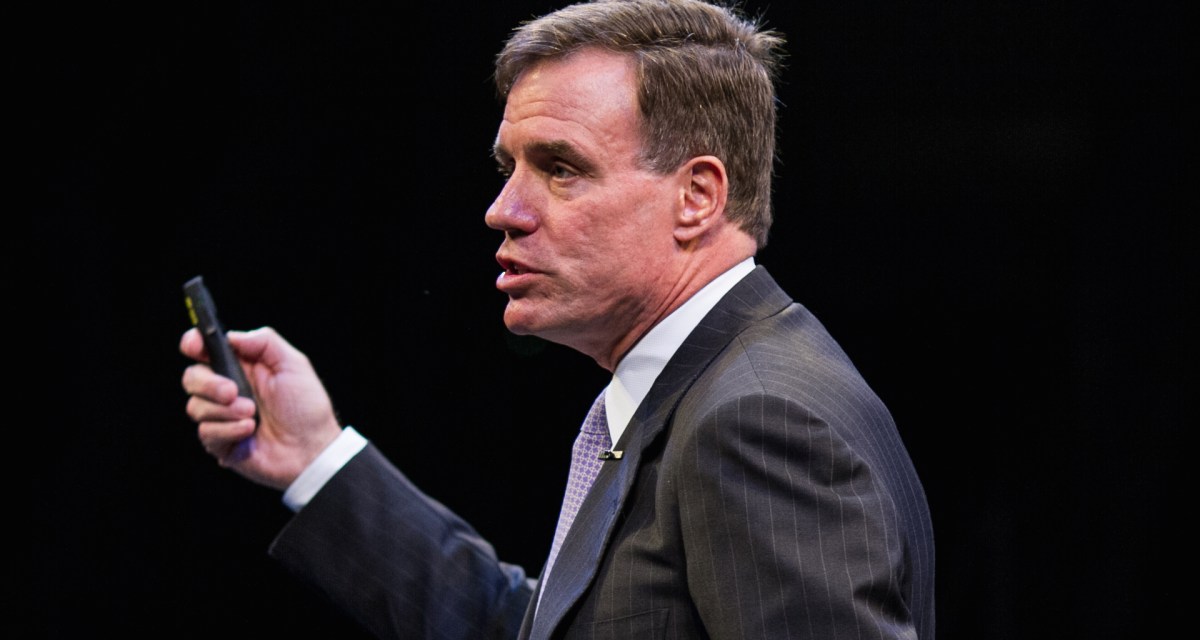
Puzzled how the data might have ended up in American scammers’ hands, Sen. Mark Warner, D-Va., and Rep. Gerry Connolly, D-Va., wrote to DOJ and OPM demanding answers.
In a response Monday to Warner, Assistant Attorney General Stephen E. Boyd said the investigation has not yet determined exactly how the victims’ data was exposed and “whether it can, in fact, be sourced directly to the OPM data breach.”
“Because the victims in this case had other things in common in terms of employment and location, it is possible that their data came from another common source,” Boyd added.
“Regrettably,” Boyd continued, the original DOJ press release “implied a premature conclusion that the exclusive and known source of the stolen identities used in the [fraud case] was the OPM data breach.”
“We apologize for the confusion,” he wrote.
In a statement to CyberScoop, a spokesperson for Warner said the senator is “pleased that DOJ has clarified the initial announcement, which led to significant, and apparently unneeded, anxiety for millions of victims of the OPM breach.”
You can read the full letter from Boyd to Warner below.
[documentcloud url=”http://www.documentcloud.org/documents/4594013-2018-7-9-Stole-Identification-Langley-Federal.html” responsive=true height=500]
More Scoops

Lawmakers spring to save ID theft services for OPM breach victims, with expiration looming
Sen. Mark Warner, D-Va., and Del. Eleanor Holmes Norton, D-D.C., hope to make the services permanent before they end next month.
Lawmakers fear Elon Musk, DOGE not adhering to privacy rules
The long, bumpy road to cyber incident reporting legislation — and the one still ahead
Latest Podcasts
Government
FBI officials say AI is bolstering adversaries, emphasizing need to focus on cyber basics, patching
Feds accuse China of ‘systematic’ distillation of U.S. AI models
CIA’s Michael Ellis says cyber intelligence is changing how the agency operates
The G7 tells industry to hurry up and prep for post-quantum encryption
Technology
Threats
Microsoft discloses two actively exploited zero-days among 974 vulnerabilities
Russian national extradited to US for alleged involvement in bank-account takeover scheme
Attackers exploit zero-days in consistently besieged SonicWall product
Jail time for Maine child in 764 marks turning point in federal law enforcement
Policy
Whistleblower says USPS deploying new, ‘untested’ IT systems governing mail-in ballots
‘Watershed 250’ test program in Texas looks to private sector for water cybersecurity help
Former sexual abuse victims say Grok used their images, videos to train deepfake capabilities
Cyber threats nudge Trump to sign executive order on foreign equipment in U.S. energy infrastructure
Text extracted automatically; images, tables and formatting may be missing. Original: https://cyberscoop.com/doj-regrets-error-opm-linked-fraud-case/