FireEye says hackers stole its red-team tools, suggests state
Full article774 words · extracted from cyberscoop.com · click to collapse
Get our latest cybersecurity news first on Google.
Microsoft and the FBI are also investigating the breach of one of the most influential security firms in the world.
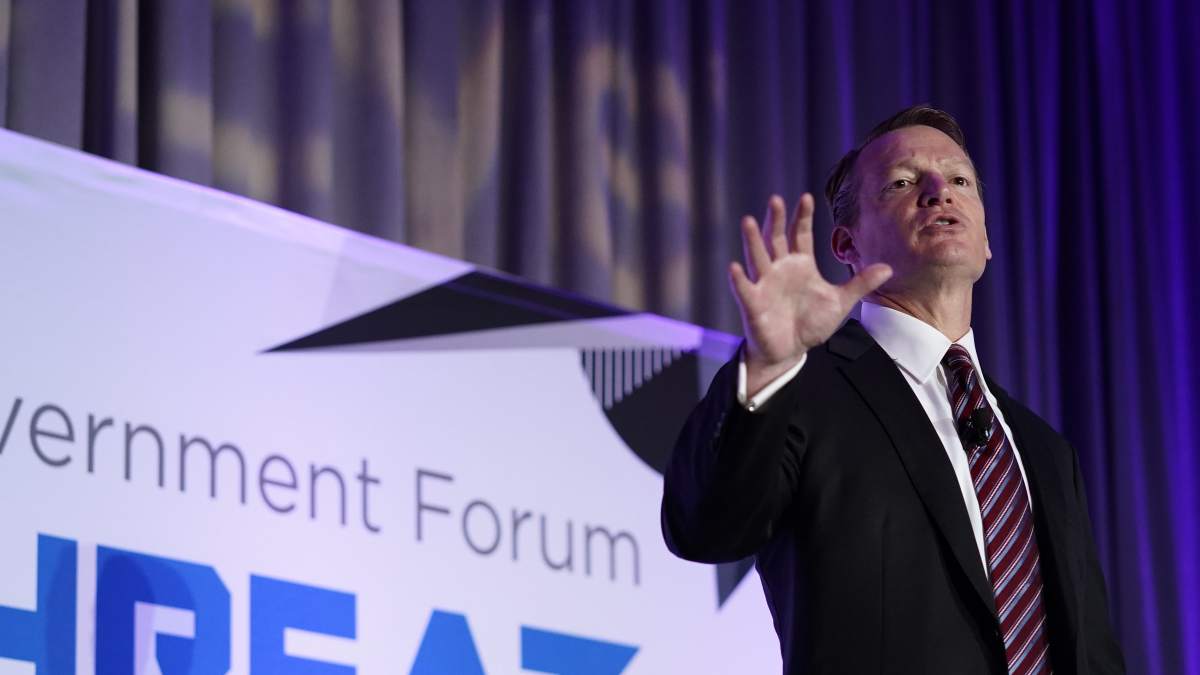
FireEye, one of the most influential cybersecurity companies in the world, on Tuesday revealed that it had been breached by a suspected state-sponsored hacking group.
FireEye CEO Kevin Mandia said that the FBI and security experts at Microsoft were helping investigate the incident, in which attackers accessed the tools FireEye uses to simulate attacks against clients. “Their initial analysis supports our conclusion that this was the work of a highly sophisticated state-sponsored attacker utilizing novel techniques,” Mandia said in a blog post.
Attackers stole so-called red team tools, which security firms use to imitate real-world hacks on behalf of their clients. Such red team tools from a respected firm like FireEye would provide malicious attackers with a kind of roadmap on how to subvert defenses, and breach victims.
The hackers who broke into FireEye’s network “primarily sought information related to certain government customers,” Mandia said.
The FireEye chief executive said his firm was taking the extraordinary step of developing “more than 300 countermeasures for our customers, and the community at large, to use in order to minimize the potential impact of the theft of these tools.”
FireEye did not identify a culprit in the breach. The company’s clients include Fortune 500 companies around the world. Any number of foreign intelligence services could find value in having access to FireEye’s security tools to probe target organizations in the public and private sectors.
“The FBI is investigating the incident and preliminary indications show an actor with a high level of sophistication consistent with a nation-state,” Matt Gorham, assistant director of the FBI Cyber Division, said in a statement. It is a rare case of the FBI commenting on an ongoing investigation.
The company is known for attributing attacks from suspected Russian, Chinese and North Korean hackers, among other groups. The firm is often called in to investigate high profile data breaches, like the 2014 breach against Sony Pictures.
The breach is reminiscent, in part, of the theft of hacking tools from the National Security Agency, which a mysterious group called the Shadow Brokers began leaking in 2016. Those tools were subsequently used in high-profile cyberattacks, such as the WannaCry ransomware attack.
Dmitri Alperovitch, co-founder and former CTO of cybersecurity company CrowdStrike, pointed out that major security firms are frequent targets of state-linked hackers.
With the Fireeye breach news coming out, it's important to remember that no one is immune to this. Many security companies have been successfully compromised over the years, including Symantec, Trend, Kaspersky, RSA and Bit9 1/
— Dmitri Alperovitch (@DAlperovitch) December 8, 2020
The response from Capitol Hill was swift.
Rep. Adam Schiff, D-Calif., chairman of the House Intelligence Committee, said he had asked intelligence agencies to brief his panel on the FireEye hack, including “any vulnerabilities that may arise from it and actions to mitigate the impacts.”
Sen. Mark Warner, D-Va., vice chairman of the Senate Intelligence Committee, said the incident “shows the difficulty of stopping determined nation-state hackers.”
“As we have with critical infrastructure, we have to rethink the kind of cyber assistance the government provides to American companies in key sectors on which we all rely,” Warner added.
Latest Podcasts
Government
FBI officials say AI is bolstering adversaries, emphasizing need to focus on cyber basics, patching
Feds accuse China of ‘systematic’ distillation of U.S. AI models
CIA’s Michael Ellis says cyber intelligence is changing how the agency operates
Jail time for Maine child in 764 marks turning point in federal law enforcement
Technology
Threats
Chinese espionage groups swarm to exploit triple-link chain of zero-days
Microsoft discloses two actively exploited zero-days among 974 vulnerabilities
Russian national extradited to US for alleged involvement in bank-account takeover scheme
Attackers exploit zero-days in consistently besieged SonicWall product
Policy
Whistleblower says USPS deploying new, ‘untested’ IT systems governing mail-in ballots
‘Watershed 250’ test program in Texas looks to private sector for water cybersecurity help
Former sexual abuse victims say Grok used their images, videos to train deepfake capabilities
Cyber threats nudge Trump to sign executive order on foreign equipment in U.S. energy infrastructure
Text extracted automatically; images, tables and formatting may be missing. Original: https://cyberscoop.com/fireeye-says-hackers-stole-its-red-team-tools-suggests-state-sponsored-group-is-to-blame/