SEC reveals 2016 breach that may have led to insider trading
Full article521 words · extracted from cyberscoop.com · click to collapse
Get our latest cybersecurity news first on Google.
SEC chairman Jay Clayton said while the breach was detected last year, it wasn't until last month that the SEC suspected the hackers used the compromised information for insider trading.
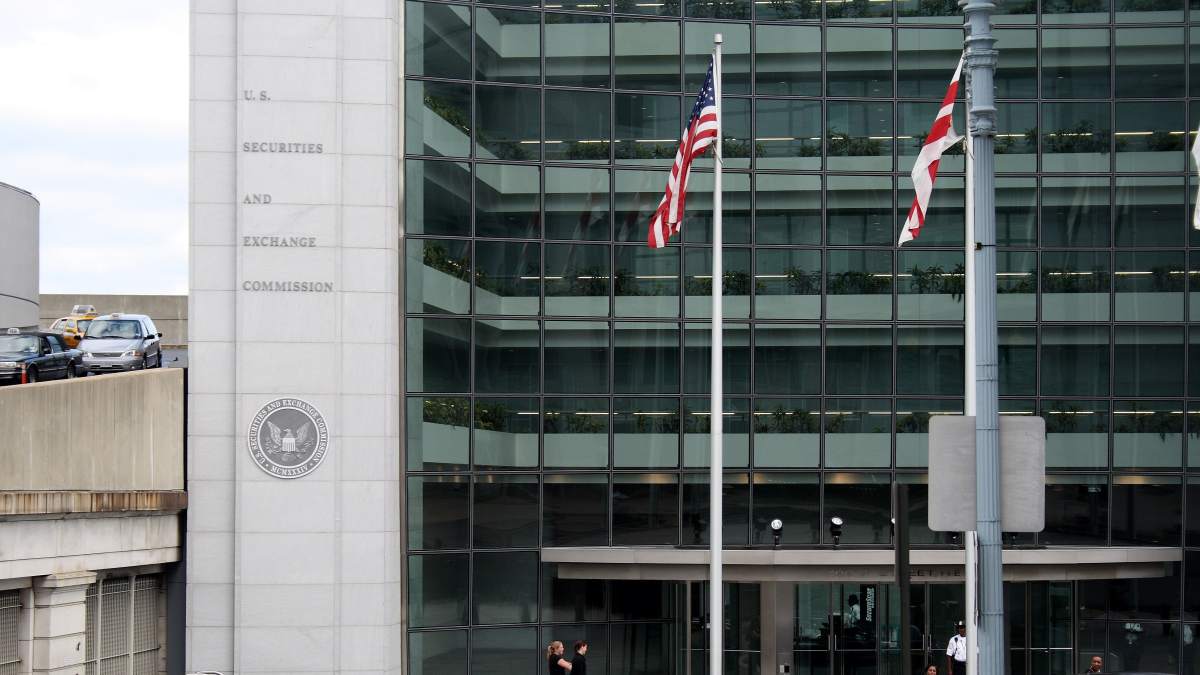
The Securities and Exchange Commission revealed Wednesday that a database housing detailed financial reports was breached last year.
SEC chairman Jay Clayton said in a statement that while the breach was detected last year, it wasn’t until last month that the SEC suspected the hackers used the compromised information for insider trading.
Clayton’s comments “underscore the daunting reality that the Securities and Exchange Commission and other entities that store nonpublic corporate information face,” said Marcus Christian, a former prosecutor at the U.S. Attorney’s Office for the Southern District of Florida. “They have imperfect security but must defend against persistent and sophisticated actors.”
The compromised database is known as EDGAR (Electronic Data Gathering, Analysis, and Retrieval) and stores sensitive corporate disclosures that are not yet available to the public. That kind of information can give traders an unfair and illegal advantage if it is used for stock trading.
“Specifically, a software vulnerability in the test filing component of our EDGAR system, which was patched promptly after discovery, was exploited and resulted in access to nonpublic information,” the Clayton said.
The SEC doesn’t believe that the breach disrupted its operations or gave hackers access to personal information.
The revelation came in brief part of a statement released Wednesday about the commission’s cybersecurity policy. The statement did not give a reason why the breach wasn’t announced sooner.
“At this point, it is not clear how widespread hacking/trading schemes are, but concerns that they could undermine market confidence are growing,” Christian said. “The biggest threat to markets is likely not the crimes that we are seeing; the worry is that we are only seeing the tip of the iceberg.”
Latest Podcasts
Government
FBI officials say AI is bolstering adversaries, emphasizing need to focus on cyber basics, patching
Feds accuse China of ‘systematic’ distillation of U.S. AI models
CIA’s Michael Ellis says cyber intelligence is changing how the agency operates
The G7 tells industry to hurry up and prep for post-quantum encryption
Technology
Threats
Chinese espionage groups swarm to exploit triple-link chain of zero-days
Microsoft discloses two actively exploited zero-days among 974 vulnerabilities
Russian national extradited to US for alleged involvement in bank-account takeover scheme
Attackers exploit zero-days in consistently besieged SonicWall product
Policy
Whistleblower says USPS deploying new, ‘untested’ IT systems governing mail-in ballots
‘Watershed 250’ test program in Texas looks to private sector for water cybersecurity help
Former sexual abuse victims say Grok used their images, videos to train deepfake capabilities
Cyber threats nudge Trump to sign executive order on foreign equipment in U.S. energy infrastructure
Text extracted automatically; images, tables and formatting may be missing. Original: https://cyberscoop.com/sec-data-breach-insider-trading/