DHS CISO joins call for an 18F for cybersecurity
Full article610 words · extracted from cyberscoop.com · click to collapse
Get our latest cybersecurity news first on Google.
Department of Homeland Security CISO Jeff Eisensmith said the federal government needs to establish something similar to the GSA government tech startup.
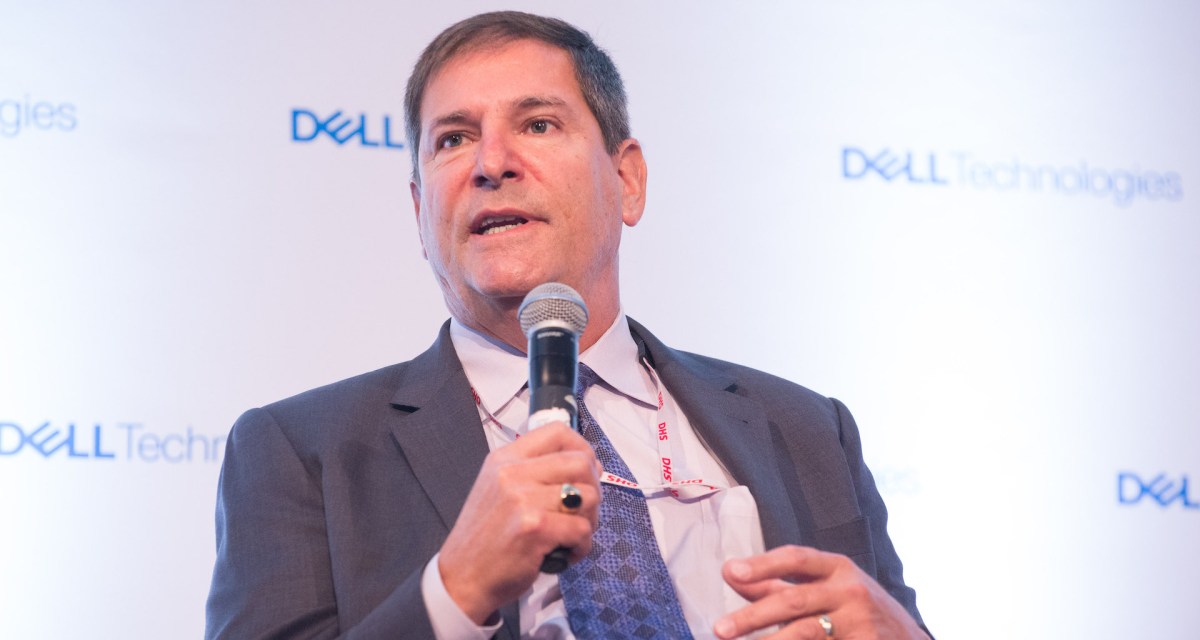
The federal government should establish a dedicated team of star performers poached from the private sector along the lines of the General Services Administration’s government technology startup 18F, Department of Homeland Security CISO Jeff Eisensmith said Thursday.
“We need to do the same thing we did with 18F and push that deeper into the cybersecurity realm,” he told CyberScoop in a brief interview after his panel discussion at the Dell Technologies’ Digital Transformation Summit produced by FedScoop.
“18F brought higher pay and prestige” to government service, he said. “They recruited hard in high tech areas. That whole paradigm could work” in cybersecurity.
Eisensmith’s call echoes one issued last year by 18F founder Greg Godbout. “It would be really great to have a consultant service in government similar to an 18F or US [Digital Service] model … that’s built around cybersecurity,” Godbout told FedScoop in May last year, about a month after he left his last federal post as Environmental Protection Agency’s CTO.
This year, the call made its way into a proposed “to-do” list for the new administration.
“Congress should direct the GSA to establish an office that collaborates with other agencies on cybersecurity issues, bringing in top private-sector talent to improve government security,” said the Information Technology and Innovation Foundation in its “Tech Policy To-Do List” in April.
Eisensmith also called Thursday for agencies to be allowed to expand their cybersecurity headcount, even if it meant they were adding positions faster than they could hire to fill them. In most occupational fields in government there tends to be a proportion of posts vacant at any given time because of how long it can take to recruit and onboard new employees. But Eisensmith said the problem was especially acute in cybersecurity — because of the turnover of staff, sometimes called “thrash” in government circles.
“With the thrash and the changeout of skilled talent, cybersecurity needs a larger buffer” of unfilled posts, he said, to ensure there were enough staff to fulfill the mission.
The looming workforce crisis — with an ever growing number of employers chasing a stagnant pool of cybersecurity workers — “is happening quickly,” he said, “and it’s not getting better, it’s getting worse.”
Latest Podcasts
Government
FBI officials say AI is bolstering adversaries, emphasizing need to focus on cyber basics, patching
Feds accuse China of ‘systematic’ distillation of U.S. AI models
CIA’s Michael Ellis says cyber intelligence is changing how the agency operates
The G7 tells industry to hurry up and prep for post-quantum encryption
Technology
Threats
Chinese espionage groups swarm to exploit triple-link chain of zero-days
Microsoft discloses two actively exploited zero-days among 974 vulnerabilities
Russian national extradited to US for alleged involvement in bank-account takeover scheme
Attackers exploit zero-days in consistently besieged SonicWall product
Policy
Whistleblower says USPS deploying new, ‘untested’ IT systems governing mail-in ballots
‘Watershed 250’ test program in Texas looks to private sector for water cybersecurity help
Former sexual abuse victims say Grok used their images, videos to train deepfake capabilities
Cyber threats nudge Trump to sign executive order on foreign equipment in U.S. energy infrastructure
Text extracted automatically; images, tables and formatting may be missing. Original: https://cyberscoop.com/dhs-ciso-calls-cybersecurity-18f/