Senator asks Department of Justice if it can keep a lid on its software exploits
Full article707 words · extracted from cyberscoop.com · click to collapse
Get our latest cybersecurity news first on Google.
Sen. Ron Wyden is asking what law enforcement agencies are doing to protect their hacking tools from foreign spies.
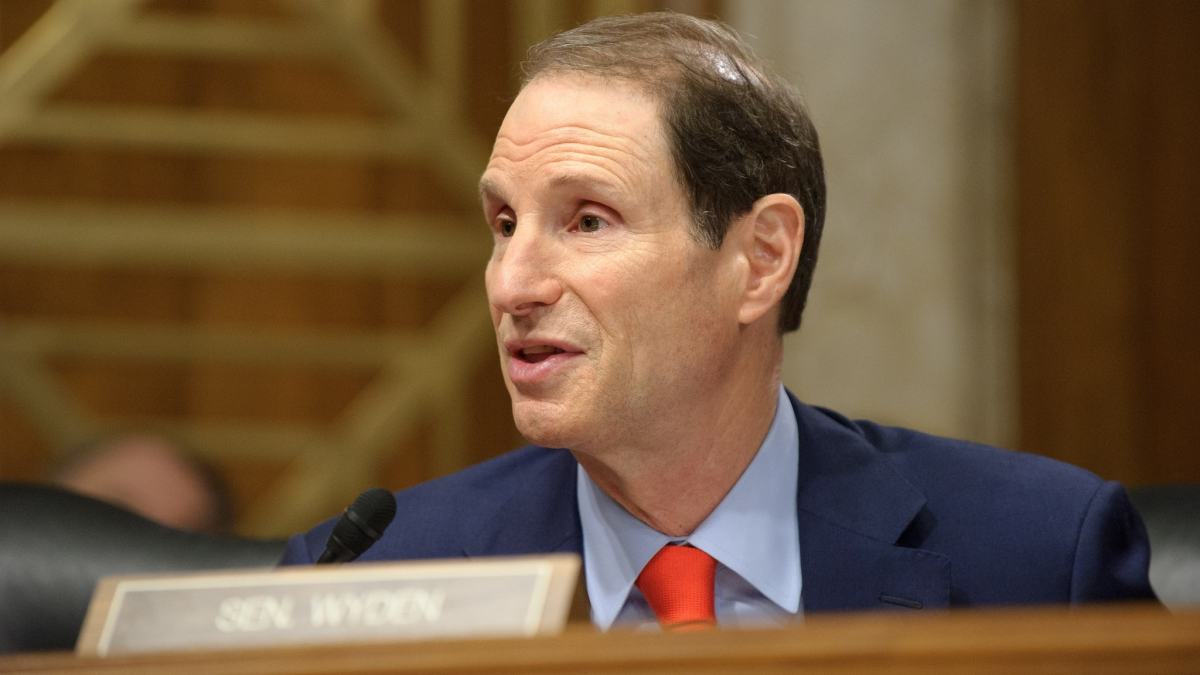
In recent years, Department of Justice agencies have quietly acquired and deployed hacking tools in support of their law enforcement mission. A handful of high-profile cases have brought greater scrutiny to those efforts, most notably in 2016 when the FBI used a contractor to crack the San Bernardino shooter’s iPhone.
Now, a senator is asking Attorney General William Barr for a more thorough accounting of what law enforcement agencies are doing to protect these software exploits from foreign intelligence agencies and other adversaries.
“Just as the American people expect the government to protect its nuclear, chemical, and biological weapons, so too do Americans expect that the government will protect its cyber arsenal from theft by hackers and foreign spies,” Sen. Ron Wyden, D-Ore., wrote to Barr in a letter dated June 5.
In particular, the department has invested heavily in tools to break encrypted communications, as top law enforcement officials have lamented the ability of criminals to “go dark.” Transnational crime networks “increasingly rely on encrypted communications to plan and commit crimes, thus forcing the FBI to develop sophisticated technology and methods to disrupt their activities and dismantle their organizations,” the FBI said in its fiscal 2020 budget request.
Wyden wants to know if the department’s software exploits have ever ended up in an adversary’s hands, whether through a security breach or discovery in the wild. The senator asked if any foreign companies had developed offensive cyber-capabilities for law enforcement agencies and, if so, whether those tools communicate with computer servers overseas.
Like any digital asset that is a target of attackers, hacking kits and the infrastructure that support them can benefit from rigorous “red teaming” tests that emulate adversary techniques. Wyden wants to know if Justice’s exploit-writing contractors are subject to such tests, and whether they are required to use best cybersecurity practices suggested by the Department of Homeland Security and the National Institute of Standards and Technology.
The Washington Post was first to report on the letter, which you can read below. Wyden asked for answers from Barr by July 12. A Justice Department spokesman said the department received the letter and would respond accordingly.
[documentcloud url=”http://www.documentcloud.org/documents/6143688-Wyden-Letter-to-Barr.html” sidebar=false]
More Scoops
Lawmakers ponder terrorism designations, homicide charges over hospital ransomware attacks
The ideas came up at a House Homeland Security Committee hearing, as health care ransomware attacks are on the rise.
Exclusive: Senator calls on Commerce to tighten proposed rules on exporting surveillance, hacking tech to problematic nations
Senator slams U.S. courts agency for ‘stonewalling’ inquiry into cyberattack
Latest Podcasts
Government
FBI officials say AI is bolstering adversaries, emphasizing need to focus on cyber basics, patching
Feds accuse China of ‘systematic’ distillation of U.S. AI models
CIA’s Michael Ellis says cyber intelligence is changing how the agency operates
The G7 tells industry to hurry up and prep for post-quantum encryption
Technology
Threats
Microsoft discloses two actively exploited zero-days among 974 vulnerabilities
Russian national extradited to US for alleged involvement in bank-account takeover scheme
Attackers exploit zero-days in consistently besieged SonicWall product
Jail time for Maine child in 764 marks turning point in federal law enforcement
Policy
Whistleblower says USPS deploying new, ‘untested’ IT systems governing mail-in ballots
‘Watershed 250’ test program in Texas looks to private sector for water cybersecurity help
Former sexual abuse victims say Grok used their images, videos to train deepfake capabilities
Cyber threats nudge Trump to sign executive order on foreign equipment in U.S. energy infrastructure
Text extracted automatically; images, tables and formatting may be missing. Original: https://cyberscoop.com/department-of-justice-hacking-tools-ron-wyden-letter/