NSA: 'We know we need to do some work' on declassifying threat intel
Full article822 words · extracted from cyberscoop.com · click to collapse
Get our latest cybersecurity news first on Google.
NSA's Anne Neuberger told the audience at CyberTalks the process needs to be refined.
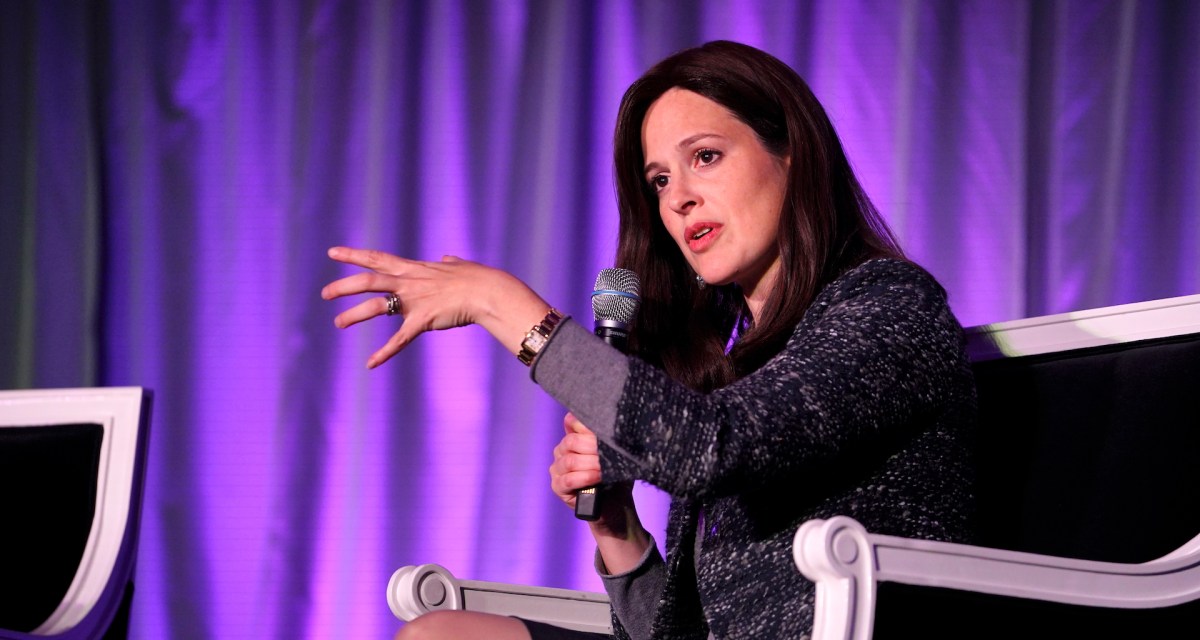
One of the National Security Agency’s newly minted Cybersecurity Directorate’s goals is to quickly share information on adversarial threats with the private sector — but the process for doing that needs to be refined, the directorate’s leader said Thursday.
“The process in place today is where we know we need to do some work,” Anne Neuberger said while speaking at CyberTalks, produced by CyberScoop. “When we find indications of a threat, we see planning to execute a particular operation, or we see the operation being executed. [But] because we learn about it in a classified way, we treat it as classified.”
Part of the difficulty the NSA faces is that adversaries often run operations and then discard their compromised infrastructure, making a protracted declassification process nearly useless since “indicators of compromise pretty much they have a ticking time clock for how useful they are,” Neuberger said.
The new directorate, which started operations earlier this month, is measuring success by examining how well it is able to prevent attacks moving forward.
“Have we used threat intelligence, have we used security guidelines, have we … worked with the network owner?” are the questions the NSA needs to be asking itself moving forward, Neuberger said.
It’s not clear what specific metrics the NSA will use to determine whether the new directorate is successful, but Neuberger said the unit will be asking government partners whether it has made a difference in their security.
DHS and NSA coordination
Inevitably, deciding who will talk with the private sector about nation-state threats — NSA or the Department of Homeland Security — will involve the DHS’s Cybersecurity and Infrastructure Security Agency, given that the intelligence agency’s authorities don’t pertain to critical infrastructure, CISA Director Chris Krebs told reporters at CyberTalks.
“By its very nature, Title 50 organizations should not be really researching and understanding how American critical infrastructure works. That’s my job — working with Treasury [Department], working with [the Department of] Energy,” Krebs said. Title 50 is the part of U.S. Code that covers intelligence agencies.
It may make sense for the NSA to take point and work directly with the private sector if the agency has interest in a specific threat, Krebs said.
But on critical infrastructure and threats to U.S. elections, Krebs thinks DHS should take the reins.
“In the traditional critical infrastructure spaces, we would look to take the lead … based on our relationships, based on our understanding of how to work with those folks,” Krebs said. “Since we have the relationship with the state and local election officials we think it’s probably most effective right now that we help harness various [intelligence] pieces and then put it in the hands of the network defenders in the local election jurisdictions.”
More Scoops
The push to designate AI as the next critical infrastructure sector
The designation would unlock a range of federal services, tools and resources for an industry that policymakers view as increasingly tied to national and economic security.
AI-fueled attacks pose ‘active threat’ to water, other sectors, U.S. agencies warn
Trump blames Minnesota for cyberattacks on water sector, drawing pushback from cyber world
Latest Podcasts
Government
FBI officials say AI is bolstering adversaries, emphasizing need to focus on cyber basics, patching
Feds accuse China of ‘systematic’ distillation of U.S. AI models
CIA’s Michael Ellis says cyber intelligence is changing how the agency operates
The G7 tells industry to hurry up and prep for post-quantum encryption
Technology
Threats
Chinese espionage groups swarm to exploit triple-link chain of zero-days
Microsoft discloses two actively exploited zero-days among 974 vulnerabilities
Russian national extradited to US for alleged involvement in bank-account takeover scheme
Attackers exploit zero-days in consistently besieged SonicWall product
Policy
Whistleblower says USPS deploying new, ‘untested’ IT systems governing mail-in ballots
‘Watershed 250’ test program in Texas looks to private sector for water cybersecurity help
Former sexual abuse victims say Grok used their images, videos to train deepfake capabilities
Cyber threats nudge Trump to sign executive order on foreign equipment in U.S. energy infrastructure
Text extracted automatically; images, tables and formatting may be missing. Original: https://cyberscoop.com/anne-neuberger-nsa-threat-intelligence-cyber-talks-2019/