Cabir, the star of the show
Full article332 words · extracted from securelist.com · click to collapse



Tomorrow will be the last day of CeBIT and everyone’s extremely busy. We still found the time to visit the Physikalisch-Technische Bundesanstalt (the national meteorology institute providing scientific and technical services) in Braunschweig together with a German TV crew.
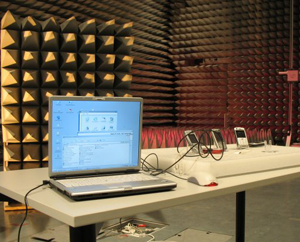
And why did we go there? Although the room may look like a big recording studio, the spikes on the wall aren’t to ensure clean sound, but to disperse all radio waves inside the room. Additionally, the metal plated walls and floor create a Faraday cage, making sure that all waves stay inside the room. In short, it’s a perfect location for mobile malware testing.
This gave us the opportunity to show the cameras just how Cabir, the first known smartphone virus, spreads. There are only a few known cases of Cabir infections in the wild in Germany, but everyone in the room understood that mobile malware is a real threat.
The chances of getting infected in your home country may be low. But there are other regions – like parts of Asia – where Cabir is more widespread. And that’s why we never tire of repeating the security professionals mantra: never install a program on your mobile phone if you’re not sure where it came from, and if you don’t need Bluetooth, turn it off! Even (or perhaps especially) at CeBIT.
Latest Webinars
Reports
Kaspersky researchers have discovered new Mirage Kitten attacks using previously undocumented malware families: NodeRabbit in Node.js and PollCat in JavaScript.
Our experts discovered a new CoolClient backdoor variant with a kernel-mode rootkit driver that hides malicious processes, files, and network connections from security tools and threat analysts.
Kaspersky experts break down a new Armored Likho campaign that poses as a fundraising efforts and delivers a new Still Toolkit aimed at stealing Telegram data and eavesdropping on victims.
Kaspersky researchers reveal previously undocumented malware attributed to Mirage Kitten (UNC1549, Smoke Sandstorm, Nimbus Manticore): NightLedger backdoor, ArcBridge, and BridgeHead tunneling tools.
Text extracted automatically; images, tables and formatting may be missing. Original: https://securelist.com/cabir-the-star-of-the-show/30308/