After ‘significant’ malware attack, U.S. Coast Guard issues maritime security advisory
Full article738 words · extracted from cyberscoop.com · click to collapse
Get our latest cybersecurity news first on Google.
The alert comes after the FBI warned private industry about growing cybersecurity risks for vessels, amid ongoing international tensions.
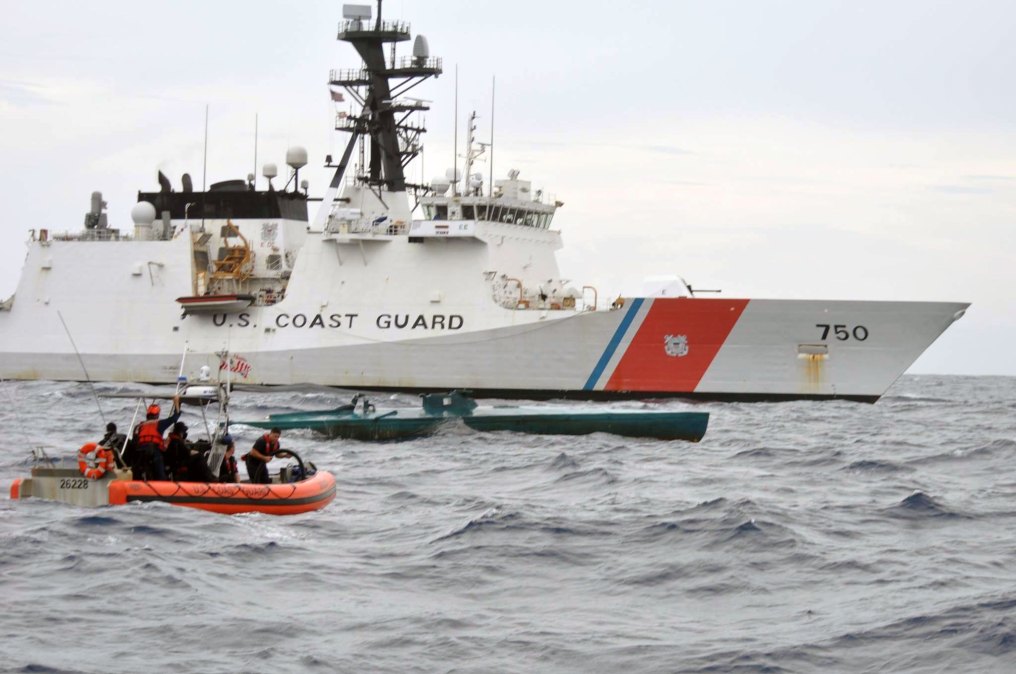
The U.S. Coast Guard has issued a safety alert encouraging mariners to follow basic cybersecurity protocols after a ship bound for the East Coast experienced a “significant cyber incident” in February.
The Coast Guard said the deep draft ship was traveling to the Port of New York and New Jersey from international waters earlier this year when it experienced an incident affecting its shipboard network. An interagency team of specialists responded, finding that “malware significantly degraded the functionality of the onboard computer system,” though the boat’s essential controls were not affected, the Coast Guard said Monday. The shipboard network had been used to conduct official business, like updating electronic charts, managing cargo information and communicating with onshore resources.
The warning comes as maritime traffic has become a prominent venue for ongoing tensions between Iran and Saudi Arabia and its allies, including the United States. In March, the FBI privately notified industry of cyberthreats to U.S. commercial and military vessels.
“Adversarial nations and non-state cyber actors routinely use various social media platforms to develop male and female false online personas to attempt to socially engineer targets of interest,” states the FBI advisory obtained by CyberScoop. “Often individuals aboard maritime vessels will unwittingly provide information about their vessels’ location or activities to the false personas under the guise of an intimate online relationship.”
That information, the FBI warned, can be used to track vessels and carry out physical attacks. The FBI also highlighted the fact that hackers could target automated systems to track ship movements.
Cybersecurity advice for vessels
The Coast Guard‘s safety advisory encourages vessel operators to segment their networks to make it more difficult for hackers to travel through breached systems. The notice also stresses the need for every employee to have their own password to the ship’s network, as well as the need basic antivirus software and a plan for installing security updates.
While the advisory doesn’t explain exactly what happened on the ship’s network, the Coast Guard also advised ship personnel to be wary of external media.
“This incident revealed that it is common practice for cargo data to be transferred at the pier, via a USB drive,” the Coast Guard said. “Those USB drives were routinely plugged directly into the ship’s computers without prior scanning for malware. It is critical that any external media is scanned for malware on a standalone system before being plugged into any shipboard network. Never run executable media from an untrusted source.”
The Coast Guard did not provide any information in the advisory about who may have been behind the hack.
Cybersecurity vulnerabilities are an issue for much of the maritime industry. While much of the public attention has focused on possible GPS interference, cargo shipping undergirds trade of more than $4 trillion worth of goods for the U.S. annually, according to the World Shipping Council. Such a large figure, combined with invaluable location data, and possible third-party entry points into influential global companies, would entice cybercriminals and state-sponsored hackers alike.
Sean Lyngaas contributed reporting to this story.
Latest Podcasts
Government
FBI officials say AI is bolstering adversaries, emphasizing need to focus on cyber basics, patching
Feds accuse China of ‘systematic’ distillation of U.S. AI models
CIA’s Michael Ellis says cyber intelligence is changing how the agency operates
The G7 tells industry to hurry up and prep for post-quantum encryption
Technology
Threats
Chinese espionage groups swarm to exploit triple-link chain of zero-days
Microsoft discloses two actively exploited zero-days among 974 vulnerabilities
Russian national extradited to US for alleged involvement in bank-account takeover scheme
Attackers exploit zero-days in consistently besieged SonicWall product
Policy
Whistleblower says USPS deploying new, ‘untested’ IT systems governing mail-in ballots
‘Watershed 250’ test program in Texas looks to private sector for water cybersecurity help
Former sexual abuse victims say Grok used their images, videos to train deepfake capabilities
Cyber threats nudge Trump to sign executive order on foreign equipment in U.S. energy infrastructure
Text extracted automatically; images, tables and formatting may be missing. Original: https://cyberscoop.com/coast-guard-significant-malware-attack/