CISA used new subpoena power to contact US companies vulnerable to hacking
Full article614 words · extracted from cyberscoop.com · click to collapse
Get our latest cybersecurity news first on Google.
It’s an authority the agency has long sought as CISA officials struggled to communicate with some vendors .
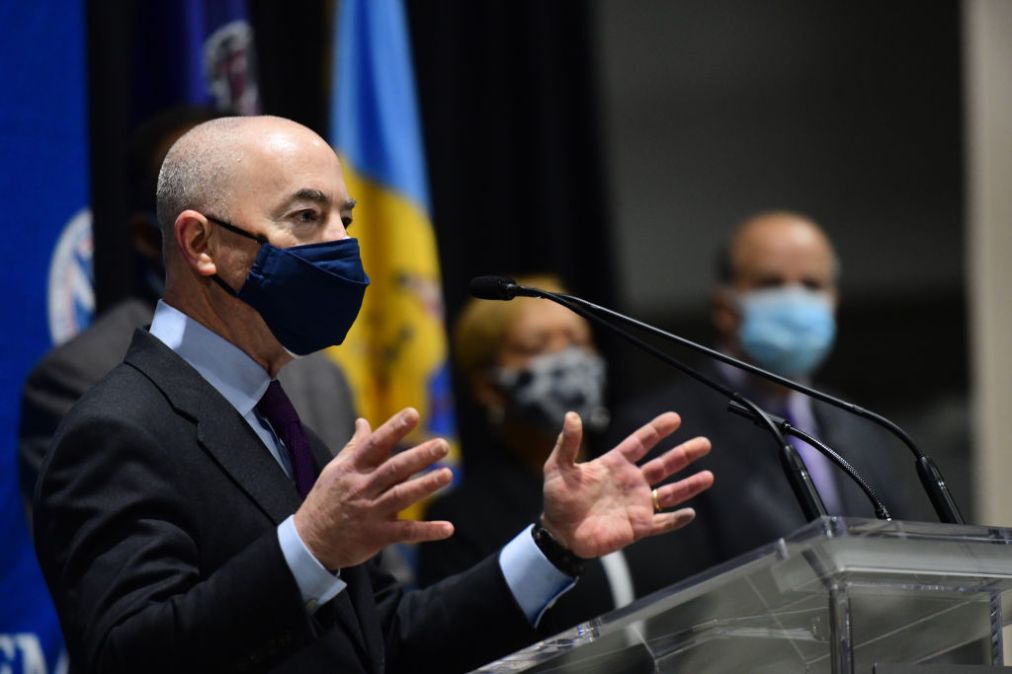
The Department of Homeland Security’s cybersecurity agency used a new subpoena power for the first time last week to contact at least one U.S. internet service provider with customers whose software is vulnerable to hacking.
It’s an authority that DHS’s Cybersecurity and Infrastructure Security Agency has long sought, as agency officials struggled to communicate with some technology firms before flaws in their equipment became public and risked exploitation by state-linked or criminal hackers.
Congress granted CISA the subpoena power in a bill that became law in January, allowing the agency to obtain a list of an internet service provider’s vulnerable customers and notify them directly rather than relying on third party communication.
CISA issued two such subpoenas last week, acting agency director Brandon Wales said. A CISA spokesperson declined to say which U.S. company or companies had been subpoenaed, or whether the vulnerabilities pertained to an ongoing hacking campaign.
“The information sought will allow CISA to identify and contact critical infrastructure entities with specific security vulnerabilities exposed on the open internet,” Wales said in a statement.
It’s a key step for an agency that the Biden administration and lawmakers want to bolster with more money and authorities. The urgency comes amid the fallout of suspected Russian and Chinese hacking campaigns that have roiled the government and private sector. The Russian cyber-espionage effort, which exploited software made by federal contractor SolarWinds and other vendors, has led agency officials to reassess CISA’s tools for detecting and mitigating hacking threats.
“Our government got hacked last year and we didn’t know about it for months,” Homeland Security Secretary Alejandro Mayorkas said in March.
The White House has asked Congress for an additional $110 million for DHS’s cybersecurity work for the 2022 fiscal year, compared to the previous year, on top of a $650 million boost that CISA received from the coronavirus relief package.
Reps. Jim Langevin, D-R.I., and Mike Gallagher, R-Wisc., are also asking House appropriators to make $400 million in additional funding available for CISA’s 2022 budget.
“CISA’s new subpoena authority has empowered the agency to notify vulnerable entities before they’re hacked, rather than waiting until they are already victims,” said Langevin, who advocated for the new authority.
Latest Podcasts
Government
FBI officials say AI is bolstering adversaries, emphasizing need to focus on cyber basics, patching
Feds accuse China of ‘systematic’ distillation of U.S. AI models
CIA’s Michael Ellis says cyber intelligence is changing how the agency operates
The G7 tells industry to hurry up and prep for post-quantum encryption
Technology
Threats
Chinese espionage groups swarm to exploit triple-link chain of zero-days
Microsoft discloses two actively exploited zero-days among 974 vulnerabilities
Russian national extradited to US for alleged involvement in bank-account takeover scheme
Attackers exploit zero-days in consistently besieged SonicWall product
Policy
Whistleblower says USPS deploying new, ‘untested’ IT systems governing mail-in ballots
‘Watershed 250’ test program in Texas looks to private sector for water cybersecurity help
Former sexual abuse victims say Grok used their images, videos to train deepfake capabilities
Cyber threats nudge Trump to sign executive order on foreign equipment in U.S. energy infrastructure
Text extracted automatically; images, tables and formatting may be missing. Original: https://cyberscoop.com/dhs-cyber-alert-subpoena-us/