What’s new from this year’s Counter Ransomware Initiative summit, and what’s next
Full article827 words · extracted from cyberscoop.com · click to collapse
Get our latest cybersecurity news first on Google.
Action plans, different kinds of meetings and more have all been in the mix, top administration officials told CyberScoop.
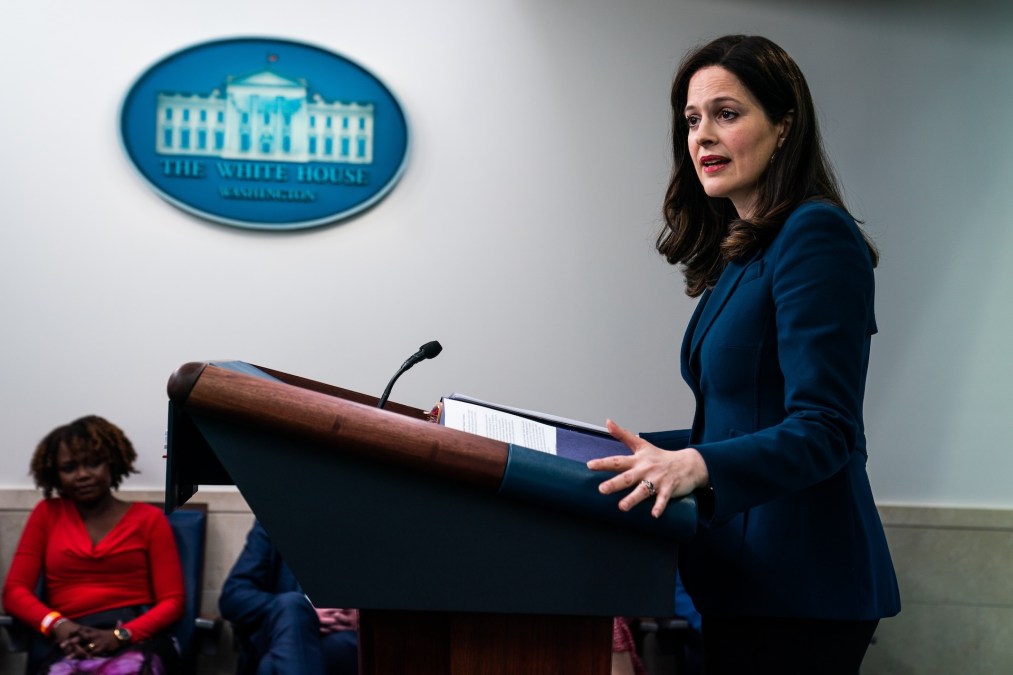
After trying some new approaches to the U.S.-led global Counter Ransomware Initiative this year, the international coalition is already laying the groundwork for next year’s agenda.
Thursday wrapped up meetings of the 68 countries with an optional capacity-building day to help those participating nations “get through practical skills,” Anne Neuberger, the deputy national security advisor for cyber and emerging technology, told CyberScoop.
It followed a series of huddles that featured one day focused on the intersection of artificial intelligence and cybersecurity. Another innovation this year, according to a senior administration official, was regional breakout sessions alongside topical breakout sessions. “The feedback we got from our members is that it really facilitated robust conversation,” the official said.
The initiative is taking a divide-and-conquer approach to action plans for 2025. Germany and Nigeria are leading the diplomacy and capacity-building pillar, Australia and Lithuania are leading the operational task force, Singapore and the U.K. are leading the policy pillar, Canada is leading the private sector advisory panel and the United States is serving as the overall chair, Neuberger said.
“In each country you have agencies doing work to address aspects of the problem,” Neuberger said. “What we’ve been doing is bringing all the tools together to be more effective, and what we bring into CRI is helping other countries do the same, and then bringing that united power of 68 member countries and international organizations against the problem.”
The White House isn’t the only part of the United States government involved that’s looking ahead.
“We must recruit more countries to our cause and encourage our partners to raise their minimum cybersecurity standards, especially for critical infrastructure like hospitals,” Richard Verma, the deputy secretary of State for management and resources, said during a speech Tuesday. “We have to become even more proactive in helping countries recover from major ransomware attacks.”
Neuberger has repeatedly highlighted how victims paying ransoms keeps ransomware gangs in business, and it’s something she discussed again this week.
It starts with trying to encourage organizations to be resilient from the start. “That’s goal number one that they’re working on to get companies to improve cybersecurity each and every day,” she told CyberScoop.
“The second piece of that is work we’re working to do with insurance companies. In some cases, insurance companies encourage paying ransom. In some cases, they reimburse for ransom,” she said.
“Every ransom payment, while it might seem like potentially the best thing for a given company to do, it fuels the broader ecosystem,” she continued. “So the messaging that CISA does, the messaging we do from the White House, discouraging it, are big parts of that. As you know, we’ve explored various policy options for stronger steps. We’re not going to be pursuing those at this time.”
The senior administration official said the guidance to victims produced from this year’s meetings was another way of trying to tackle ransom payments. The guidance “basically aims to reduce disruption in costs, the number of ransoms paid and the size of the ransom paid,” the official said.
“And it was developed in partnership with the insurance industries because we thought it was really important to get their input.” the official said. Wednesday’s event ended “with a call to action for the remaining CRI members to sign on and get the insurance industries and their respective jurisdictions to sign on as well.”
Latest Podcasts
Government
FBI officials say AI is bolstering adversaries, emphasizing need to focus on cyber basics, patching
CIA’s Michael Ellis says cyber intelligence is changing how the agency operates
The G7 tells industry to hurry up and prep for post-quantum encryption
Jail time for Maine child in 764 marks turning point in federal law enforcement
Technology
Threats
Chinese espionage groups swarm to exploit triple-link chain of zero-days
Microsoft discloses two actively exploited zero-days among 974 vulnerabilities
Russian national extradited to US for alleged involvement in bank-account takeover scheme
Attackers exploit zero-days in consistently besieged SonicWall product
Policy
Whistleblower says USPS deploying new, ‘untested’ IT systems governing mail-in ballots
‘Watershed 250’ test program in Texas looks to private sector for water cybersecurity help
Former sexual abuse victims say Grok used their images, videos to train deepfake capabilities
Cyber threats nudge Trump to sign executive order on foreign equipment in U.S. energy infrastructure
Text extracted automatically; images, tables and formatting may be missing. Original: https://cyberscoop.com/counter-ransomware-initiative-summit-whats-next/