Google finds Indian hack-for-hire firms exploiting coronavirus fears via spearphishing schemes
Full article897 words · extracted from cyberscoop.com · click to collapse
Get our latest cybersecurity news first on Google.
Indian hack-for-hire firms are impersonating the World Health Organization in spearphishing email campaigns, according to Google.
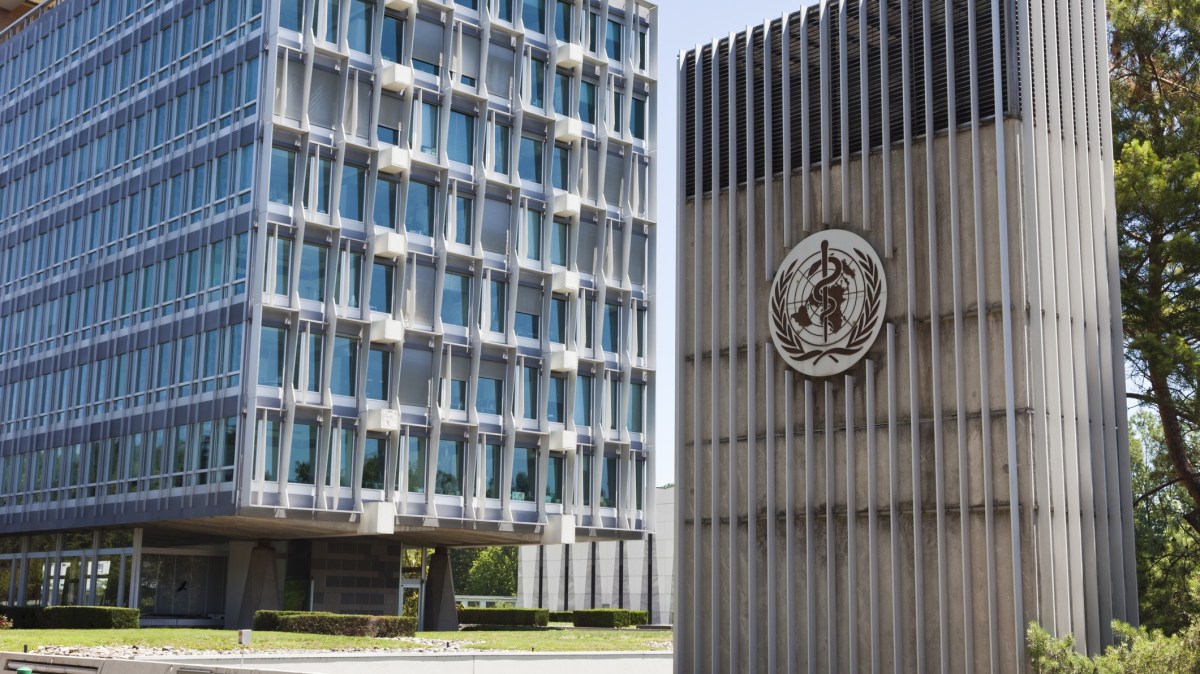
Hack-for-hire firms in India have been impersonating the World Health Organization in credential-stealing spearphishing email campaigns, Google’s Threat Analysis Group said Wednesday.
The hack-for-hire campaign, which has targeted healthcare companies, consulting firms, and financial services entities primarily in the U.S., Slovenia, Canada, Iran, Bahrain, and Cyprus, uses Gmail accounts imitating the WHO to direct victims to lookalike WHO websites. From there, victims are urged to sign up for healthcare alerts related to the coronavirus pandemic, according to Google. When signing up, however, users are prompted to reveal their Google account credentials or other personal information such as their cell phone numbers.
It’s just the latest example of criminals and nation-state actors seizing upon the uncertainty during the COVID-19 pandemic to send spam emails purporting to have information from health authorities about the coronavirus, but are actually seeking to steal credentials or are laced with malware. Other spearphishing email campaigns have imitated the U.S. Centers for Disease Control and Prevention and other local health authorities, for example.
But even as many municipalities ease shelter-in-place orders, Google has not seen this kind of spam activity slow down, the company said in a blog post.
“[W]e’re seeing a resurgence in COVID-related hacking and phishing attempts from numerous commercial and government-backed attackers,” read a post authored by Shane Huntley, Google’s Threat Analysis Group’s director of software engineering. “Generally, 2020 has been dominated by COVID-19.”
It’s unclear if the Indian hack-for-hire firms Google was tracking were linked directly with any government hacking directives. Nation-state hackers have in the past outsourced their hacking operations in an effort to make tracing their activity more difficult, according to the FBI.
YouTube disinformation
Nation-state linked influence operations have likewise not stopped during the pandemic, according to Google. Since March of this year, Google has taken down approximately a thousand YouTube channels that were behaving in a coordinated and spammy manner, for instance.
Many of these takedowns did not appear to be political in nature, although some of the Chinese-language channels were primarily focused on political content, Huntley said.
Google has also terminated advertising accounts, AdSense accounts, 1 Play developer account, and YouTube channels related to coordinated influence operations emanating from Iran, Egypt, India, and Indonesia.
Moving forward, Google will be issuing quarterly reports about takedowns.
“We’ve … shared occasional updates about this kind of activity, and today we’re introducing a more streamlined way of doing this via a new, quarterly bulletin to share information about actions we take against accounts that we attribute to coordinated influence campaigns (foreign and domestic),” Huntley said.
The move comes amid heightened scrutiny in recent days of how technology companies impact the flow of information online, but it’s also part of a longstanding effort among tech titans to be more transparent about what is allowed on their platforms. The decision comes approximately two months after Facebook’s announcement it plans to periodically publish details on its takedowns of inauthentic behavior in one place.
More Scoops
Supreme Court poised to rewrite how social media confronts disinformation
If the Supreme Court backs state efforts to limit platforms from curating content, online disinformation will surge, experts and tech companies say.
Chinese state media propaganda found in 88% of Google, Bing news searches
Facebook, Twitter, Google move to intercept Russian propaganda, disinformation about Ukraine
Latest Podcasts
Government
FBI officials say AI is bolstering adversaries, emphasizing need to focus on cyber basics, patching
Feds accuse China of ‘systematic’ distillation of U.S. AI models
CIA’s Michael Ellis says cyber intelligence is changing how the agency operates
The G7 tells industry to hurry up and prep for post-quantum encryption
Technology
Threats
Chinese espionage groups swarm to exploit triple-link chain of zero-days
Microsoft discloses two actively exploited zero-days among 974 vulnerabilities
Russian national extradited to US for alleged involvement in bank-account takeover scheme
Attackers exploit zero-days in consistently besieged SonicWall product
Policy
Whistleblower says USPS deploying new, ‘untested’ IT systems governing mail-in ballots
‘Watershed 250’ test program in Texas looks to private sector for water cybersecurity help
Former sexual abuse victims say Grok used their images, videos to train deepfake capabilities
Cyber threats nudge Trump to sign executive order on foreign equipment in U.S. energy infrastructure
Text extracted automatically; images, tables and formatting may be missing. Original: https://cyberscoop.com/coronavirus-phishing-scheme-google-india-world-health-organization/