When security gets hot
Full article450 words · extracted from securelist.com · click to collapse


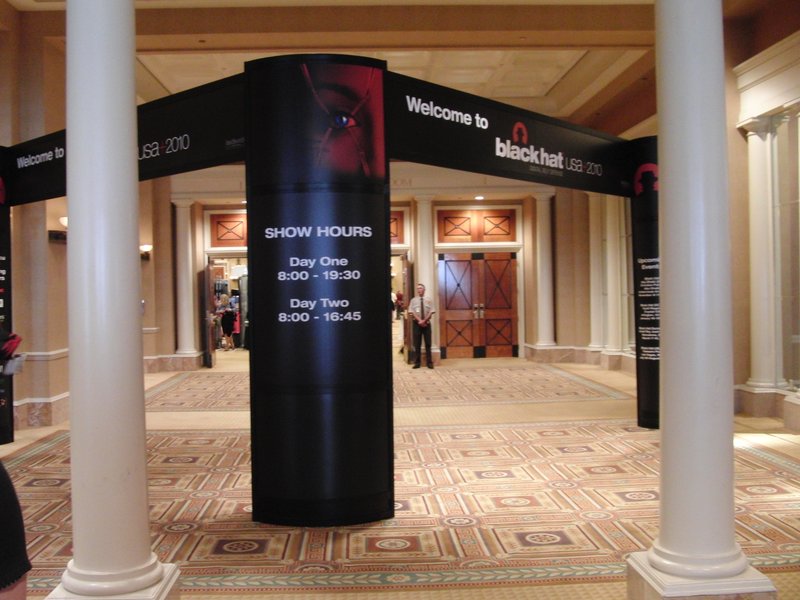
There are people who think that all hackers should be sent to the desert – well, once a year this dream comes true.
Greetings from Las Vegas where two major security conferences just ended.
As every year Black Hat took place here at the Caesars Palace. People from around the globe gave presentations about ATM-hacking, reverse-engineering and other security related topics distributed over 11 tracks in two days. The host casino offers for this event lots of space, so you walk long until you get in the target room where you want to attend the presentation.
At the vendor area you may always find interesting people to talk to or get information about security products and services. This year a big group of Kaspersky people attended Black Hat 2010 (from the US, Japan, Romania, France and Germany).
What would you think if hundreds of hackers, nerds and geeks go to the desert and flood the Riviera in Las Vegas? – Yes, it’s time for DefCon!
One of the well known hacker conferences world-wide.
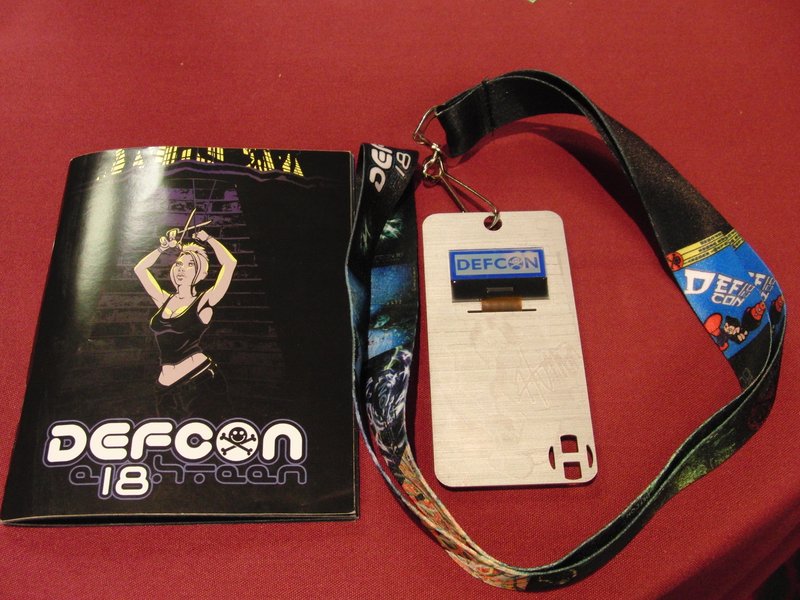
It’s the 18th DefCon these days, offering talks, hardware hacking, lots of contests, meetings, games, movies, parties and a hair-dresser for the perfect geek haircut “mohawk”.
This event always reminds me of the CCC (chaos communication congress) in Germany. And therefore the talks are mostly overcrowded and the Internet connection is not as stable as it should be – but hey, it’s a hacker event.
The talks targeting lots of different topics as attacks, hardware hacking, Internet related topics, reverse engineering and security. If you want you can also do hands-on at different contests and mess with others. Nearly everything invites to play around with, even the badge for this conference is open hardware and can be modified in many ways. And if you need a rest, there is space in the chill-out-area or the contest-area where you can meet people and discuss everything around computers and more. At the vendor area you may also find some stuff to buy for fun, work or to dress.
Latest Webinars
Reports
Kaspersky researchers have discovered new Mirage Kitten attacks using previously undocumented malware families: NodeRabbit in Node.js and PollCat in JavaScript.
Our experts discovered a new CoolClient backdoor variant with a kernel-mode rootkit driver that hides malicious processes, files, and network connections from security tools and threat analysts.
Kaspersky experts break down a new Armored Likho campaign that poses as a fundraising efforts and delivers a new Still Toolkit aimed at stealing Telegram data and eavesdropping on victims.
Kaspersky researchers reveal previously undocumented malware attributed to Mirage Kitten (UNC1549, Smoke Sandstorm, Nimbus Manticore): NightLedger backdoor, ArcBridge, and BridgeHead tunneling tools.
Text extracted automatically; images, tables and formatting may be missing. Original: https://securelist.com/when-security-gets-hot/29729/