Spammers change their tune
Full article320 words · extracted from securelist.com · click to collapse



Spammers have brought another instrument into their orchestra of tricks – MP3 audio files. This new type of spam is circulating in European mail traffic: a blank message, a classic social engineering message header, and an attached MP3 file. There’s been speculation that this might happen for a while, and although this new development is interesting, we don’t think that MP3 spam is going to have much of a future.
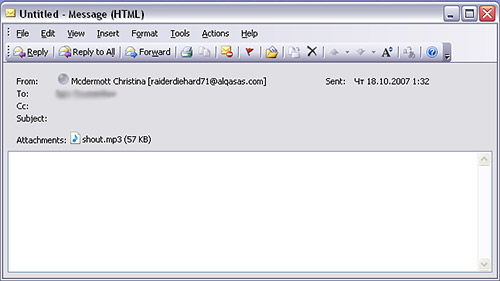
The actual audio file contains a ‘stock spam’ message designed to inflate the price of shares in a certain company. But the spammers have had to make a trade off between making the message as small as possible, and making a comprehensible recording. They’ve misjudged – the quality of the sound file isn’t easy to listen to. Even if a user does bother to listen to the almost 30 seconds of advertising, it’s unlikely that they’ll be persuaded to buy, as listening to a recording, noting the details and then going online is a far longer process than simply clicking on a link in an email.
However, this latest mass mailing demonstrates once again that spammers are still trying new tricks in their continued quest to slip advertising past spam filters and trick unwary users.
Latest Webinars
Reports
Kaspersky researchers have discovered new Mirage Kitten attacks using previously undocumented malware families: NodeRabbit in Node.js and PollCat in JavaScript.
Our experts discovered a new CoolClient backdoor variant with a kernel-mode rootkit driver that hides malicious processes, files, and network connections from security tools and threat analysts.
Kaspersky experts break down a new Armored Likho campaign that poses as a fundraising efforts and delivers a new Still Toolkit aimed at stealing Telegram data and eavesdropping on victims.
Kaspersky researchers reveal previously undocumented malware attributed to Mirage Kitten (UNC1549, Smoke Sandstorm, Nimbus Manticore): NightLedger backdoor, ArcBridge, and BridgeHead tunneling tools.
Text extracted automatically; images, tables and formatting may be missing. Original: https://securelist.com/spammers-change-their-tune/30375/