CISA directive orders federal civilian agencies to regularly report software vulnerabilities
Full article534 words · extracted from cyberscoop.com · click to collapse
Get our latest cybersecurity news first on Google.
CISA Director Jen Easterly said the directive will give the agency more insight into federal civilian agencies' cybersecurity practices.
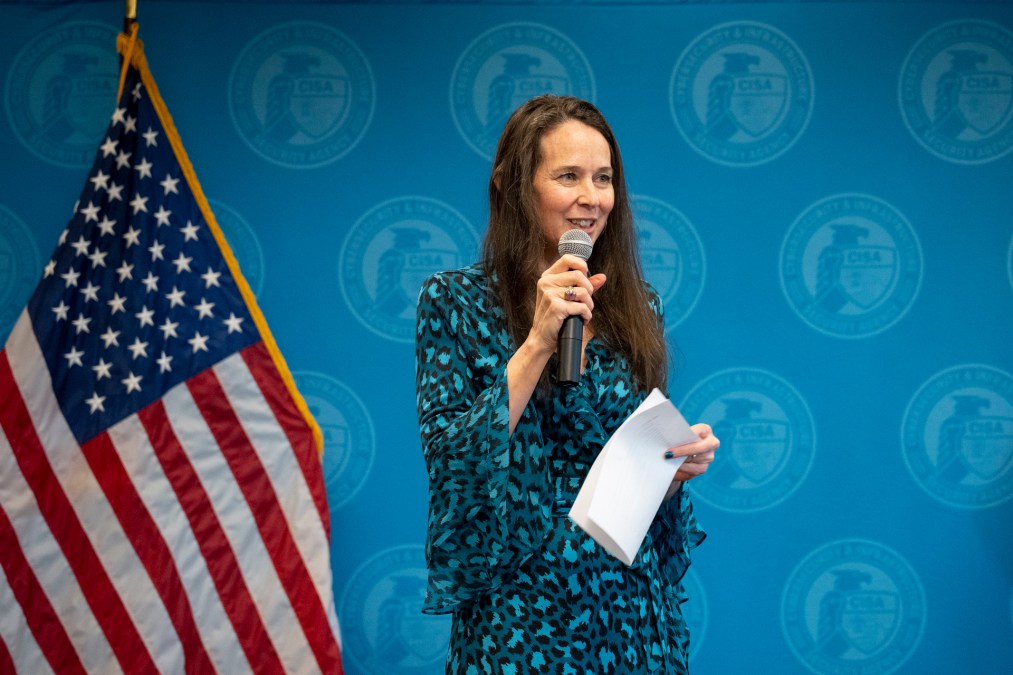
The Cybersecurity and Infrastructure Security Agency announced a Binding Operational Directive on Monday ordering federal civilian agencies to enhance efforts to detect vulnerabilities in their networks, a move that CISA Director Jen Easterly hopes the private sector will emulate.
The Improving Asset Visibility and Vulnerability Detection on Federal Networks, or BOD 23-01, directive is designed to improve “asset visibility and vulnerability detection on federal networks,” Easterly told reporters during a CISA roundtable discussion on Monday. Federal civilian agencies now will be expected to report detailed data about vulnerabilities to CISA at timed intervals using automated tools, she said.
“We have said consistently that we are on an urgent path to gain visibility into risks facing federal civilian networks,” Easterly told reporters. “This is a movement essentially to allow CISA, in its role as operational lead for federal cybersecurity, to manage federal cybersecurity as an enterprise.”
The development of the directive “really reflects [CISA’s] rapidly maturing role” of helping agencies improve network visibility, she said, pointing to the Solar Winds supply chain compromise as a prime example of the “gap” in agencies’ awareness of their own threat surface.
By establishing baseline requirements for agencies to use in identifying assets and vulnerabilities, Easterly said the directive gives CISA a much more granular view of federal agencies’ disparate cybersecurity postures.
“Threat actors continue to target our nation’s critical infrastructure and government networks to exploit weaknesses within unknown, unprotected, or under-protected assets,” Easterly said in a press release. “While this directive applies to federal civilian agencies, we urge all organizations to adopt the guidance in this directive to gain a complete understanding of vulnerabilities that may exist on their networks.”
Latest Podcasts
Government
FBI officials say AI is bolstering adversaries, emphasizing need to focus on cyber basics, patching
Feds accuse China of ‘systematic’ distillation of U.S. AI models
CIA’s Michael Ellis says cyber intelligence is changing how the agency operates
The G7 tells industry to hurry up and prep for post-quantum encryption
Technology
Threats
Chinese espionage groups swarm to exploit triple-link chain of zero-days
Microsoft discloses two actively exploited zero-days among 974 vulnerabilities
Russian national extradited to US for alleged involvement in bank-account takeover scheme
Attackers exploit zero-days in consistently besieged SonicWall product
Policy
Whistleblower says USPS deploying new, ‘untested’ IT systems governing mail-in ballots
‘Watershed 250’ test program in Texas looks to private sector for water cybersecurity help
Former sexual abuse victims say Grok used their images, videos to train deepfake capabilities
Cyber threats nudge Trump to sign executive order on foreign equipment in U.S. energy infrastructure
Text extracted automatically; images, tables and formatting may be missing. Original: https://cyberscoop.com/cisa-mandate-federal-agencies-cybersecurity/