DOJ examines controversial new 'hack back' bill
Full article625 words · extracted from cyberscoop.com · click to collapse
Get our latest cybersecurity news first on Google.
The years-long "hack back" discussion is finally being debated in Congress. A DOJ official weighed in during CyberTalks.
Washington is waiting and watching for the Department of Justice to weigh in on the newly introduced Active Cyber Defence Certainty (ACDC) Act, a controversial proposal to legalize companies’ ability to “hack back” after being targeted in cyberattacks.
Speaking at CyberTalks in Washington, D.C., on Wednesday, DOJ special counsel Leonard Bailey said the department is still looking at the House bill, and he commended co-sponsors Tom Graves, R-Ga. and Kyrsten Sinema, D-Ariz. for taking a years-long discussion “and actually producing legislative text.”
“We look forward to thinking about that and figuring out what that balance looks like,” Bailey said.
The DOJ’s position on ACDC is crucial because the bill would amend the Computer Fraud and Abuse Act (CFAA) as well as requiring law enforcement oversight and reports to the government by “entities that use active-defense techniques,” Graves explained last week when the newest version of the bill was introduced.
NSA Director Adm. Mike Rogers warned Congress in May against hack-back legislation because such a law could effectively open a Pandora’s Box by producing confusion and dangerous side-effects.
“My concern is, be leery of putting more gunfighters out in the street in the Wild West,” Rogers said in May when he testified before a House Armed Services subcommittee. “As an individual tasked with protecting our networks, I’m thinking to myself — we’ve got enough cyber actors out there already.”
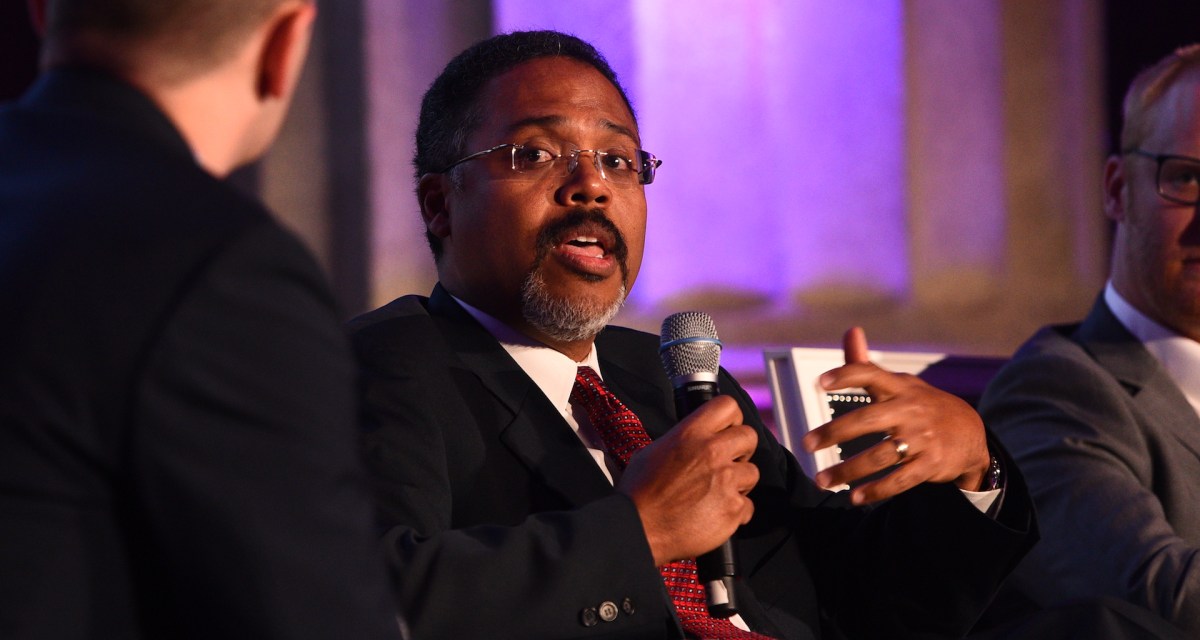
Bailey spoke Wednesday on a panel next to Bugcrowd founder Casey Ellis and HackerOne CEO Marten Mickos about the CFAA, how the law impacts vulnerability disclosure and bug bounty programs, and how potential reform through ACDC might play out. The bill would be unprecedented around the world, and even proponents agree that there are wide unanswered questions about such a law’s possible consequences.
“Hacking back has its justified role in certain situations,” HackerOne’s Mickos said. “But the real threat is asymmetric. That means that often there is nothing to hack back at. There are very few cases where the threat is symmetric. [ACDC] won’t have a dramatic effect on industry. Instead, the real solution is in pooling defense, sharing vulnerability across every company. That’s a much more powerful solution than hacking back.”
It was still early in the morning, but Mickos’ remarks were met with the most energetic applause of the day from the CyberTalks crowd.
Latest Podcasts
Government
FBI officials say AI is bolstering adversaries, emphasizing need to focus on cyber basics, patching
Feds accuse China of ‘systematic’ distillation of U.S. AI models
CIA’s Michael Ellis says cyber intelligence is changing how the agency operates
The G7 tells industry to hurry up and prep for post-quantum encryption
Technology
Threats
Microsoft discloses two actively exploited zero-days among 974 vulnerabilities
Russian national extradited to US for alleged involvement in bank-account takeover scheme
Attackers exploit zero-days in consistently besieged SonicWall product
Jail time for Maine child in 764 marks turning point in federal law enforcement
Policy
Whistleblower says USPS deploying new, ‘untested’ IT systems governing mail-in ballots
‘Watershed 250’ test program in Texas looks to private sector for water cybersecurity help
Former sexual abuse victims say Grok used their images, videos to train deepfake capabilities
Cyber threats nudge Trump to sign executive order on foreign equipment in U.S. energy infrastructure
Text extracted automatically; images, tables and formatting may be missing. Original: https://cyberscoop.com/doj-examines-controversial-new-hack-back-bill/