Pentagon goes 'back to basics' on cyber
Full article853 words · extracted from cyberscoop.com · click to collapse
Get our latest cybersecurity news first on Google.
Every Friday the CIOs of the military services and major pentagon agencies convene with Terry Halvorsen, the Defense Department CIO, to go over the latest data from the department's cybersecurity scorecard — and it can be an uncomfortable experience.
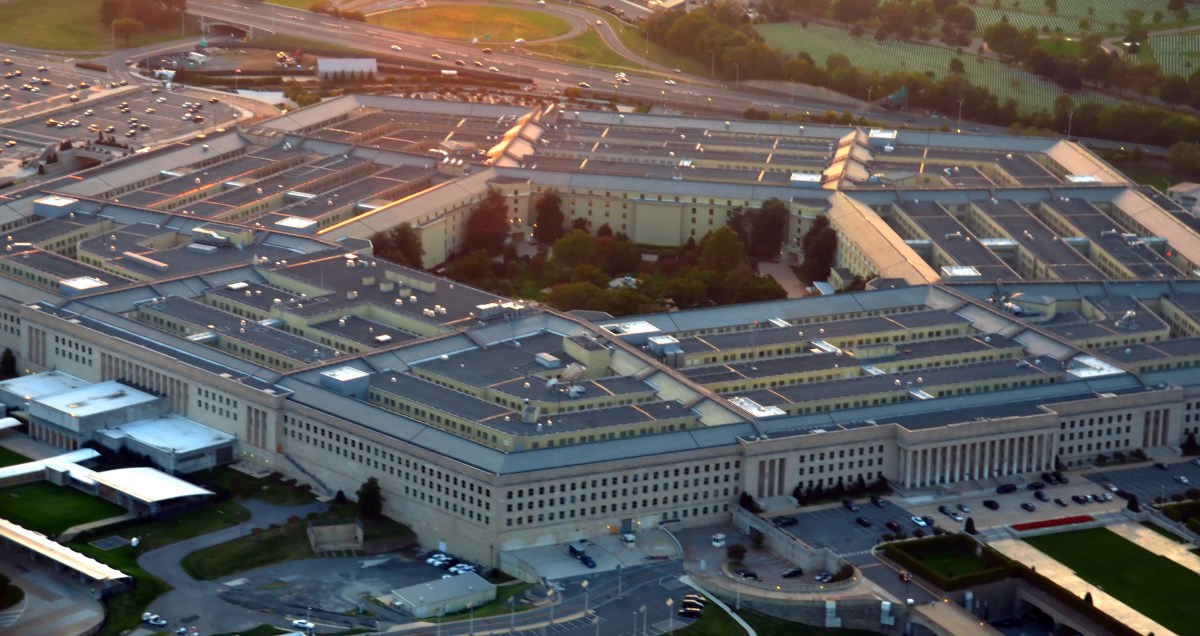
It’s back to basics once a week for the CIOs of the military services and major agencies in the Pentagon.
Every Friday they convene with Defense Department CIO Terry Halvorsen to go over the latest data from the department’s cybersecurity scorecard — and it can be an uncomfortable experience, according to Marianne Bailey, the principal director in the office of the deputy Defense CIO for cybersecurity.
“No one wants to be an outlier, no one wants a bad grade,” she told the FedScoop Federal Cybersecurity Summit, sponsored by Hewlett-Packard Enterprise, last week.
“He’s very assertive, proactive,” she said of Halvorsen in an interview after her presentation, “He doesn’t accept reasons why, [he says] ‘Just tell me how you’re going to fix it.'”
The mood in the meetings is positive, she said. “There was a lot of pushback early on, which was interesting to watch.”
Every month, data from the scorecard, which measures progress on 10 key cybersecurity targets, is sent to Secretary of Defense Ashton Carter — and every quarter, he and Halvorsen meet to review their goals.
“There is accountability from the very very top, all the way down,” said Bailey, calling the regular meetings “kind of unprecedented.”
The scorecard measures progress on targets set in the DOD’s back-to-basics cyber plan — the Cybersecurity Discipline Implementation Plan. The plan, released last year and updated in February, is designed to radically simplify the approach of the huge department and provide metrics and benchmarks for assessing progress, she said.
“We were getting a lot of complaints [from our cybersecurity workforce] that they were very inundated with all the things they were being barraged with to do,” she said. “We had no way of measuring how we were doing.”
The plan was drawn up after an intrusion assessment had identified a few key measures that — if implemented throughout the department — would significantly improve cybersecurity.
The measures include requiring a PKI key for every login; having separate logins for system administrators used only when special admin privileges are required; and ensuring the department’s Host-Based Security System is installed on every endpoint.
The eventual aim, Bailey explained, is to bring about a culture change so proper cybersecurity becomes as important as the proper use and storage of firearms.
“I think we will get there,” She said, “I don’t think we’re there yet. You get trained on that firearm a ton of times. Training, refresher training, you have to stay qualified… We’re trying to get there on cybersecurity.”
Currently, all federal employees take annual training on IT security — or information assurance, as it’s more formally known. “A class once a year is just not good enough to refresh you,” said Bailey — something else her office is seeking to change, by introducing a cybersecurity “pop quiz” as part of the logon process.
“Every single day before I log on, I have to answer three questions,” she explained, about “things that every user needs to know.”
“I can miss one and it will give me the answer, but if I keep missing them, guess what? I have to take remedial training,” she said, adding that the measure had been rolled out in a few offices but was “not implemented department-wide yet.”
She said all these initiatives are examples of Halvorsen’s leadership.
“People talk about authorities, but sometimes I don’t know that you really need clear, written in legislation authorities. If you have a really good vision and a really good plan, you’re in the right position and you’re well respected — you can push it out and just stay on top of it … I think that’s what Halvorsen’s done.”
Latest Podcasts
Government
Technology
European parliament members call for slowdown of Serbia’s EU entry over spyware use
Pegasus, NoviSpy variant spyware found on devices of Serbian activists
Wyden seeks upgraded NSA security guidance on commercial VPN use
Former sexual abuse victims say Grok used their images, videos to train deepfake capabilities
Threats
Chinese espionage groups swarm to exploit triple-link chain of zero-days
Microsoft discloses two actively exploited zero-days among 974 vulnerabilities
Russian national extradited to US for alleged involvement in bank-account takeover scheme
Attackers exploit zero-days in consistently besieged SonicWall product
Policy
Whistleblower says USPS deploying new, ‘untested’ IT systems governing mail-in ballots
‘Watershed 250’ test program in Texas looks to private sector for water cybersecurity help
Cyber threats nudge Trump to sign executive order on foreign equipment in U.S. energy infrastructure
Election official says Tina Peters would be consultant, won’t have access to election systems
Text extracted automatically; images, tables and formatting may be missing. Original: https://cyberscoop.com/pentagon-goes-back-basics-cyber/