Senate Intel chair urges national cyber director to safeguard against open
Full article731 words · extracted from cyberscoop.com · click to collapse
Get our latest cybersecurity news first on Google.
Tom Cotton, R-Okla., cited Chinese and Russian involvement in open-source tech and the risks to government and defense systems.
Listen to this article
0:00
Learn more.
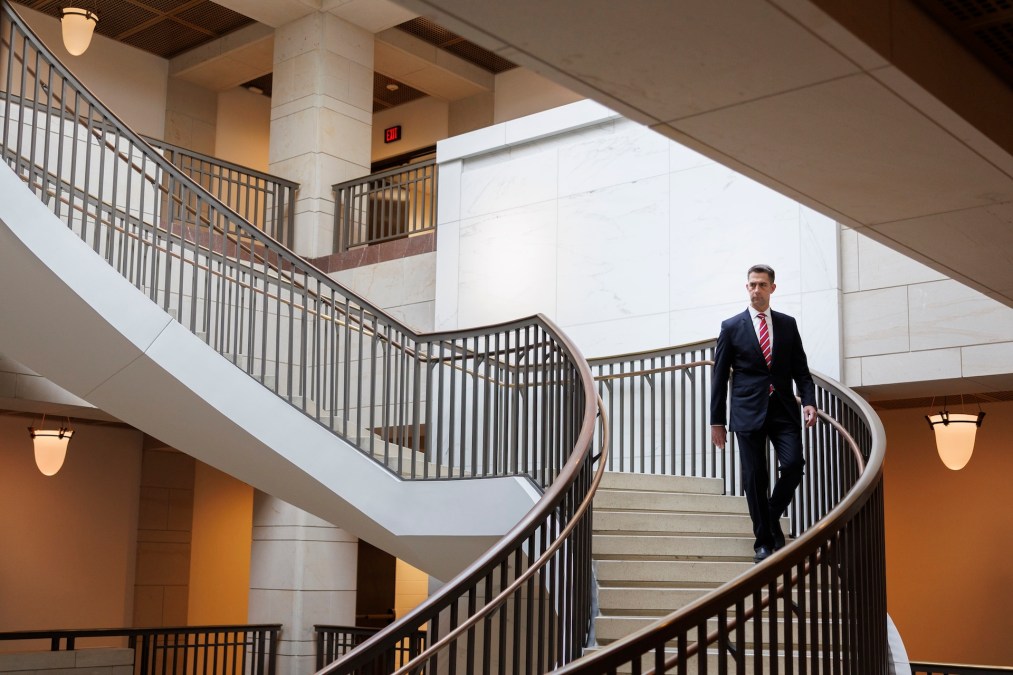
Senate Intelligence Committee Chairman Tom Cotton is raising the spectre of foreign adversaries playing too heavy a role in open-source software, and asking the national cyber director to counter the risks.
The Arkansas Republican wrote to National Cyber Director Sean Cairncross Thursday, saying he was concerned about reports that “state-sponsored software developers and cyber espionage groups have started to exploit this communal environment, which assumes that contributors are benevolent, to insert malicious code into widely used open source codebases.”
Cotton cited last year’s alarms about a shadowy suspected nation-state hacker, Jia Tan, inserting a backdoor into a beta version of the compression utility XZ Utils. He also noted a Russia-based developer being the sole maintainer of a piece of open-source software (OSS) that’s in Defense Department software packages, and citations about Chinese tech companies Alibaba and Huawei being top OSS contributors.
“As the Office of the National Cyber Director holds responsibility for coordinating implementation of national cyber policy and government-wide cybersecurity, you are well-positioned to lead the U.S. government in addressing this cross-cutting vulnerability,” Cotton wrote. “I respectfully request that you take steps to build up the federal government’s capability to maintain awareness of provenance and foreign influence on OSS and track contributions from developers in adversary nations.”
Cotton’s letter adds to warnings from the Hill this year about the risks that Chinese involvement in open-source tech poses, following a letter from the House select committee on China on the subject to Biden-era Commerce Secretary Gina Raimondo. Legislation designed to improve open-source cybersecurity didn’t advance in the Senate after leading lawmakers introduced it in 2023.
The senator noted that open-source software is part of critical government and defense systems. Defense Secretary Pete Hegseth in July ordered the Pentagon’s chief information officer to take steps to guard against foreign influence in department technology.
“The DoD will not procure any hardware or software susceptible to adversarial foreign influence that presents risk to mission accomplishment and must prevent such adversaries from introducing malicious capabilities into the products and services that are utilized by the Department,” he wrote.
At the same time, a Trump administration executive order this year puzzled experts by deleting language from a previous Biden administration executive order emphasizing the importance of open-source software.
More Scoops
Open-source security is posing challenges governments can’t easily solve
A diffuse landscape, fruitful targets, companies not stepping up, AI’s influence and flagging U.S. government efforts all figure into a shifting threat.
New National Cyber Director Cairncross faces challenges on policy, bureaucracy, threats
Unverified code is the next national security threat
Latest Podcasts
Government
FBI officials say AI is bolstering adversaries, emphasizing need to focus on cyber basics, patching
Feds accuse China of ‘systematic’ distillation of U.S. AI models
CIA’s Michael Ellis says cyber intelligence is changing how the agency operates
Jail time for Maine child in 764 marks turning point in federal law enforcement
Technology
Threats
Policy
Whistleblower says USPS deploying new, ‘untested’ IT systems governing mail-in ballots
‘Watershed 250’ test program in Texas looks to private sector for water cybersecurity help
Former sexual abuse victims say Grok used their images, videos to train deepfake capabilities
Cyber threats nudge Trump to sign executive order on foreign equipment in U.S. energy infrastructure
Text extracted automatically; images, tables and formatting may be missing. Original: https://cyberscoop.com/tom-cotton-open-source-software-foreign-influence-national-cyber-director/