The one that didn’t get away
Full article260 words · extracted from securelist.com · click to collapse



This week the Anti-Virus Testing Workshop is taking place in Reykjavik. When I arrived in Iceland one of the first things I did was to turn on my mobile phone. Up until now, I’ve never had any strange Bluetooth connection requests at an airport, but while waiting for my luggage this changed.
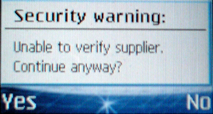 Of course, I accepted the file and was greeted with a pop up from KAV Mobile saying that the file contained Worm.SymbOS.Comwar.c. Although this happened in Iceland I suspect the worm may have come from someone who was on the same plane as me. However, I can’t be sure, and there’s no way of proving this.
I shared news of the worm with some other AV guys who are here. And that’s exactly what it was to them, news. Just goes to show that mobile malware is still something of a novelty even in AV researcher circles.
Latest Webinars
Reports
Kaspersky researchers have discovered new Mirage Kitten attacks using previously undocumented malware families: NodeRabbit in Node.js and PollCat in JavaScript.
Our experts discovered a new CoolClient backdoor variant with a kernel-mode rootkit driver that hides malicious processes, files, and network connections from security tools and threat analysts.
Kaspersky experts break down a new Armored Likho campaign that poses as a fundraising efforts and delivers a new Still Toolkit aimed at stealing Telegram data and eavesdropping on victims.
Kaspersky researchers reveal previously undocumented malware attributed to Mirage Kitten (UNC1549, Smoke Sandstorm, Nimbus Manticore): NightLedger backdoor, ArcBridge, and BridgeHead tunneling tools.
Text extracted automatically; images, tables and formatting may be missing. Original: https://securelist.com/the-one-that-didnt-get-away/30329/