Watchdog: Agency overseeing cybersecurity for offshore energy falling short
Full article834 words · extracted from cyberscoop.com · click to collapse
Get our latest cybersecurity news first on Google.
The Government Accountability Office said that a worst-case scenario for an offshore oil and gas facility could lead to fatalities.
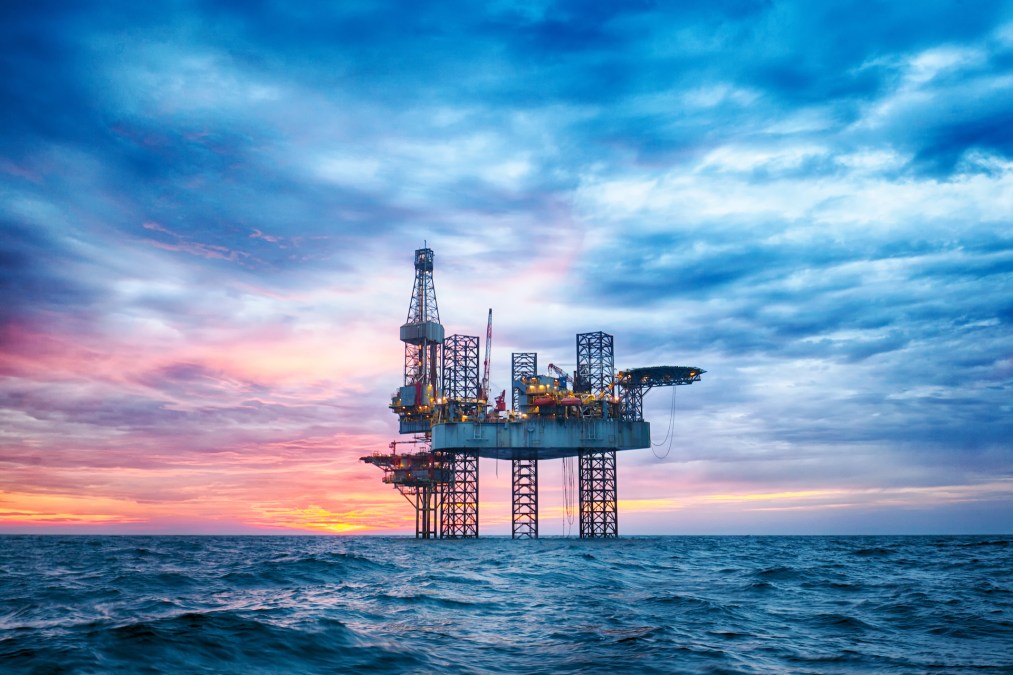
The federal enforcement office that oversees more than 1,600 offshore oil and gas facilities has done little to address growing cybersecurity risks, according to a watchdog report released on Thursday.
The Government Accountability Office said that the Department of Interior’s Bureau of Safety and Environmental Enforcement has taken “few actions” to address cybersecurity risks since the agency first planned to address the issue in 2015, noting that an attack on an offshore oil and gas rig could be catastrophic.
“We’re not dealing with just a system going down or a website or data leakage or maybe some financial loss, there could be major consequences for an offshore oil rig not operating as intended,” said Chris Grove, director of cybersecurity strategy at Nozomi Networks, a firm that works with offshore oil and gas rigs.
When a facility is miles from land in the middle of an ocean any type of assistance can be difficult during an incident, said Grove, pointing to the 2010 BP Deepwater Horizon oil pipeline collapse as an example of a worst-case scenario.
The GAO also noted that a worst-case scenario can be potentially fatal. “According to BSEE incident investigation documentation, these can include deaths and injuries, damaged or destroyed equipment, and pollution to the marine environment. However, in a worst-case OT failure scenario, all these impacts can occur simultaneously at a catastrophic scale.”
BSEE planned to address the cybersecurity risks in 2015 and again in October 2020, but both times “no resulting actions were taken to address cybersecurity issues,” GAO wrote.
According to the GAO, BSEE proposed developing a “foundational cybersecurity capability” to work with industry in the fiscal year 2023 budget justification. In May, BSEE hired a cybersecurity specialist to work on the issue, however, the agency told the GAO that the program’s development is on hold until that individual “is adequately versed in the relevant issues and entities.”
The GAO noted that the operational technology used to manage those systems can often run on legacy systems that are increasingly connected to the internet, increasing the potential for attacks.
The watchdog recommended that “BSEE should immediately develop and implement a strategy to address offshore infrastructure risks.”
The GAO wrote that BSEE “generally concurred” with the report and recommendation. When reached for comment, BSEE said that “we do not have any additional comments beyond what is printed in the GAO report.”
Events such as the Colonial Pipeline ransomware attack highlight how attacks on business IT systems can have ramifications on industrial operations. In that case, industrial operators shut down due to an abundance of caution. Nozomi’s Grove pointed out, however, that it’s those “unintended consequences” from cyberattacks that are concerning.
“You can go out there with a truck” to fix or replace any equipment, but with offshore oil rigs it’s not as simple when the facility is miles away, Grove said. “Having a network admin just swing by and apply the patch isn’t as easy as you want.”
The GAO pointed out the threat landscape for offshore oil and gas is difficult to determine as there is no reporting mandate for that industry: “Specifically, no federal officials or industry representatives we contacted were aware of any cyberattacks against offshore oil and gas infrastructure or specific requirements to report them if they occur.”
Grove said that it could be time to reconsider whether BSEE should be charged with overseeing cybersecurity for offshore oil and gas. “It’s not their core competency and this is an extremely difficult and challenging cybersecurity problems to solve — one of the biggest out there,” he said. “Anyone that’s trying to solve that is going to be facing an uphill battle.”
Latest Podcasts
Government
FBI officials say AI is bolstering adversaries, emphasizing need to focus on cyber basics, patching
Feds accuse China of ‘systematic’ distillation of U.S. AI models
CIA’s Michael Ellis says cyber intelligence is changing how the agency operates
The G7 tells industry to hurry up and prep for post-quantum encryption
Technology
Threats
Chinese espionage groups swarm to exploit triple-link chain of zero-days
Microsoft discloses two actively exploited zero-days among 974 vulnerabilities
Russian national extradited to US for alleged involvement in bank-account takeover scheme
Attackers exploit zero-days in consistently besieged SonicWall product
Policy
Whistleblower says USPS deploying new, ‘untested’ IT systems governing mail-in ballots
‘Watershed 250’ test program in Texas looks to private sector for water cybersecurity help
Former sexual abuse victims say Grok used their images, videos to train deepfake capabilities
Cyber threats nudge Trump to sign executive order on foreign equipment in U.S. energy infrastructure
Text extracted automatically; images, tables and formatting may be missing. Original: https://cyberscoop.com/bsee-offshore-cybersecurity-gao/