CISA to formally solicit industry feedback on cybersecurity incident reporting rules
Full article872 words · extracted from cyberscoop.com · click to collapse
Get our latest cybersecurity news first on Google.
CISA Director Jen Easterly will meet with executives to craft a framework for cybersecurity incident reporting that doesn't "burden industry."
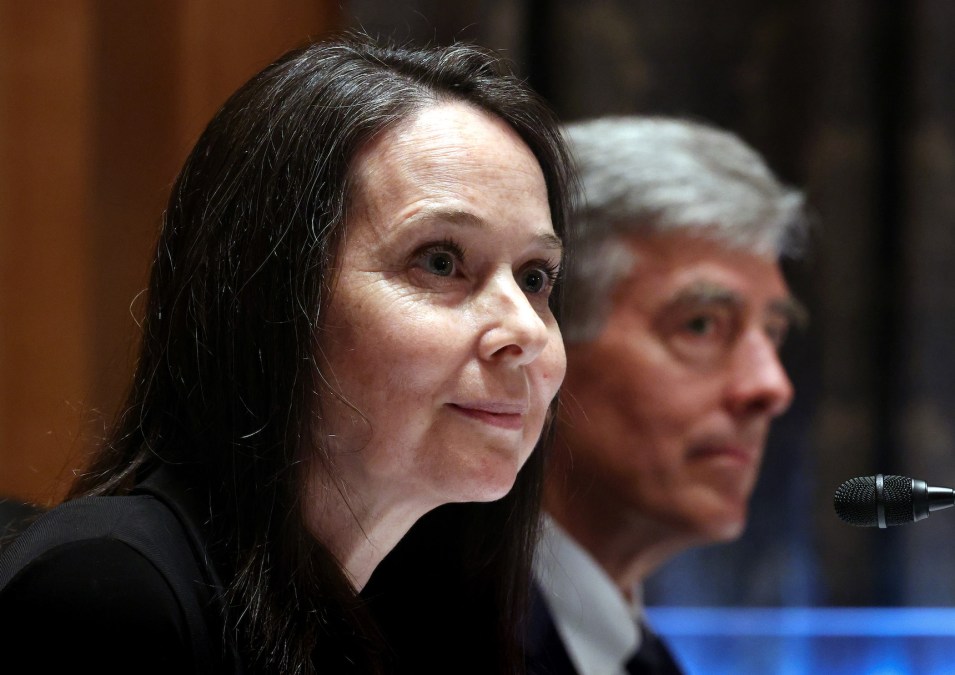
Federal cyber officials will formally ask industry leaders “in the next couple of days” to help shape the regulatory structure for cybersecurity incident reporting, Jen Easterly, director of the Department of Homeland Security’s Cybersecurity and Infrastructure Security Agency, said Wednesday.
The incident reporting framework follows the new law that President Biden signed in March requiring that critical infrastructure owners and operators to report major cyberattacks to CISA within 72 hours and ransomware attacks within 24 hours.
CISA has said that it will use the reports to rapidly deploy resources to victims under attack and share information with network defenders. Easterly, who spent four years working on cyber defense at Morgan Stanley prior to coming to CISA, emphasized that she wants to work with industry to create a smart regulatory apparatus that doesn’t create problems for the private sector.
“This will finally allow us a much better understanding what’s going on across the ecosystem,” Easterly said at the Billington Cybersecurity Summit in Washington. “We don’t want to burden industry and we don’t want to burden the federal government with noise either.”
Easterly said that after CISA issues a request for information from the private sector, she intends to also host several listening sessions with industry to ensure the rule-making process is “consultative.”
Throughout the interview at Billington, Easterly emphasized that while offensive cybersecurity is “sexy,” she wants cyber defenders to understand that “defense is the new offense.”
“We don’t want to burden industry and we don’t want to burden the federal government with noise either.”
jen easterly, cisa
“There’s amazing, amazing talent out there in the defense community, and we need to harness that to make sure that we are building and defending a secure and resilient ecosystem to make adversaries’ jobs much harder,” Easterly said. “This is the thing — attackers have budgets, too. We have to work together to make sure that we are increasing the marginal cost of their investment.”
U.S. cybersecurity practitioners can compete with anyone on the basis of skills alone, Easterly said. But she cautioned that America may sometimes come in behind adversaries because of ethics.
“They go after schools, they go after hospitals, they go after emergency services, they go after water,” Easterly said, lamenting what she called an “asymmetry in morality” between U.S. cyber operators and enemies.
Easterly was followed to the stage at Billington by National Cyber Director Chris Inglis, who told the audience that the “sense of urgency continues to go up on a daily basis.”
“Defense needs to be the new offense: We need to establish the initiative. That’s job one, priority one,” he said. “We need to make it such that if you’re a transgressor in this space, the new deal is you got to beat all of us to beat one of us.”
More Scoops
The push to designate AI as the next critical infrastructure sector
The designation would unlock a range of federal services, tools and resources for an industry that policymakers view as increasingly tied to national and economic security.
Trump blames Minnesota for cyberattacks on water sector, drawing pushback from cyber world
Industry’s message on CIRCIA: Please ask us fewer questions about cyberattacks
Latest Podcasts
Government
FBI officials say AI is bolstering adversaries, emphasizing need to focus on cyber basics, patching
Feds accuse China of ‘systematic’ distillation of U.S. AI models
CIA’s Michael Ellis says cyber intelligence is changing how the agency operates
The G7 tells industry to hurry up and prep for post-quantum encryption
Technology
Threats
Chinese espionage groups swarm to exploit triple-link chain of zero-days
Microsoft discloses two actively exploited zero-days among 974 vulnerabilities
Russian national extradited to US for alleged involvement in bank-account takeover scheme
Attackers exploit zero-days in consistently besieged SonicWall product
Policy
Whistleblower says USPS deploying new, ‘untested’ IT systems governing mail-in ballots
‘Watershed 250’ test program in Texas looks to private sector for water cybersecurity help
Former sexual abuse victims say Grok used their images, videos to train deepfake capabilities
Cyber threats nudge Trump to sign executive order on foreign equipment in U.S. energy infrastructure
Text extracted automatically; images, tables and formatting may be missing. Original: https://cyberscoop.com/cisa-cybersecurity-incident-reporting/