We Come in Peace, Too
Full article239 words · extracted from securelist.com · click to collapse
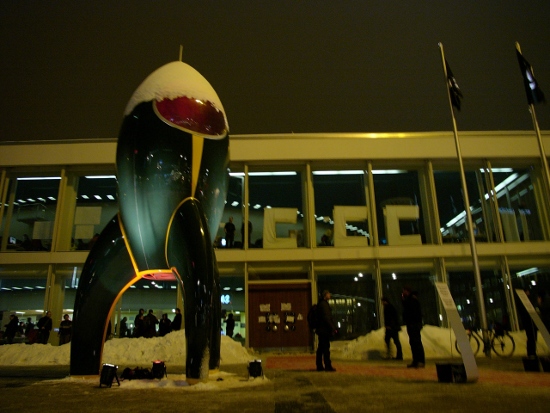

Since Monday, my colleagues and I have been attending the annual Chaos Communication Congress 27C3 in Berlin. For the past 27 years, the Chaos Computer Club has organised this four day conference for hackers from all over the world.
The sold-out event at Berlin’s bcc covers a wide range of topics, separated into six different tracks: Community, Culture, Hacking, Making, Science and Society. Take a look at what’s known as the Fahrplan or schedule.
All the talks are streamed and recorded. Check out the conference wiki.
Yesterday also marked the start of a new, CCC independent side event called BerlinSides, which focuses on infosec and is organised by Aluc.TV and SecurityBsides.com. This free event takes place at one of the oldest hackerspaces in the world, Berlin’s famous c-base.
Latest Webinars
Reports
Kaspersky researchers have discovered new Mirage Kitten attacks using previously undocumented malware families: NodeRabbit in Node.js and PollCat in JavaScript.
Our experts discovered a new CoolClient backdoor variant with a kernel-mode rootkit driver that hides malicious processes, files, and network connections from security tools and threat analysts.
Kaspersky experts break down a new Armored Likho campaign that poses as a fundraising efforts and delivers a new Still Toolkit aimed at stealing Telegram data and eavesdropping on victims.
Kaspersky researchers reveal previously undocumented malware attributed to Mirage Kitten (UNC1549, Smoke Sandstorm, Nimbus Manticore): NightLedger backdoor, ArcBridge, and BridgeHead tunneling tools.
Text extracted automatically; images, tables and formatting may be missing. Original: https://securelist.com/we-come-in-peace-too-impressions-from-cccs-27c3-berlin/29804/