UK election admin agency breach exposed personal information of tens of millions voters
Full article786 words · extracted from cyberscoop.com · click to collapse
Get our latest cybersecurity news first on Google.
The voter registries were accessed over a period of more than a year, the agency said.
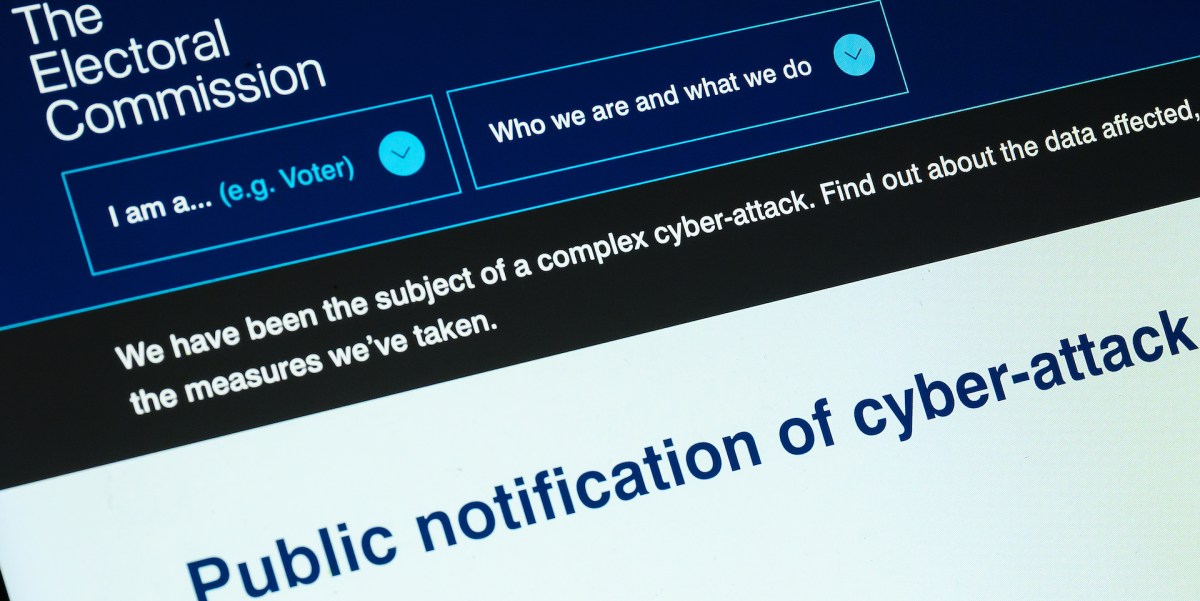
Hackers accessed and lurked inside certain servers within the United Kingdom’s top election administration agency for nearly a year as a result of a “complex cyber-attack,” the agency announced Tuesday.
The unknown intruders had access to servers related to the agency’s email, control systems and copies of electoral registers, according to a statement posted to its website. The Electoral Commission, an independent body that oversees elections and political finance in the United Kingdom, said that “hostile actors” first accessed the servers in August 2021. The breach was identified in October 2022 and publicly revealed Tuesday.
The hackers accessed copies of voter registries which included the names and addresses of any U.K. voters registered between 2014 and 2022. The information accessed by the hackers also included email addresses among other information, potentially putting information associated with tens of millions people at risk. The agency noted that “much” of the data is already in the public domain, but that it “is possible however that this data could be combined with other data in the public domain, such as that which individuals choose to share themselves, to infer patterns of [behavior] or to identify and profile individuals.”
The agency said it’s not clear who was responsible for the attack and that there have been no claims of responsibility made.
A spokesperson for U.K.’s National Cyber Security Centre said the agency “provided the Electoral Commission with expert advice and support to aid their recovery after a cyber incident was first identified. Defending the UK’s democratic processes is a priority for the NCSC and we provide a range of guidance to help strengthen the cyber resilience of our electoral systems.”
Will Thomas, a UK-based CTI researcher at Equinix, tweeted that the voter database is a “prime target for any hostile intelligence services that consistently target the UK.” Like the massive 2015 breach of the Office of Personnel Management in the U.S., Thomas wrote, “these records have years of personal data that can be used to enrich other datasets for targets of interest, such as details about members of security services, military, and the [government].”
Thomas told CyberScoop in an online message that based on what’s known so far, and given the hackers’ access for nearly 15 months “while also exfiltrating a large amount of critical databases,” the attack was complex, as the agency suggested.
“There was no ransomware deployment and no threat actor attempting data extortion,” Thomas said. “This was very likely an intrusion by a foreign intelligence agency.”
Updated, Aug. 8, 2023: This story has been updated to include a comment from the U.K.’s National Cyber Security Centre.
More Scoops
UK spy chief labels AI ‘unstoppable force’ with offensive, defensive ramifications for cyberspace
Anne Keast-Butler, head of the GCHQ, said her agency was developing an artificial intelligence-powered cyber shield as other nations were deploying AI in warfare.
US, UK agencies warn hackers were hiding on Cisco firewalls long after patches were applied
Feds quash widespread Russia-backed espionage network spanning 18,000 devices
Latest Podcasts
Government
FBI officials say AI is bolstering adversaries, emphasizing need to focus on cyber basics, patching
CIA’s Michael Ellis says cyber intelligence is changing how the agency operates
The G7 tells industry to hurry up and prep for post-quantum encryption
Jail time for Maine child in 764 marks turning point in federal law enforcement
Technology
Threats
Policy
Whistleblower says USPS deploying new, ‘untested’ IT systems governing mail-in ballots
‘Watershed 250’ test program in Texas looks to private sector for water cybersecurity help
Former sexual abuse victims say Grok used their images, videos to train deepfake capabilities
Cyber threats nudge Trump to sign executive order on foreign equipment in U.S. energy infrastructure
Text extracted automatically; images, tables and formatting may be missing. Original: https://cyberscoop.com/u-k-election-admin-agency-servers-breach-exposed-voter-information-of-tens-of-millions/