Do you like photos?
Full article299 words · extracted from securelist.com · click to collapse



This week we’ve seen a couple of IM-Worms peaking above the radar to an extent you can probably call epidemic levels.
Two of these were MSN-Worms. Each worm sends a link:
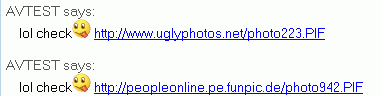
Each of the links lead to a different Trojan-downloader. The downloaders download a variety of adware and adware-related Trojans.
Moreover, IM-Worm.Win32.Licat.c is also downloaded, which in turn launches a new mass mailing of the original message. Nothing unusual, right?
Wrong! Both worms spread using links to .PIF files. But some of you might remember that Microsoft blocked messages containing “.pif”?
Yes they have, but… the MS block is case sensitive!
So the criminals used capital letters, “.PIF” and the network filters let the message flow right through. Other variations like .Pif, .pIf, and so on also work.
We have notified Microsoft of this and hope they take the necessary actions. In the meantime, users and admins should beware.
The funpic.de page has been taken down during the night and the uglyphotos link is dead and blocked by MSN. But there’s no doubt there will be new ones to replace it. Especially with the VML vulnerability still un-patched.
Latest Webinars
Reports
Kaspersky researchers have discovered new Mirage Kitten attacks using previously undocumented malware families: NodeRabbit in Node.js and PollCat in JavaScript.
Our experts discovered a new CoolClient backdoor variant with a kernel-mode rootkit driver that hides malicious processes, files, and network connections from security tools and threat analysts.
Kaspersky experts break down a new Armored Likho campaign that poses as a fundraising efforts and delivers a new Still Toolkit aimed at stealing Telegram data and eavesdropping on victims.
Kaspersky researchers reveal previously undocumented malware attributed to Mirage Kitten (UNC1549, Smoke Sandstorm, Nimbus Manticore): NightLedger backdoor, ArcBridge, and BridgeHead tunneling tools.
Text extracted automatically; images, tables and formatting may be missing. Original: https://securelist.com/do-you-like-photos/30230/