We help you to survive this crisis!
Full article237 words · extracted from securelist.com · click to collapse



There have been a lot of variants of Email-Worm.Win32.Iksmas around lately. Now that Valentine’s Day is over, we might have expected to see a few less of them, but no.
There’s been a new flood of mass mailings spreading Iksmas – instead of professions of endless love, these messages are offering money saving coupons. And who’s going to say no to a special offer?
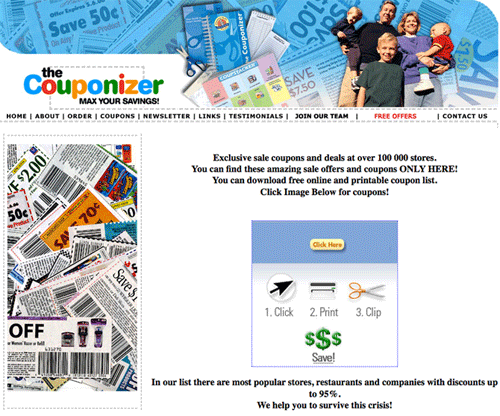
The name of the worm executable varies, but all the names have one thing in common – save.exe, nocrisis.exe, etc. all reference the economic situation.
Of course, special offers are great, and we could all use a bit more cash.But stick to offers you know are genuine; if you go for scams like this, you’re just putting money in the spammers’ pockets.
Latest Webinars
Reports
Kaspersky researchers have discovered new Mirage Kitten attacks using previously undocumented malware families: NodeRabbit in Node.js and PollCat in JavaScript.
Our experts discovered a new CoolClient backdoor variant with a kernel-mode rootkit driver that hides malicious processes, files, and network connections from security tools and threat analysts.
Kaspersky experts break down a new Armored Likho campaign that poses as a fundraising efforts and delivers a new Still Toolkit aimed at stealing Telegram data and eavesdropping on victims.
Kaspersky researchers reveal previously undocumented malware attributed to Mirage Kitten (UNC1549, Smoke Sandstorm, Nimbus Manticore): NightLedger backdoor, ArcBridge, and BridgeHead tunneling tools.
Text extracted automatically; images, tables and formatting may be missing. Original: https://securelist.com/we-help-you-to-survive-this-crisis/30489/