Smishing Triad Hackers Use JWR Phishing Kit to Steal Cards, OTPs and Bank Credentials
Group-IB attributes large-scale smishing using the JWR real-time phishing kit to the Smishing Triad's Outsider cluster, harvesting card data, OTPs, and bank credentials.
Group-IB attributes a large-scale SMS phishing campaign to Outsider, an operator sub-cluster within the Smishing Triad phishing-as-a-service ecosystem, using a kit dubbed JWR. The Vue 2-based platform maintains real-time WebSocket communication with operators, enabling them to adapt pages live and harvest roughly 70 PII fields, card data, PINs, OTPs, identity document images, and digital wallet credentials via a dedicated PayPal sub-funnel. Unit 42 previously tied 194,345 malicious domains across 136,933 root domains to the broader operation since January 2024. Defenders can hunt for /api/open/ endpoints, /webSocket/QT/ paths, JWR-prefixed storage artifacts, and a hard-coded WebSocket token.
- Outsider operates as a customer within the Smishing Triad phishing-as-a-service ecosystem
- JWR uses Vue 2 SPA and Web Worker with WebSocket channels for real-time operator interaction
- Kit collects ~70 PII fields, identity document images, three credential slots, and a PayPal sub-funnel
- Detection markers include /api/open/ endpoints, /webSocket/QT/ path, and hard-coded WebSocket token
- Unit 42 linked 194,345 malicious domains across 136,933 root domains since January 2024
Full article734 words · extracted from gbhackers.com · click to collapse
A large-scale SMS phishing campaign linked to the Smishing Triad is using a sophisticated phishing kit dubbed JWR to harvest payment-card data, one-time passwords, online-banking credentials, identity information, and digital-wallet logins.
Group-IB attributed the activity to an operator sub-cluster tracked as Outsider, which appears to operate as a customer within the wider phishing-as-a-service ecosystem rather than as an independent operation.
The messages create urgency by asking recipients to complete a verification, pay an alleged unpaid fee, or reconfirm parcel-delivery details.
Victims who click are routed through shortened URLs to fast-changing, disposable phishing domains hosting the JWR framework.
JWR differs from conventional static phishing pages because it operates as a real-time fraud platform.
The kit uses a Vue 2 single-page application and a dedicated Web Worker to maintain communication between the victim’s browser and an operator-controlled backend.
Stolen information is sent through binary WebSocket traffic, with a two-second HTTP long-polling fallback if the WebSocket channel fails.
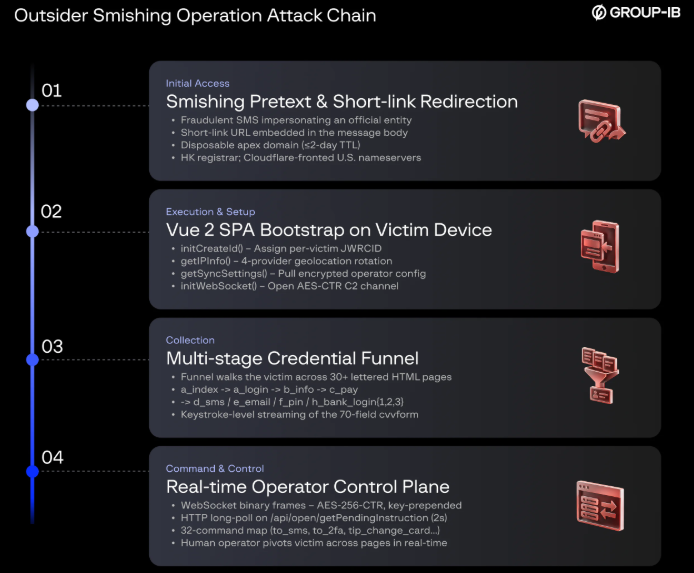
This architecture lets fraud operators observe a victim’s activity while it is happening and alter the next page in the phishing flow.
JWR Phishing Kit
Rather than relying on a fixed sequence of forms, an operator can direct a target toward SMS-OTP prompts, banking-login pages, app-confirmation screens, QR-code verification pages, card-declined messages, or alternative card-entry forms based on the information already provided.
GroupIB Researchers said that, the campaign begins with fraudulent SMS messages impersonating trusted entities such as delivery companies, toll services, government organizations, or financial institutions.
The result is a highly interactive social-engineering process. Once a victim submits a card number, the operator can inspect the card’s BIN details, request an OTP, redirect the victim to a bank-login page, or attempt to collect credentials for another financial institution.
This approach allows the criminals to adapt the lure to the victim’s bank, payment method, and authentication requirements in near real time.
Researchers found that the JWR kit’s central data model contains roughly 70 fields designed to collect a broad range of personally identifiable information.
The fields cover names, addresses, phone numbers, email addresses, dates of birth, government identity numbers, payment-card details, card PINs, device data, browser cookies, IP addresses, and geolocation information.
The framework can also request images of identity documents, including passports, driver’s licenses, social security cards, and medical IDs.
Some prompts seek “handheld” document images, effectively selfies showing the victim holding an identity document. Such data can support account-takeover attempts, identity fraud, and efforts to bypass Know Your Customer re-verification processes.
JWR additionally includes three separate credential slots for online accounts, enabling attackers to collect credentials for multiple banks, brokerages, or other financial services during the same session.
A dedicated PayPal-focused sub-funnel expands the kit’s reach to digital-wallet targets.
The kit encrypts WebSocket frames and HTTP traffic sent to /api/open/ endpoints using AES-256-CTR.
However, the implementation provides little meaningful confidentiality because each message contains the 32-byte AES key and 16-byte initialization vector in cleartext before the ciphertext.
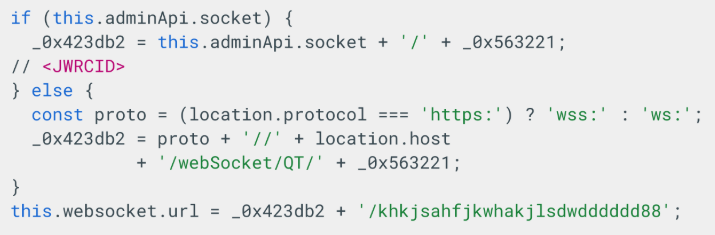
Group-IB noted that the design is more likely intended to obscure JSON-formatted stolen data from casual network inspection than to prevent determined defenders from decrypting it.
This behavior creates valuable detection opportunities. Network defenders can hunt for the kit’s /api/open/ endpoint structure, /webSocket/QT/ path, JWR-prefixed browser storage artifacts, and a hard-coded WebSocket token ending in khkjsahfjkwhakjlsdwdddddd88.
These markers can help incident responders link otherwise unrelated phishing domains to the same JWR family.
The Smishing Triad is widely assessed as a criminal marketplace involving phishing-kit developers, SMS spammers, domain operators, hosting providers, and target-data brokers.
Palo Alto Networks Unit 42 identified 194,345 malicious fully qualified domain names spanning 136,933 root domains associated with the broader operation since January 2024.
For organizations, the key defensive priority is continuous monitoring of SMS-linked brand impersonation, rapid takedown of newly registered phishing infrastructure, and detection engineering focused on the kit’s distinctive network and client-side indicators.
For users, unsolicited SMS links requesting payments, identity verification, or OTP submission should be treated as hostile until verified independently through an official app, bookmarked website, or published customer-service channel.
★ Learn 7 Metric-Gated AI SOC Deployment Phases – Download Free AI SOC Deployment Playbook 2026.
Mayura Kathirhttps://gbhackers.com/
Mayura Kathir is a cybersecurity reporter at GBHackers News, covering daily incidents including data breaches, malware attacks, cybercrime, vulnerabilities, zero-day exploits, and more.
Text extracted automatically; images, tables and formatting may be missing. Original: https://gbhackers.com/jwr-phishing-kit/