Malware Calendar Wallpaper for October 2011
Full article352 words · extracted from securelist.com · click to collapse
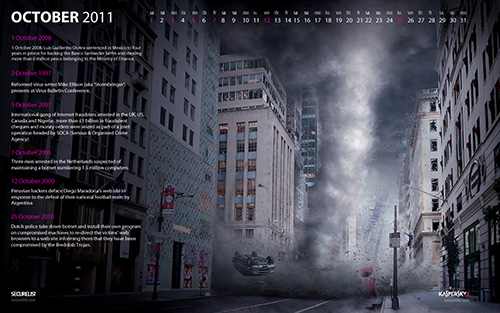

Here’s the latest of our malware calendar wallpapers.
1280×800 | 1680×1050 | 1920×1200 | 2560×1600


This month’s wallpaper highlights the worldwide nature of cybercrime.
The Internet has made the world a very small place. Once we connect, we’re able to access web resources anywhere in the world. This has had a profound effect on online criminality. Unlike real-world criminals, who must have sight of their victims, the Internet means that we can all become the potential targets of cybercriminals who may be located anywhere in the world. Cybercrime is, therefore, a worldwide phenomenon.
This doesn’t mean that malware development is spread evenly across the globe. There have always been development ‘hot-spots’ focused on creation of certain types of malware. For example, botnet development in Russia, or the creation of banking Trojans in Latin America.
There can also be victim ‘hot-spots’ too. This may occur where the use of computers – and the Internet – is developing rapidly, but where the level of awareness of the risks is low. Or where a target operating system has a high install-base – as with the spread of fake anti-virus programs for Mac OS in the second quarter of 2011.
If you’re interested in finding out more about the geography of malware, take a look at our report IT threat evolution: Q2 2011
And wherever you live or work, it’s important to understand the risks and take appropriate action to reduce your exposure to them.
Latest Webinars
Reports
Kaspersky researchers have discovered new Mirage Kitten attacks using previously undocumented malware families: NodeRabbit in Node.js and PollCat in JavaScript.
Our experts discovered a new CoolClient backdoor variant with a kernel-mode rootkit driver that hides malicious processes, files, and network connections from security tools and threat analysts.
Kaspersky experts break down a new Armored Likho campaign that poses as a fundraising efforts and delivers a new Still Toolkit aimed at stealing Telegram data and eavesdropping on victims.
Kaspersky researchers reveal previously undocumented malware attributed to Mirage Kitten (UNC1549, Smoke Sandstorm, Nimbus Manticore): NightLedger backdoor, ArcBridge, and BridgeHead tunneling tools.
Text extracted automatically; images, tables and formatting may be missing. Original: https://securelist.com/malware-calendar-wallpaper-for-october-2011-5/31257/