NATO countries' refugee management may have been targeted by Belarus
Full article809 words · extracted from cyberscoop.com · click to collapse
Get our latest cybersecurity news first on Google.
A phishing campaign aimed at countries taking refugees is potentially linked to a group known to researchers as TA445, UNC1151 or Ghostwriter.
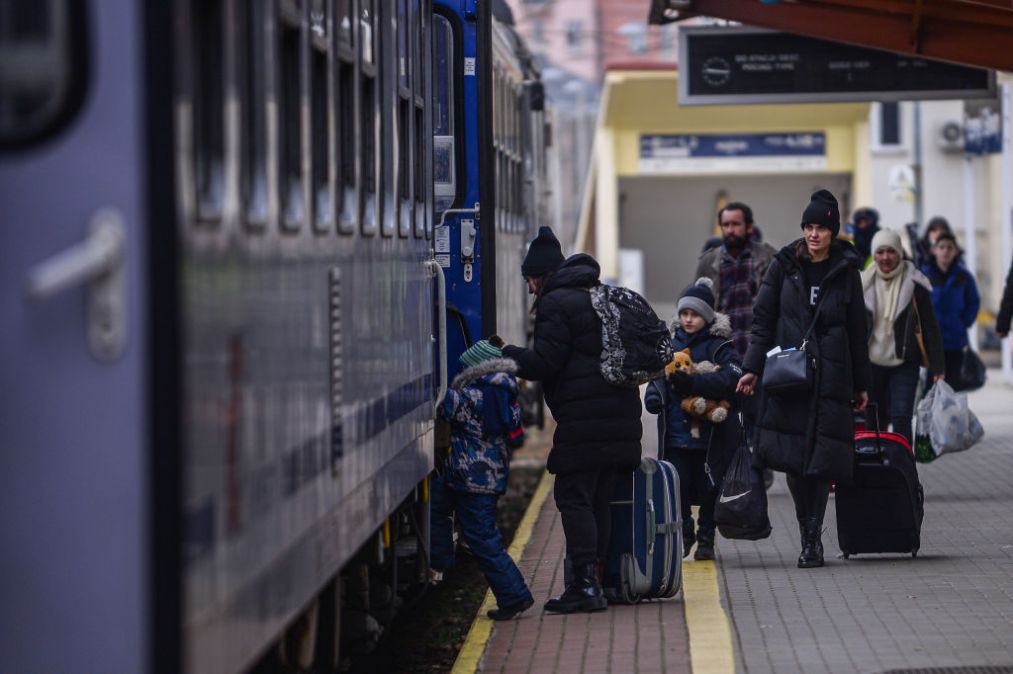
A hacking group with a history of phishing attacks and disinformation against NATO nations may be using compromised Ukrainian armed service member emails to target European officials tasked with managing logistics around refugees fleeing Ukraine, according to findings published Monday.
Researchers with cybersecurity firm Proofpoint report they detected an email Feb. 24 that carried a subject referencing the Feb. 24 emergency meeting of NATO on the day the Russian government began its military attack on Ukraine. The email included an attached Microsoft Excel spreadsheet titled “list of persons.xlsx” that the researchers later determined included malware that, if installed, sought to gather information and intelligence from target computers.
The social engineering lure used in this campaign was timely, the researchers said, given the NATO meeting and “a news story about a Russian government ‘kill list’ targeting Ukrainians that began circulating in Western media outlets” Feb. 21.
Proofpoint did not definitively attribute the campaign, but “several temporal and anecdotal indicators exist” suggesting activity associated with a group tracked variously as TA445, UNC1151 or Ghostwriter. The group — with a documented history of disinformation efforts aimed at manipulating sentiment about refugees in NATO countries — is believed to be operating out of Minsk in furtherance of Belarusian and Russian government objectives.
On Feb. 25, the day after the phishing emails were sent, the Ukrainian government Computer Emergency Response Team posted a warning about “mass phishing emails” targeting the accounts of Ukrainian military personnel and related individuals, and attributed the effort to UNC1151 and the Ministry of Defense of the Republic of Belarus.
Proofpoint’s researches note that the data observed allowed for only “limited conclusions” about the targets of the campaign, but noted they were “European governmental entities” with a range of professional responsibilities but were mostly tide to transportation, financial and budget allocation, administration, and population movement within Europe.
“This campaign may represent an attempt to gain intelligence regarding the logistics surrounding the movement of funds, supplies, and people within NATO member countries,” the researchers wrote.
“While the utilized techniques in this campaign are not groundbreaking individually, if deployed collectively, and during a high tempo conflict, they possess the capability to be quite effective,” the researchers wrote. “As the conflict continues, researchers assess similar attacks against governmental entities in NATO countries are likely.”
More Scoops
Multi-national warning issued over Russia’s targeting of logistics, tech firms
The campaign traces back at least to early 2022, coinciding with the start of Russia’s full-scale invasion of Ukraine.
Hacks, leaks and wipers: Google analyzes a year of Russian cyberattacks on Ukraine
Russian hackers attempted to breach petroleum refining company in NATO country, researchers say
Hackers linked to the Chinese government increasingly target Russia, analysis suggests
Hacktivist personas back latest GhostWriter disinfo op targeting Poland, Ukraine
Multiple government hacking groups stay busy targeting Ukraine and the region, Google researchers say
Russian, Chinese, Belarusian hackers increasingly using Ukraine-themed lures in attacks, Google observes
Latest Podcasts
Government
FBI officials say AI is bolstering adversaries, emphasizing need to focus on cyber basics, patching
Feds accuse China of ‘systematic’ distillation of U.S. AI models
CIA’s Michael Ellis says cyber intelligence is changing how the agency operates
The G7 tells industry to hurry up and prep for post-quantum encryption
Technology
Threats
Policy
Whistleblower says USPS deploying new, ‘untested’ IT systems governing mail-in ballots
‘Watershed 250’ test program in Texas looks to private sector for water cybersecurity help
Former sexual abuse victims say Grok used their images, videos to train deepfake capabilities
Cyber threats nudge Trump to sign executive order on foreign equipment in U.S. energy infrastructure
Text extracted automatically; images, tables and formatting may be missing. Original: https://cyberscoop.com/ghostwriter-phishing-refugees-nato-russia-ukraine/