Clinton's encryption solution would require a ton of oversight
Full article1,012 words · extracted from cyberscoop.com · click to collapse
Get our latest cybersecurity news first on Google.
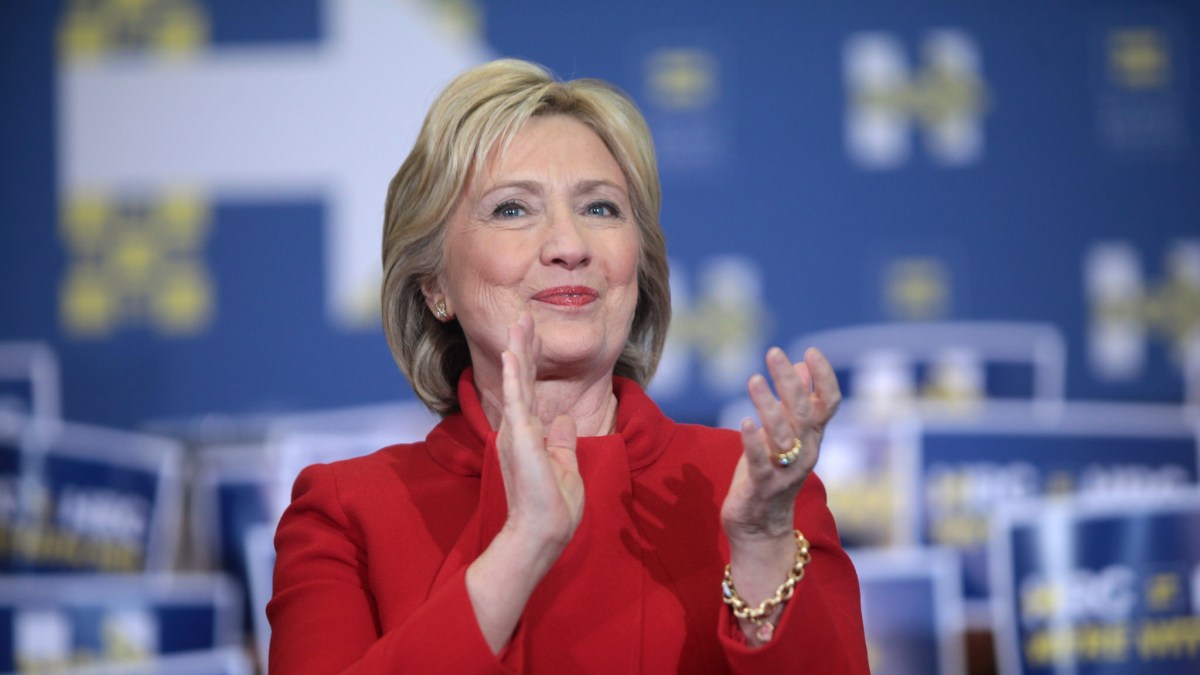
If Hillary Clinton wins the White House, her supposed opinion on encryption could lead to unintended consequences and regulatory necessities, experts warn.
Law enforcement taking advantage of zero day exploits is preferred to an overarching encryption “backdoor” law, a group of cryptography, security policy and digital privacy experts said Friday during a panel discussion at the 2016 CyCon U.S. cybersecurity conference.
And yet, those experts say the inherent dangers in relying on zero days cannot be ignored.
Globally, all data will eventually be encrypted, according to Matthew Green, an assistant professor at the Johns Hopkins Information Security Institute. Not all encryption will be or is currently considered “equal,” however; some communications will always be susceptible to surveillance. Effective crypto, absent of any flaw or vulnerability, remains difficult to design, Green explained, meaning that avenues to overstep encryption do exist.
This question of deciding between targeted government hacking and mandated backdoors recently received renewed attention due to a leaked conversation between a group of political advisors to democratic presidential nominee Hillary Clinton. According to a series of private emails published by Wikileaks, Clinton supposedly prefers select, government hacking to creating backdoors in certain software products.
If Clinton’s supposed opinion on encryption were to manifest into official policy though then it could lead to unintended consequences and regulatory necessities, the panel warned.
“If we’re going to condone the use of zero days and finding vulnerabilities in systems, then we have this problem of nondisclosure where the government knows about a vulnerability, and maybe is sharing with other governments, but the general public does not. And so we’re just trading one security problem for another,” said Heather West, public policy leader for the Americas for Mozilla.
When hackers themselves can’t break into a system, they can purchase an exploit or hacking services from a third party. Such was the case earlier this year when the FBI purchased an exploit to unlock an iPhone 5C belonging to a dead terrorist.
“This [zero day] industry is growing by leaps and bounds regardless; as it is already being used by law enforcement and governments around the world,” said Citizen Lab senior researcher Sarah McKune, “[but] I think what is being considered here, is that strong encryption protects at scale whereas targeted intrusions tied specifically to identified individuals — done lawfully — is favored.”
The current, voluntary process in place to disclose software flaws on the part of the U.S. government — known as the vulnerabilities equities process — is a transparent first step, but it alone will not suffice in an environment where the White House is in favor of hacking in the face of inaccessible criminal evidence, explained Trey Herr, a postdoctoral fellow at the Belfer Center’s Cybersecurity Project at the Harvard Kennedy School.
“If the next president takes that approach, we won’t know about it, as it would be classified to ensure uncertainty. It would be a potentially dangerous road for the U.S. government to officially take, as it is inherently beyond the purview of transparency. I can’t begin to list the unintended consequences such a policy shift would entail,” said Matt Mayer, a visiting fellow focused on homeland security and counterterrorism studies at the American Enterprise Institute.
If Clinton’s reported favorability toward government hacking were to become law, then it would require the creation of new regulation, controls and oversight, the panel of experts unanimously agreed. Importantly, this oversight should not only curtail domestic use of hacking tools but also the purchase and sale of such weapons elsewhere by U.S. entities, McKune added.
“There are a range of options that law enforcement can turn to aside from mandated backdoors,” Ross Schulman, senior policy counsel at New America’s Open Technology Institute, previously told CyberScoop. “If government hacking is a route that we go down, however, Congress has to set clear rules of the road. Right now, the FBI is operating in the dark and without guidance.”
More Scoops
CISA official advises agencies not to get too hung up on who takes lead in critical infrastructure sectors
Acting director Nick Andersen said relationships, not actor risk management agency designations, should guide which agency is at the forefront.
New National Cyber Director Cairncross faces challenges on policy, bureaucracy, threats
Senate legislation would direct federal agencies to fortify against quantum computing cyber threats
Latest Podcasts
Government
FBI officials say AI is bolstering adversaries, emphasizing need to focus on cyber basics, patching
Feds accuse China of ‘systematic’ distillation of U.S. AI models
CIA’s Michael Ellis says cyber intelligence is changing how the agency operates
Jail time for Maine child in 764 marks turning point in federal law enforcement
Technology
Threats
Policy
Whistleblower says USPS deploying new, ‘untested’ IT systems governing mail-in ballots
‘Watershed 250’ test program in Texas looks to private sector for water cybersecurity help
Former sexual abuse victims say Grok used their images, videos to train deepfake capabilities
Cyber threats nudge Trump to sign executive order on foreign equipment in U.S. energy infrastructure
Text extracted automatically; images, tables and formatting may be missing. Original: https://cyberscoop.com/hillary-clinton-encryption-zero-day-government-hacking/