Maersk may lose up to $300M due to NotPetya attack
Full article595 words · extracted from cyberscoop.com · click to collapse
Get our latest cybersecurity news first on Google.
The Danish shipping behemoth says the attack was a “significant business interruption.”
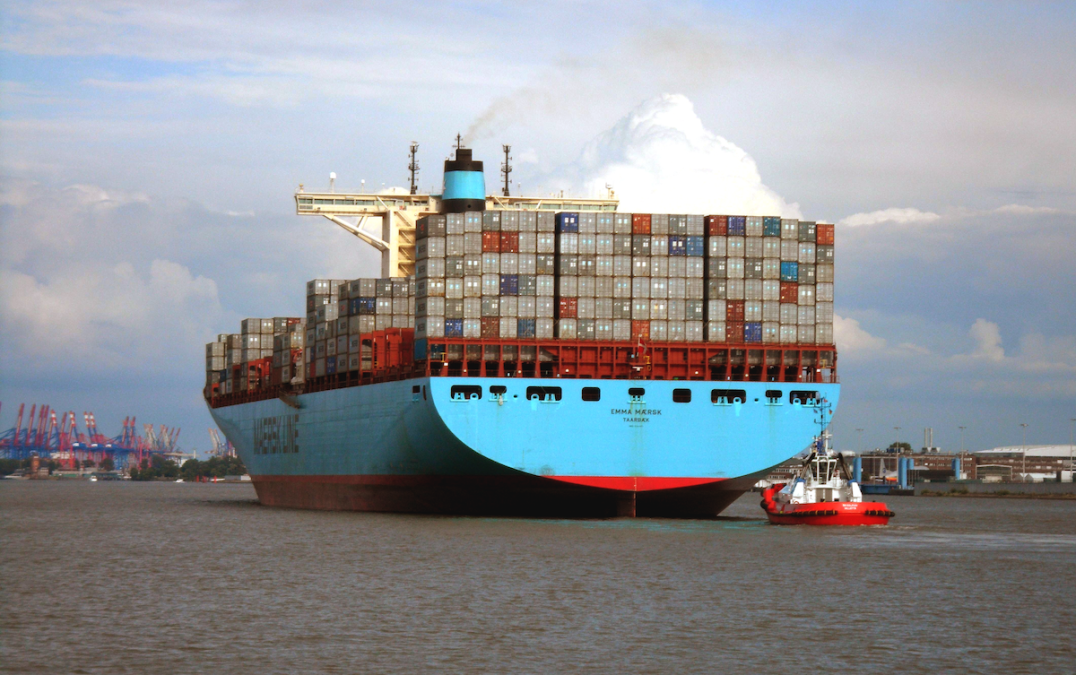
The world’s largest container shipping company, A.P. Moller-Maersk, has said that it expects as much as a $300 million dip in profits due to a June 27 ransomware incident, the firm noted in a public report released Wednesday.
Maersk executives said they expected losses of between $200 million and $300 million — which will be reflected in the next earnings report — because of a “significant business interruption” caused by the spread of a ransomware variant known as NotPetya inside corporate networks.
The disclosure was attached to Maersk’s second-quarter earnings report. Public companies are required to publicly update their investors on the state of the business once every fiscal quarter.
While NotPetya was engineered to look like ordinary ransomware, the virus held hidden code that would delete files on an infected computer. Ransomware is not typically designed to be destructive. In most cases, ransomware operators hope to encrypt files on a system until a payment is received.
Experts say NotPetya carried indicators previously tied to a group of Russian hackers, codenamed Telebots or Sandworm group. CyberScoop previously reported that NotPetya was intended to be “destructive” in nature. The ransomware largely targeted companies based in Ukraine, according to analysis conducted by cybersecurity firm ESET and Cisco’s threat intelligence unit, Talos.
“The malware was contained to only impact the container related businesses of A.P. Moller – Maersk, and therefore six out of nine businesses, including all Energy businesses, could uphold normal operations,” Maersk stated. “These system shutdowns resulted in significant business interruption during the shutdown period, with limited financial impact in Q2, while the impact in Q3 is larger.”
Denmark-based Maersk has at least one office based in the country. Security researchers believe NotPetya spread to companies based outside of Ukraine because some foreign businesses were connected to Ukrainian enterprises through VPN services.
According to research conducted by Kaspersky Lab and ESET, the “patient zero” behind Petya is a popular Ukrainian accounting software firm named M.E. Doc. A booby-trapped software update was rolled out by the company to unsuspecting users earlier this year. A hacker was able to penetrate M.E. Doc at some point in time and infect the company’s software update mechanism. Ukraine police ultimately shut down operations and confiscated hardware from M.E. Doc in early July.
Latest Podcasts
Government
FBI officials say AI is bolstering adversaries, emphasizing need to focus on cyber basics, patching
Feds accuse China of ‘systematic’ distillation of U.S. AI models
CIA’s Michael Ellis says cyber intelligence is changing how the agency operates
Jail time for Maine child in 764 marks turning point in federal law enforcement
Technology
Threats
Policy
Whistleblower says USPS deploying new, ‘untested’ IT systems governing mail-in ballots
‘Watershed 250’ test program in Texas looks to private sector for water cybersecurity help
Former sexual abuse victims say Grok used their images, videos to train deepfake capabilities
Cyber threats nudge Trump to sign executive order on foreign equipment in U.S. energy infrastructure
Text extracted automatically; images, tables and formatting may be missing. Original: https://cyberscoop.com/maersk-notpetya-300-million-loss/