Nyxem.e’s dreaded 32 bytes
Full article226 words · extracted from securelist.com · click to collapse



Somewhere, deep inside Nyxem.e’s 100K+ body, there is a dreaded block of 32 bytes. On the 3rd of every month, exactly 30 minutes after the infected system is started, Nyxem.e will use this block to overwrite all *.doc, *.xls, *.mdb, *.mde, *.ppt, *.pps, *.zip, *.rar, *.pdf, *.psd and *.dmp files on your disks.
Once this has happened, your 6MB presentation for the CEO, your vacation pictures and all the RAR and ZIP backups will look like this:

Or, in ASCII:
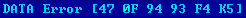
With the activation date drawing near, just make sure your system is not infected. Unlike GPCode, once the payload has hit, the chances of you getting your data back will be practically zero.
Latest Webinars
Reports
Kaspersky researchers have discovered new Mirage Kitten attacks using previously undocumented malware families: NodeRabbit in Node.js and PollCat in JavaScript.
Our experts discovered a new CoolClient backdoor variant with a kernel-mode rootkit driver that hides malicious processes, files, and network connections from security tools and threat analysts.
Kaspersky experts break down a new Armored Likho campaign that poses as a fundraising efforts and delivers a new Still Toolkit aimed at stealing Telegram data and eavesdropping on victims.
Kaspersky researchers reveal previously undocumented malware attributed to Mirage Kitten (UNC1549, Smoke Sandstorm, Nimbus Manticore): NightLedger backdoor, ArcBridge, and BridgeHead tunneling tools.
Text extracted automatically; images, tables and formatting may be missing. Original: https://securelist.com/nyxem-es-dreaded-32-bytes/30127/