Mistyping leads to infections!
Full article307 words · extracted from securelist.com · click to collapse



Cybercriminals like to register domain names that are very similar to actual, well known domain names but with one or more letters changed. In many cases a potential victim will mistype a letter and in this way arrives at a fake Web site instead of the original one.
Here is just one example of this: a copy of the official Russian Web page of Kaspersky. The criminals added just one small line inside of the ‘downloads’ tab promoting a fake download for a free, one year copy of Kaspersky Internet Security 2011.
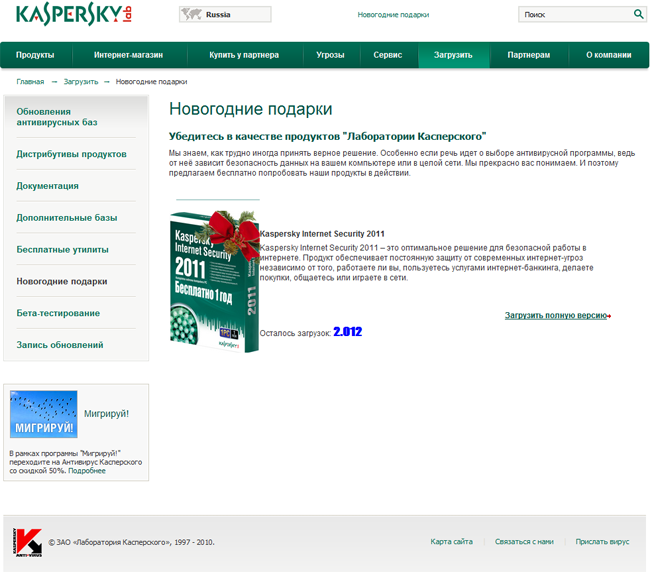
Instead of KIS 2011 the victim gets malware. This is ransomware which, after the installation, forces a reboot of your PC. Upon completing the reboot the malware shows a fake message that you’ve won a prize of a Samsung Galaxy S cellphone for just 1200 rubles (40 USD)! To claim this prize, you should pay via SMS text or, optionally through one of the popular on-line payments systems in Russia.
Kaspersky Anti-Virus detects this threat as Trojan-Ransom.MSIL.FakeInstaller.e
In the time of writing of this blogpost the malicious site was still on-line and also detected by Kaspersky Internet Security Web Anti-Virus as a fraudulent one.
Latest Webinars
Reports
Kaspersky researchers have discovered new Mirage Kitten attacks using previously undocumented malware families: NodeRabbit in Node.js and PollCat in JavaScript.
Our experts discovered a new CoolClient backdoor variant with a kernel-mode rootkit driver that hides malicious processes, files, and network connections from security tools and threat analysts.
Kaspersky experts break down a new Armored Likho campaign that poses as a fundraising efforts and delivers a new Still Toolkit aimed at stealing Telegram data and eavesdropping on victims.
Kaspersky researchers reveal previously undocumented malware attributed to Mirage Kitten (UNC1549, Smoke Sandstorm, Nimbus Manticore): NightLedger backdoor, ArcBridge, and BridgeHead tunneling tools.
Text extracted automatically; images, tables and formatting may be missing. Original: https://securelist.com/mistyping-leads-to-infections/29811/