Former White House cyber director: Expect another Shadow Brokers incident
Full article920 words · extracted from cyberscoop.com · click to collapse
Get our latest cybersecurity news first on Google.
Another Shadow Brokers-like incident — in which unprecedented, older software vulnerabilities are indiscriminately posted online for everyone to see — should be expected in the “near future,” said former White House National Security Council Senior Director for Cybersecurity Ari Schwartz.
Another incident in which a trove of previously undiscovered software vulnerabilities are publicly posted online should be expected in the “near future,” said former White House National Security Council Senior Director for Cybersecurity Ari Schwartz.
In the past, the U.S. government has kept quiet when software vulnerabilities are discovered. Now, even while some of those exploits are dated or no longer work, they pose a public relations risk and raise transparency questions when they are exposed to the masses.
Schwartz told FedScoop he expects incidents — like the leak of exploits from the NSA-linked Equation Group — to be commonplace because the government is undoubtedly aware of old, never before disclosed software flaws in private sector products.
[Read More: Random hackers are taking NSA-linked cyber weapons for a test drive]
“It would be better to have vulnerabilities shared with vendors directly from the U.S. government rather than having them leak out from other sources attributed to the U.S. government,” Schwartz told FedScoop, referencing the disclosure of stolen NSA-owned cyber weapons made possible by a mysterious group calling themselves the Shadow Brokers.
“It is dangerous to see a leak like this with literally no time to patch,” he added.
Following publication of the aforementioned software exploits — which affect technologies developed by American companies Cisco, Fortinet and Juniper Networks — independent hackers were quick to copy the code, repurpose the exploits and launch new attacks. And because the vendors were previously unaware of the vulnerabilities, no security patches existed.
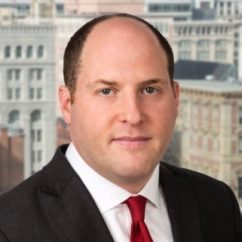
Venable LLP Managing Director of Cybersecurity Services Ari Schwartz
During Schwartz’s tenure at the White House, the administration worked to make changes to a once secretive software exploit disclosure process known as the Vulnerability Equities Process.
Following the Shadow Broker’s chronicle, the VEP is now attracting increased criticism from prominent voices in the information security community — many of whom believe the process is broken, evident by the NSA’s apparent negligence to responsibly disclose what appear to be hoarded, older zero-day exploits.
In March 2014, White House chief cybersecurity adviser Michael Daniel wrote about the VEP in an official White House blog post following reports linking the NSA to yet another vulnerability known as Heartbleed. In the blog post, Daniel described the policy as disclosure after discovery by default.
Schwartz, a key architect behind today’s post-2014 disclosure process, said that some of the criticism he has witnessed online concerning the VEP is unfair because the process was never designed to be “backward looking.” Exploits published by the Shadow Brokers reportedly date back to before both the 2014 transformation effort.
“There are only a limited number of individuals that work on vulnerabilities issues,” Schwartz, now a managing director at D.C. law firm Venable LLP, wrote to FedScoop in an email. “To have all of those experts spending time and effort looking through all of the old vulnerabilities to see which have been disclosed and which haven’t and having the ensuing conversation about each one would be devotion of resources that could instead be better spent on new vulnerability issues.
More Scoops
National cyber director lays out White House plans to secure AI without writing new rules
The Trump administration executive order on artificial intelligence tried to strike the balance between responsible use, security and mutual benefit, all with an eye toward not making…
White House cyber official: identity security matters more than ever in the age of AI

Announcing the winners of the 2025 CyberScoop 50 awards
Latest Podcasts
Government
FBI officials say AI is bolstering adversaries, emphasizing need to focus on cyber basics, patching
Feds accuse China of ‘systematic’ distillation of U.S. AI models
CIA’s Michael Ellis says cyber intelligence is changing how the agency operates
Jail time for Maine child in 764 marks turning point in federal law enforcement
Technology
Threats
Chinese espionage groups swarm to exploit triple-link chain of zero-days
Microsoft discloses two actively exploited zero-days among 974 vulnerabilities
Russian national extradited to US for alleged involvement in bank-account takeover scheme
Attackers exploit zero-days in consistently besieged SonicWall product
Policy
Whistleblower says USPS deploying new, ‘untested’ IT systems governing mail-in ballots
‘Watershed 250’ test program in Texas looks to private sector for water cybersecurity help
Former sexual abuse victims say Grok used their images, videos to train deepfake capabilities
Cyber threats nudge Trump to sign executive order on foreign equipment in U.S. energy infrastructure
Text extracted automatically; images, tables and formatting may be missing. Original: https://cyberscoop.com/former-white-house-cyber-director-expect-another-shadow-brokers-incident/