Cyber firm KnowBe4 hired a fake IT worker from North Korea
Full article798 words · extracted from cyberscoop.com · click to collapse
Get our latest cybersecurity news first on Google.
The security awareness training company said in a blog post that the software engineer used stolen U.S. credentials and an AI-enhanced photo.
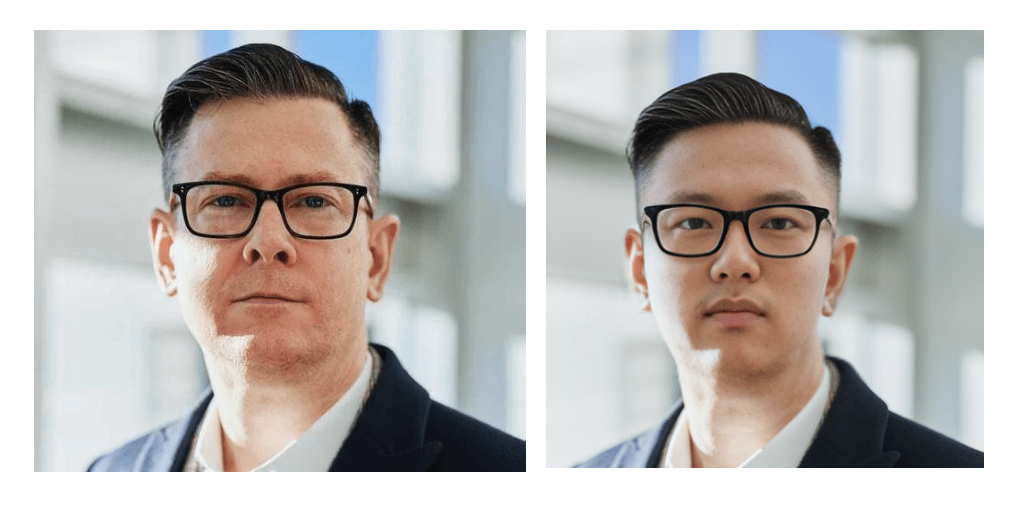
A remote worker hired by KnowBe4 as a software engineer on its internal IT team was actually a persona controlled by a North Korean threat actor, the security firm revealed in a blog post Tuesday.
Detailing a seemingly thorough interview process that included background checks, verified references and four video conference-based interviews, KnowBe4 founder and CEO Stu Sjouwerman said the worker avoided being caught by using a valid identity that was stolen from a U.S.-based individual. The scheme was further enhanced by the actor using a stock image augmented by artificial intelligence.
An internal investigation started when KnowBe4’s InfoSec Security Operations Center team detected “a series of suspicious activities” from the new hire. The remote worker was sent an Apple laptop, which was flagged by the company on July 15 when malware was loaded onto the machine. The AI-filtered photo, meanwhile, was flagged by the company’s Endpoint Detection and Response software.
Later that evening, the SOC team had “contained” the fake worker’s systems after he stopped responding to outreach. During a roughly 25-minute period, “the attacker performed various actions to manipulate session history files, transfer potentially harmful files, and execute unauthorized software,” Sjouwerman wrote in the post. “He used a [single-board computer] raspberry pi to download the malware.”
From there, the company shared its data and findings with the FBI and with Mandiant, the Google-owned cyber firm, and came to the conclusion that the worker was a fictional persona operating from North Korea.
KnowBe4 said the fake employee likely had his workstation connected “to an address that is basically an ‘IT mule laptop farm.’” They’d then use a VPN to work the night shift from where they actually reside — in this case, North Korea “or over the border in China.” That work would take place overnight, making it appear that they’re logged on during normal U.S. business hours.
“The scam is that they are actually doing the work, getting paid well, and give a large amount to North Korea to fund their illegal programs,” Sjouwerman wrote. “I don’t have to tell you about the severe risk of this.”
Despite the intrusion, Sjouwerman said “no illegal access was gained, and no data was lost, compromised, or exfiltrated on any KnowBe4 systems.” He chalked up the incident to a threat actor that “demonstrated a high level of sophistication in creating a believable cover identity” and identified “weaknesses in the hiring and background check processes.”
“This is a well-organized, state-sponsored, large criminal ring with extensive resources,” he wrote. “The case highlights the critical need for more robust vetting processes, continuous security monitoring, and improved coordination between HR, IT, and security teams in protecting against advanced persistent threats.”
Brian Jack, KnowBe4’s chief information security officer, said in an email to CyberScoop that “not a lot” has changed since the incident with the company’s cybersecurity controls given that the current controls “are what enabled us to detect this.”
“We are enhancing our hiring processes to include more thorough validation of identities prior to employment start date and are training all hiring staff on common red flags seen for this type of threat,” Jack added.
This story was updated July 24, 2024 with comments from KnowBe4.
Latest Podcasts
Government
FBI officials say AI is bolstering adversaries, emphasizing need to focus on cyber basics, patching
Feds accuse China of ‘systematic’ distillation of U.S. AI models
CIA’s Michael Ellis says cyber intelligence is changing how the agency operates
The G7 tells industry to hurry up and prep for post-quantum encryption
Technology
Threats
Microsoft discloses two actively exploited zero-days among 974 vulnerabilities
Russian national extradited to US for alleged involvement in bank-account takeover scheme
Attackers exploit zero-days in consistently besieged SonicWall product
Jail time for Maine child in 764 marks turning point in federal law enforcement
Policy
Whistleblower says USPS deploying new, ‘untested’ IT systems governing mail-in ballots
‘Watershed 250’ test program in Texas looks to private sector for water cybersecurity help
Former sexual abuse victims say Grok used their images, videos to train deepfake capabilities
Cyber threats nudge Trump to sign executive order on foreign equipment in U.S. energy infrastructure
Text extracted automatically; images, tables and formatting may be missing. Original: https://cyberscoop.com/cyber-firm-knowbe4-hired-a-fake-it-worker-from-north-korea/