Not just cyber: NASA CIO says all IT is about risk management
Full article590 words · extracted from cyberscoop.com · click to collapse
Get our latest cybersecurity news first on Google.
All IT has a "dark side" that must be contained, NASA CIO Renee Wynn told the FedScoop IT Modernization Summit.
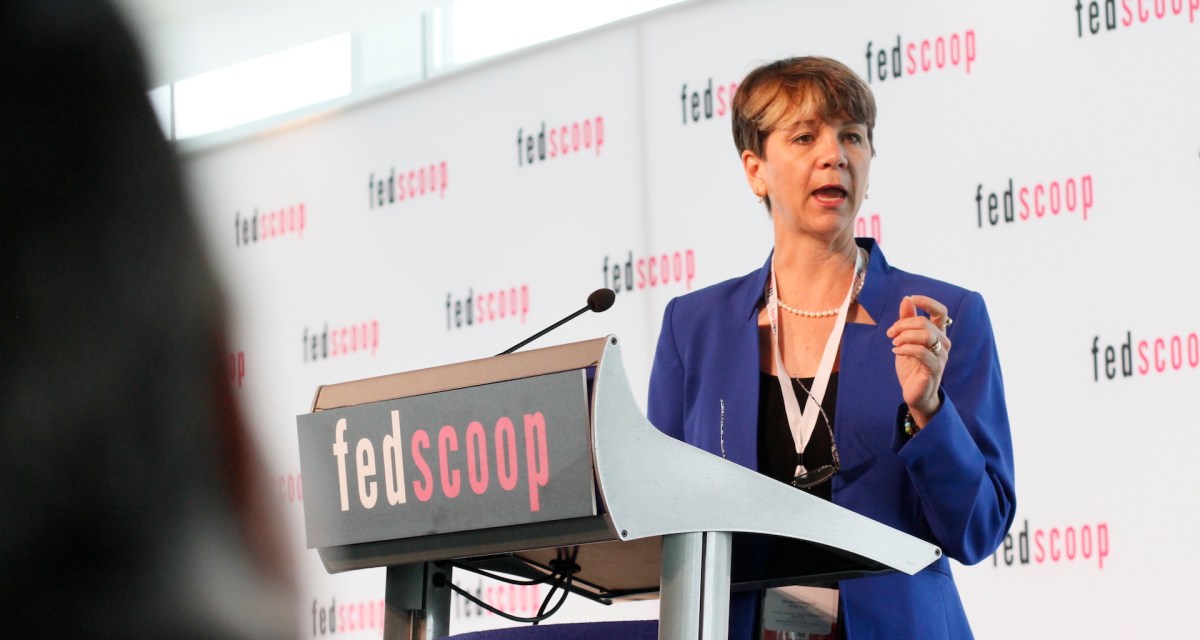
It’s axiomatic that cybersecurity is all about risk management, but NASA CIO Renee Wynn said Tuesday that all IT, indeed all technology, has a “dark side” that must be contained.
In a federal agency like NASA “the IT spend is all about managing risks — what are you buying?,” Wynn said Tuesday during FedScoop’s IT Modernization Summit. “Where’s it from? How well does it fit with your ecosystem? And can you protect it when it gets there?”
“Cybersecurity is about that last piece,” she added.
But long before IT is actually installed, the risk has to be assessed.
“It’s coming into to an [IT] environment from 1977,” she said. In fact, parts of NASA’s legacy IT were even older than that, since they dated back to the earliest days of space exploration.
“Before it flew you had to invent it, and it had to be on the chalkboard …probably for 10 years [before that] … so think about technology from 1967,” she told a standing-room only crowd at the Newseum in Washington, D.C.
Wynn told the summit, she is a subscriber, in certain cases, to the theory of “security through antiquity” — though she didn’t use those words.
In security terms, she said, “sometimes old is good.”
By contrast, technological advances “always have a dark side,” she said, giving as an example the increasing ease with which satellites can be put in orbit.
While that made it possible for NASA to blast satellites designed by school students into space, it also means that U.S. adversaries are more easily able to hold at risk vital national security satellites, such as those that provide global positioning services, or GPS.
“Now that more capability is flying around, it’s not just debris [that might pose a threat to space vehicles] it’s what [the adversary] can do — and we know there are some satellites vital to the protection of the United States.”
Wynn noted that, against certain attack vectors — like insider threats for instance — low tech options were often “the best you can do.”
“We like locked doors,” she said.
Latest Podcasts
Government
FBI officials say AI is bolstering adversaries, emphasizing need to focus on cyber basics, patching
Feds accuse China of ‘systematic’ distillation of U.S. AI models
CIA’s Michael Ellis says cyber intelligence is changing how the agency operates
Jail time for Maine child in 764 marks turning point in federal law enforcement
Technology
Threats
Chinese espionage groups swarm to exploit triple-link chain of zero-days
Microsoft discloses two actively exploited zero-days among 974 vulnerabilities
Russian national extradited to US for alleged involvement in bank-account takeover scheme
Attackers exploit zero-days in consistently besieged SonicWall product
Policy
Whistleblower says USPS deploying new, ‘untested’ IT systems governing mail-in ballots
‘Watershed 250’ test program in Texas looks to private sector for water cybersecurity help
Former sexual abuse victims say Grok used their images, videos to train deepfake capabilities
Cyber threats nudge Trump to sign executive order on foreign equipment in U.S. energy infrastructure
Text extracted automatically; images, tables and formatting may be missing. Original: https://cyberscoop.com/nasa-cio-says-it-is-all-about-risk-management/