Two years since the introduction of the extended databases
Full article304 words · extracted from securelist.com · click to collapse



Exactly two years ago we introduced our extended databases.
These databases protect against AdWare, RiskWare and PornWare. Some people like to refer to the extended databases simply as anti-spyware protection, but we actually detect much more than just that with the help of these databases, most notably RiskWare programs.
Back then we still had cumulative updates and the extended databases consisted of three components: advware.avc, riskware.avc and pornware.avc.
Later two of those names changed to adware.avc and obscene.avc. Since the beginning of this year we simply have combined them into extxxx.avc database, where the x stands for a decimal figure. However, we’ve actually been detecting these types of threats for much longer than two years.
Before we introduced the extended databases the detection of AdWare etc. was included in x-files.avc.
Two years ago it was special to have a separate option to cover such threats, now it is a much more common feature for antivirus programs.
You can select the extended databases by going to KAV’s settings, clicking on Threats and exclusions, and then selecting the extended database.
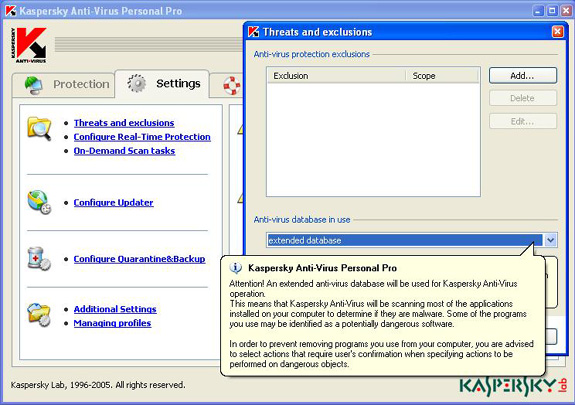
Be sure to read the pop-up message when choosing a database from the dropdown list.
Latest Webinars
Reports
Kaspersky researchers have discovered new Mirage Kitten attacks using previously undocumented malware families: NodeRabbit in Node.js and PollCat in JavaScript.
Our experts discovered a new CoolClient backdoor variant with a kernel-mode rootkit driver that hides malicious processes, files, and network connections from security tools and threat analysts.
Kaspersky experts break down a new Armored Likho campaign that poses as a fundraising efforts and delivers a new Still Toolkit aimed at stealing Telegram data and eavesdropping on victims.
Kaspersky researchers reveal previously undocumented malware attributed to Mirage Kitten (UNC1549, Smoke Sandstorm, Nimbus Manticore): NightLedger backdoor, ArcBridge, and BridgeHead tunneling tools.
Text extracted automatically; images, tables and formatting may be missing. Original: https://securelist.com/two-years-since-the-introduction-of-the-extended-databases/30037/