Vast hack-for-hire scheme against activists, corporate targets tied to Indian IT firm
Full article686 words · extracted from cyberscoop.com · click to collapse
Get our latest cybersecurity news first on Google.
Environmental actvisits, anti-net neutrality groups and investment services were among the intended targets.
An Indian cybersecurity firm operated a widespread hack-for-hire scheme that, for a span of seven years, aimed to steal passwords from journalists, advocacy groups, investment firms and an array of other targets, according to new research.
Since 2013, thousands of people throughout the world have been targeted with phishing emails that appeared to come from friends, co-workers, Facebook, pornography websites and other sources. In fact, the emails aimed to trick recipients into providing their username and password to BellTroX InfoTech Services, an Indian security firm that aimed to hack organizations on behalf of its clients, according to the internet watchdog group Citizen Lab, a research group affiliated with the University of Toronto.
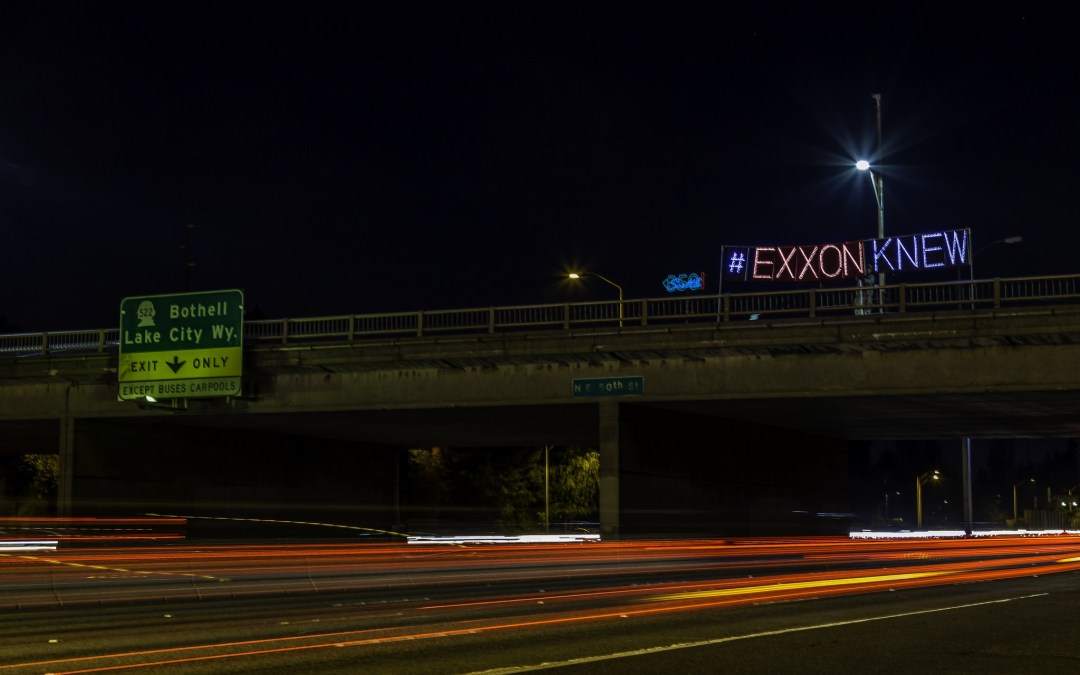
Citizen Lab did not provide details on the company’s clients, but did count the net neutrality advocacy groups Fight for the Future and the Electronic Frontier Foundation among the intended victims. Environmental groups working on the #ExxonKnew campaign, which argued that Exxon Mobil ignored evidence of climate change for decades, also were targeted “extensively,” Citizen Lab found. Researchers have classified the BellTroX InfoTech Services campaign as “Dark Basin.”
Other targets included the investment firm Muddy Waters and the private equity giant KKR, Reuters found.
A U.S. federal criminal investigation into the matter is ongoing, according to the New York Times. BellTroX could not immediately be reached for comment Tuesday.
“Dark Basin’s activities make it clear that there is a large and likely growing hack-for-hire industry,” Citizen Lab researchers wrote in the report. “Hack-for-hire groups enable companies to outsource activities….which muddies the waters and can hamper legal investigations. Previous court cases indicate that similar operations to BellTroX have contracted through a murky set of contractual, payment, and information sharing layers that may include law firms and private investigators and which allow clients a degree of deniability and distance.”
Researchers’ findings included nearly 28,000 websites made to look like they were legitimate businesses or services, a process hackers use to make phishing attacks more credible. Some environmental organizations targeted as part of the campaign encouraged email recipients to click on a Google News link about Exxon Mobil, while some messages masqueraded as lawyers involved in the legal fight against Exxon. In one case, attackers sent phishing email to a target’s child, a technique that Citizen Lab said highlights “the well-informed nature of the targeting, and an intelligence gathering objective.”
Citizen Lab did not accuse Exxon Mobil of any wrongdoing, and has suggested that many of Dark Basin’s intended victims were engaged in legal disputes. That could mean that private investigators hired to help the litigation hired BellTroX, though the true circumstances remain unclear.
Latest Podcasts
Government
FBI officials say AI is bolstering adversaries, emphasizing need to focus on cyber basics, patching
Feds accuse China of ‘systematic’ distillation of U.S. AI models
CIA’s Michael Ellis says cyber intelligence is changing how the agency operates
Jail time for Maine child in 764 marks turning point in federal law enforcement
Technology
Threats
Chinese espionage groups swarm to exploit triple-link chain of zero-days
Microsoft discloses two actively exploited zero-days among 974 vulnerabilities
Russian national extradited to US for alleged involvement in bank-account takeover scheme
Attackers exploit zero-days in consistently besieged SonicWall product
Policy
Whistleblower says USPS deploying new, ‘untested’ IT systems governing mail-in ballots
‘Watershed 250’ test program in Texas looks to private sector for water cybersecurity help
Former sexual abuse victims say Grok used their images, videos to train deepfake capabilities
Cyber threats nudge Trump to sign executive order on foreign equipment in U.S. energy infrastructure
Text extracted automatically; images, tables and formatting may be missing. Original: https://cyberscoop.com/dark-basin-citizen-lab-belltrox-exxon-mobile-hacking/