Top DOJ official 'pleased' with multiagency and branch response to courts data breach
Full article1,061 words · extracted from cyberscoop.com · click to collapse
Get our latest cybersecurity news first on Google.
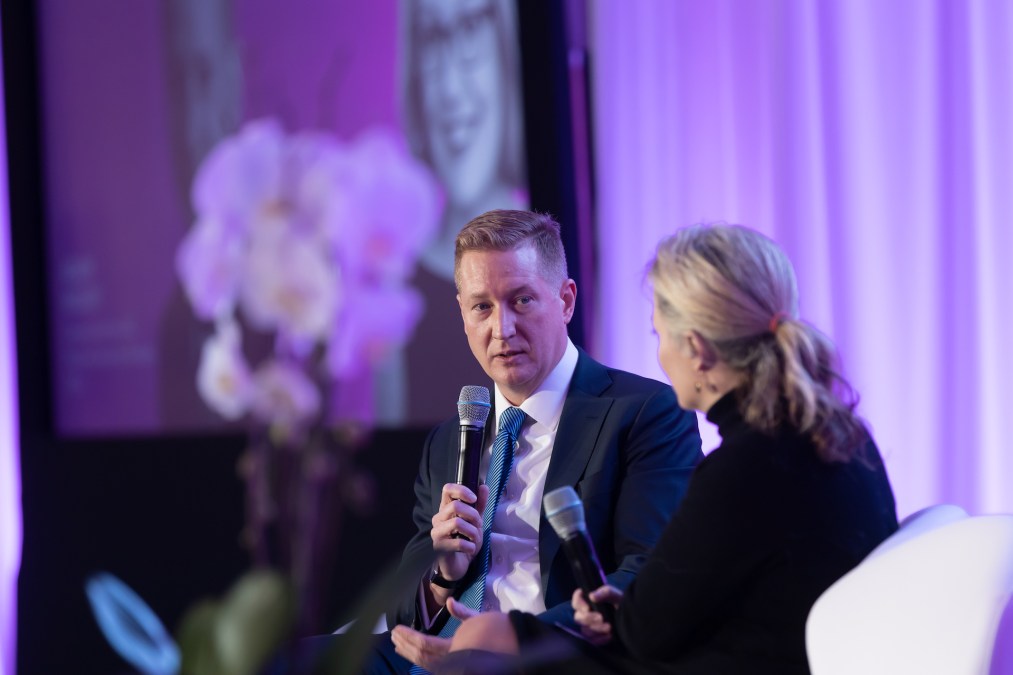
Deputy Assistant Attorney General for National Security Adam Hickey discussed the breach and the need to balance transparency with privacy related to sensitive material.
The Department of Justice and Department of Homeland Security’s response to the 2020 breach of the federal courts’ public records management system — thrust into the headlines by the head of the House Judiciary Committee in July — was a “model” of different branches of government working through complex issues in a constructive way, a top DOJ official said Thursday.
Deputy Assistant Attorney General for National Security Adam Hickey, speaking at the CyberTalks event, said he’s been “pleased” with the cross-agency and branch cooperation in the wake of what he called “an apparent compromise” of the Case Management/Electronic Case Files (CM/ECF) system, which allows both the ability to file court records online and public access to court filings and records.
“I think it was a model, not only for the DOJ and DHS working together to respond to a system owner’s needs, but we were able to work through some very complex issues that arise, as you might imagine, when you’re dealing with a separate branch of government,” Hickey said. “The courts are, understandably, cautious working with the executive branch given the sensitivity in there.”
While the “overwhelming majority” of the material in the database is public, Hickey said, “an incredibly small amount of material in there is sealed material,” such as arrest and search warrants, sealed charges and other non-public documents.
Hickey added that one of the lessons from the situation came from working with the Administrative Office of the United States Courts — the agency within the judicial branch that provides a broad range of administrative support for federal courts — to develop alternative means to file “that small portion of court documents, the most highly sensitive documents that shouldn’t be online.”
“Just because it’s convenient,” Hickey said, “doesn’t mean that that’s the best thing to do from a risk management perspective.”
Hickey told CyberScoop in August that the Justice Department has filed its most sensitive court documents on paper since January 2021 but did not connect that change to the breach of the courts.
The breach has attracted intense Congressional scrutiny. House Judiciary Chairman Rep. Jerrold Nadler said in July that the U.S. federal court system faced “an incredibly significant and sophisticated cybersecurity breach” dating to early 2020 that “had lingering impacts” on the DOJ and other agencies. His committee learned about the “startling breadth and scope of the court’s document management system’s security failure,” in March 2022, Nadler said.
“Perhaps even more concerning is the disturbing impact this security breach had on pending civil and criminal litigation, as well as ongoing national security or intelligence matters,” he added.
The same day, U.S. Sen. Ron Wyden, D-Ore., wrote a letter to the head of the Administrative Office of the United States Courts, Roslynn R. Mauskopf, demanding answers about the incident. In September Mauskopf responded and said that the agency “takes these threats seriously,” and that given the sensitivity of the matter, “communications to Congress on these matters have been through various confidential or classified briefings to Members and staff of relevant committees, with Executive Branch agencies participating as appropriate.”
Wyden told CyberScoop in September that the response was “disappointing,” and said that the court administrators “continue to refuse to be transparent with the public,” adding that the “continued stonewalling, nearly two years after the hack took place, is a major red flag about the state of the courts’ systems.”
Hickey said Thursday that during “any significant security issue we have to balance a desire for transparency” with the needs of an investigation and “the rights and privacy of the system owner.”
More Scoops
SCOTUS tosses one of two injunctions against Trump USPS mail-in ballot rules
The 6-3 decision dismisses one lawsuit brought by states, saying they have no standing to sue because the disputed sections “neither requires nor forbids anything of anyone outside…
Federal court dismisses Trump DOJ lawsuit seeking California voter data
Federal judiciary touts cybersecurity work in wake of latest major breach
Latest Podcasts
Government
FBI officials say AI is bolstering adversaries, emphasizing need to focus on cyber basics, patching
Feds accuse China of ‘systematic’ distillation of U.S. AI models
CIA’s Michael Ellis says cyber intelligence is changing how the agency operates
The G7 tells industry to hurry up and prep for post-quantum encryption
Technology
Threats
Microsoft discloses two actively exploited zero-days among 974 vulnerabilities
Russian national extradited to US for alleged involvement in bank-account takeover scheme
Attackers exploit zero-days in consistently besieged SonicWall product
Jail time for Maine child in 764 marks turning point in federal law enforcement
Policy
Whistleblower says USPS deploying new, ‘untested’ IT systems governing mail-in ballots
‘Watershed 250’ test program in Texas looks to private sector for water cybersecurity help
Former sexual abuse victims say Grok used their images, videos to train deepfake capabilities
Cyber threats nudge Trump to sign executive order on foreign equipment in U.S. energy infrastructure
Text extracted automatically; images, tables and formatting may be missing. Original: https://cyberscoop.com/doj-courts-breach-lesson-pleased-transparency/