IM
Full article214 words · extracted from securelist.com · click to collapse



I recently came across an interesting IRCBot which KAV detects as Backdoor.Win32.IRCBot.lo.
When I took a closer look at it, I found out that it’s quite an advanced bot with a lot of features.
The thing which interested me most was the ability of the bot to spread via IM. There’s support for just about every IM-client.
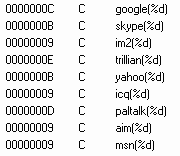
It also started me thinking about the way malware which spreads via IM has evolved over the last year, specifically the shift from IM-Worm+IRCBot to ‘IM-Bot’ – an IRCBot which also includes IM-Worm functionality.
We’ll have an article about this on viruslist in the near future.
Latest Webinars
Reports
Kaspersky researchers have discovered new Mirage Kitten attacks using previously undocumented malware families: NodeRabbit in Node.js and PollCat in JavaScript.
Our experts discovered a new CoolClient backdoor variant with a kernel-mode rootkit driver that hides malicious processes, files, and network connections from security tools and threat analysts.
Kaspersky experts break down a new Armored Likho campaign that poses as a fundraising efforts and delivers a new Still Toolkit aimed at stealing Telegram data and eavesdropping on victims.
Kaspersky researchers reveal previously undocumented malware attributed to Mirage Kitten (UNC1549, Smoke Sandstorm, Nimbus Manticore): NightLedger backdoor, ArcBridge, and BridgeHead tunneling tools.
Text extracted automatically; images, tables and formatting may be missing. Original: https://securelist.com/im-bot/30118/