Eugene Kaspersky defends publishing 'Slingshot' report
Full article622 words · extracted from cyberscoop.com · click to collapse
Get our latest cybersecurity news first on Google.
"Our job is to take the fish from the water ... We see it’s a fish, and we have to catch it."
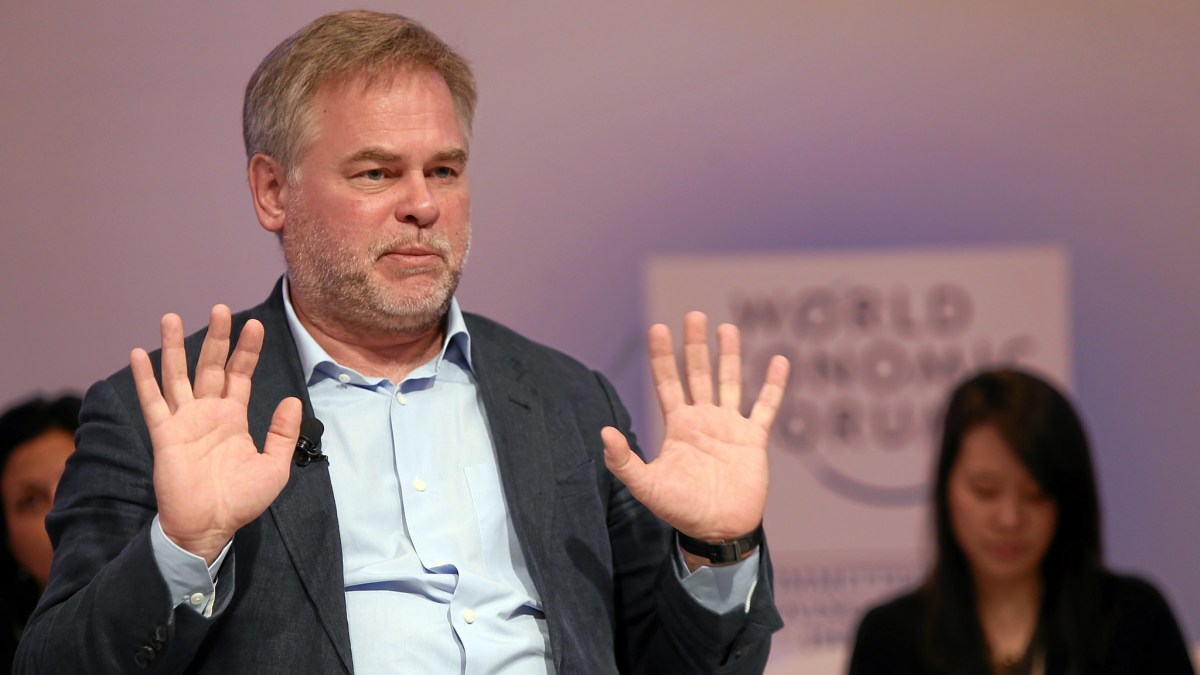
The founder and current CEO of Kaspersky Lab is defending the Moscow-based company after it published a research report that ultimately exposed an active U.S. cyber-espionage operation against ISIS and Al-Qaeda terrorists.
In an interview with Australian press, Eugene Kaspersky said his company’s anti-virus engine does not discriminate based on nationality or the malware authors’ intent. Prior reporting by CyberScoop showed that the research report in question, which looked at a malware framework dubbed “Slingshot,” was in fact connected to an expansive U.S.-led counterterrorism effort.
“Don’t blame our X-ray,” he told The Australian after speaking at a Formula One event in Melbourne. “It rings on any kind of gun. It doesn’t matter who’s wearing the gun, a terrorist or a policeman. We provide the world’s best X-ray … Maybe days after we find that it’s a criminal searching for money, or it’s espionage looking for information. Our X-ray is made to ring for anything.”
While Kaspersky did not address the specific decision to publish the Slingshot report, he deflected blame by claiming that Kaspersky Lab’s technology is designed to spot malicious software regardless of origin or purpose.
Using another metaphor, Kaspersky added: “[our job is to] take the fish from the water … We don’t know what language this fish is speaking. We see it’s a fish, and we have to catch it.”
By publishing the Slingshot report, Kaspersky Lab forced the U.S. to shut down portions of the operation, sources told CyberScoop. But it’s not clear whether Kaspersky Lab was at all aware that its investigation into Slingshot would eventually expose covert U.S. programs abroad.
The disclosure occurred at an unfortunate time for Kaspersky Lab, as the company continues to fight a contentious legal battle with the U.S. government. In September, the Department of Homeland Security banned the use of Kaspersky’s anti-virus product across civilian government agencies, citing a risk to national security. Then in December, President Donald Trump signed into law the National Defense Authorization Act, which went further in banning all Kaspersky Lab products across the entire government.
Since CyberScoop’s original story was published, a number of private sector cybersecurity researchers have argued both sides, with some saying Kaspersky was justified in exposing Slingshot while others arguing that counterterrorism operations should be out-of-bounds.
Latest Podcasts
Government
FBI officials say AI is bolstering adversaries, emphasizing need to focus on cyber basics, patching
Feds accuse China of ‘systematic’ distillation of U.S. AI models
CIA’s Michael Ellis says cyber intelligence is changing how the agency operates
The G7 tells industry to hurry up and prep for post-quantum encryption
Technology
Threats
Microsoft discloses two actively exploited zero-days among 974 vulnerabilities
Russian national extradited to US for alleged involvement in bank-account takeover scheme
Attackers exploit zero-days in consistently besieged SonicWall product
Jail time for Maine child in 764 marks turning point in federal law enforcement
Policy
Whistleblower says USPS deploying new, ‘untested’ IT systems governing mail-in ballots
‘Watershed 250’ test program in Texas looks to private sector for water cybersecurity help
Former sexual abuse victims say Grok used their images, videos to train deepfake capabilities
Cyber threats nudge Trump to sign executive order on foreign equipment in U.S. energy infrastructure
Text extracted automatically; images, tables and formatting may be missing. Original: https://cyberscoop.com/kaspersky-slingshot-isis-operation-comments/