Chinese drone maker DJI launches bug bounty program after U.S. Army ban
Full article601 words · extracted from cyberscoop.com · click to collapse
Get our latest cybersecurity news first on Google.
Rewards range from $100 to $30,000 in the self-organized effort.
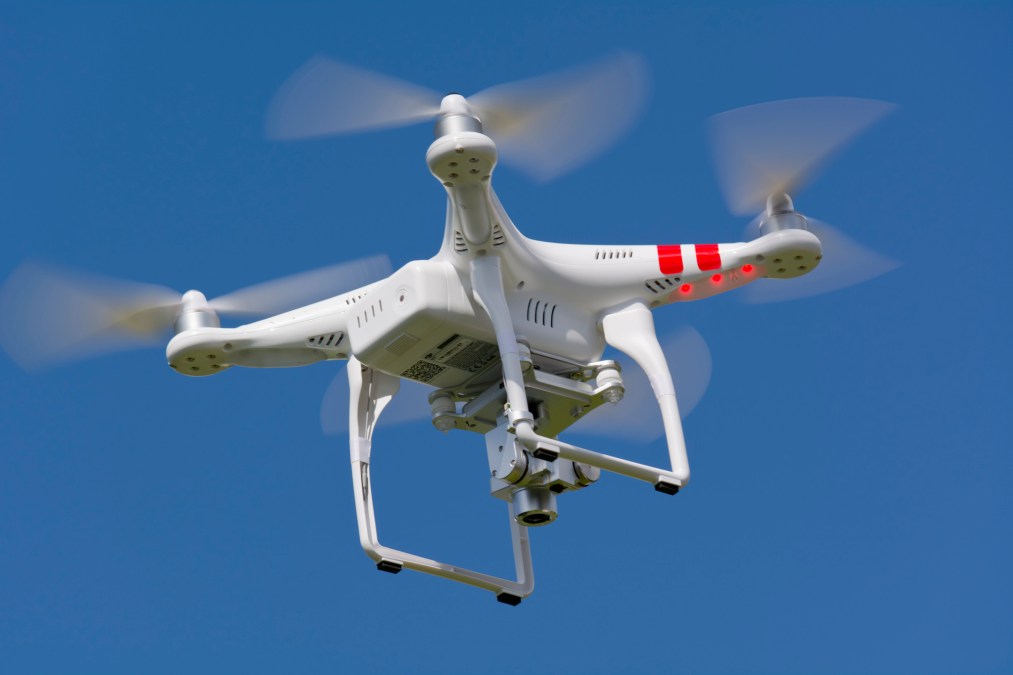
Chinese drone maker Daijiang Innovation Corporation (DJI) launched a bug bounty program Monday after the company’s products were banned by the U.S. Army about one month ago due to unspecified “cyber vulnerabilities.”
DJI owns 70 percent of the global drone market, according to a 2016 analysis by Goldman Sachs and Oppenheimer. Analysts predict that the market will expand to $100 billion in five years.
The company also said Monday it had released several security updates and removed third-party plugins that did not meet security standards.
The Army ban pushed DJI to launch several security updates over the last month, including one patch that added the ability to disconnect a drone from the internet while it is in flight. Customer concerns were ultimately the motivating factor that caused DJI to make changes to its software, Reuters previously reported.
The newly announced bug bounty program offers rewards from $100 to $30,000 depending on the nature of the discovered software vulnerability. Reports can be sent to [email protected], and a fully fledged reporting website is coming, according to DJI.
“Security researchers, academic scholars and independent experts often provide a valuable service by analyzing the code in DJI’s apps and other software products and bringing concerns to public attention,” DJI Director of Technical Standards Walter Stockwell said in a statement.
DJI is targeting, among other experts, hackers who have long been focused on DJI’s drones. A thriving community of drone hackers exists that finds and exploits DJI security holes in order to break out of pre-programmed no-fly zones and other restrictions. The question now is whether they’ll report their findings in exchange for the drone makers’ reward.
DJI spokesperson Adam Lisberg told CyberScoop the new bug bounty program wasn’t a reaction to the U.S. Army ban but instead “has to do with a number of issues that have been raised with us by various security researchers.”
“We want to engage with the research community and respond to their reasonable concerns with a common goal of cooperation and improvement,” Stockwell said. “We value input from researchers into our products who believe in our mission to enable customers to use DJI products that are stable, reliable and trustworthy.”
Correction: DJI is self-organizing the bug bounty program and is not, as was erroneously reported, using the BugCrowd platform.
Latest Podcasts
Government
FBI officials say AI is bolstering adversaries, emphasizing need to focus on cyber basics, patching
Feds accuse China of ‘systematic’ distillation of U.S. AI models
CIA’s Michael Ellis says cyber intelligence is changing how the agency operates
Jail time for Maine child in 764 marks turning point in federal law enforcement
Technology
Threats
Chinese espionage groups swarm to exploit triple-link chain of zero-days
Microsoft discloses two actively exploited zero-days among 974 vulnerabilities
Russian national extradited to US for alleged involvement in bank-account takeover scheme
Attackers exploit zero-days in consistently besieged SonicWall product
Policy
Whistleblower says USPS deploying new, ‘untested’ IT systems governing mail-in ballots
‘Watershed 250’ test program in Texas looks to private sector for water cybersecurity help
Former sexual abuse victims say Grok used their images, videos to train deepfake capabilities
Cyber threats nudge Trump to sign executive order on foreign equipment in U.S. energy infrastructure
Text extracted automatically; images, tables and formatting may be missing. Original: https://cyberscoop.com/chinese-drone-maker-dji-launches-bug-bounty-program-u-s-army-ban/