Security threat prompts Progress to disable ShareFile accounts, tell customers to shut down servers
Vulnerabilities mentionedAll →
| CVE | Vulnerability | CVSS | EPSS | Flags | Affected | Exposure | Published |
|---|---|---|---|---|---|---|---|
| CVE-2026-2699 +1 in the same advisory: …2701 | Unauthenticated RCE in Progress ShareFile Storage Zones Controller CVE-2026-2699 is an improper access control flaw (CWE-284) in customer-managed Progress ShareFile Storage Zones Controller (SZC) that lets an unauthenticated attacker reach restricted configuration pages over the network. Because the issue is reachable pre-authentication with no user interaction and low complexity (AV:N/AC:L/PR:N), an attacker needs only network access to an exposed controller. Successful abuse allows the attacker to change system configuration and potentially escalate to full remote code execution, with high impact to confidentiality, integrity, and availability (CVSS 3.1: 9.8). Any organization running its own customer-managed SZC deployment is affected; the Progress/ShareFile-hosted cloud service itself is not the flaw, though Progress has taken precautionary emergency action (disabling ShareFile accounts and urging customers to shut down controllers) amid an active security threat per press reports. A public proof-of-concept exploit is available (watchTowr Labs), the flaw carries a very high EPSS of 59.5% (99th percentile) indicating strong likelihood of exploitation within 30 days, and it is not yet listed in CISA KEV. Do: Apply the vendor patch as soon as possible per the Progress security bulletin (the fixed version is not specified in the available data). As interim mitigation, restrict unauthenticated internet access to the SZC configuration interface (e.g., firewall or reverse-proxy rules) and consider temporarily taking the controller offline if immediate patching is not possible, as Progress has advised. Review logs for unauthenticated requests to configuration pages and signs of configuration changes or follow-on command execution. | 9.8 group max | 60% | PoC |
| moderate~1,000-10,000 internet-exposed Storage Zones Controller instances |
Full article428 words · extracted from helpnetsecurity.com · click to collapse
A “credible external security threat” targeting Progress Software’s ShareFile Storage Zone Controllers (SZC) – the on-premises, customer-managed server components where organizations store files shared via this popular enterprise platform – has spurred the company to disable access to ShareFile accounts that are using them.
The warning was sent to customers via email on July 10, urging them to manually shut down the server that is hosting their Storage Zone Controllers.
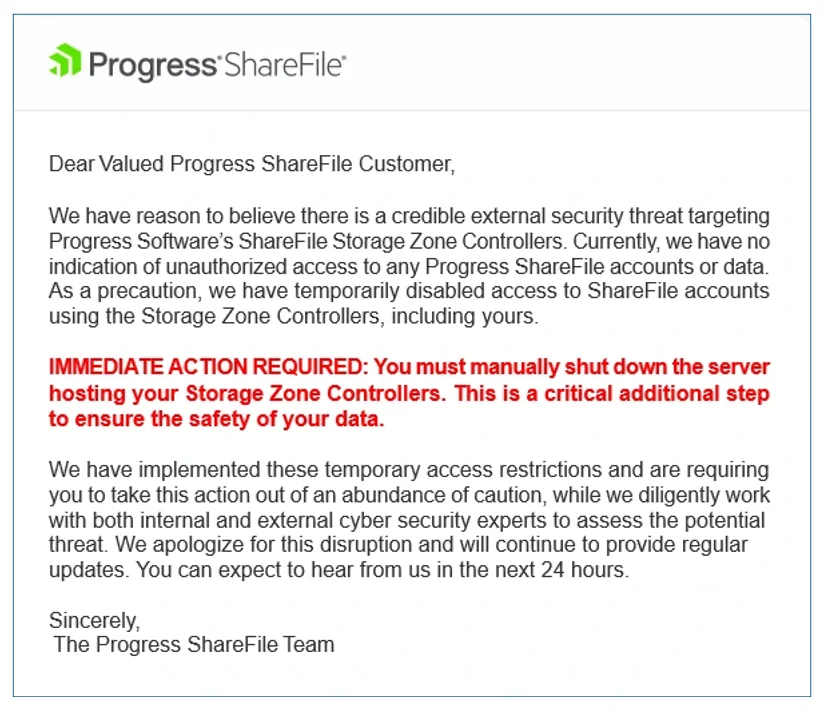
The initial email alert from Progress Software
“This is a critical additional step to ensure the safety of your data,” the company said, and promised regular updates on the situation.
Investigation ongoing as access is gradually restored
The ShareFile Status Page still shows the status report from July 10, saying that the company is investigating the issue and that “ShareFile customers with Storage Zone Controllers are not operational at this time.”
A Knowledge Base article published on July 11 says that Progress Software has “no indication of unauthorized access to any Progress ShareFile Accounts or data.”
Participants in an active discussion thread on the Sysadmin subreddit have complained that Progress’s subsequent communications contained no new information.
The company is reportedly starting to restore access to the affected ShareFile accounts, though it’s asking customers to keep their Storage Zone Controllers disabled for the time being.
While Progress is yet to officially confirm the underlying cause of the disruption, theories about it are circulating. Some commenters suggest that attackers may have chained two vulnerabilities (CVE-2026-2699 and CVE-2026-2701) to achieve pre-authentication remote code execution on unpatched on-premises SZC deployments.
The company said it’s working with internal and external cyber security experts to assess the potential threat.
UPDATE (July 14, 2026, 01:15 a.m. ET):
“Our investigation identified a high severity path traversal vulnerability in Progress ShareFile Storage Zones Controller affecting versions 5.x and 6.x. We have developed and released patched versions to address this issue,” Progress shared in the most recent email sent to customers.
The vulnerability, whose CVE will be published in two weeks, allows an authenticated administrative user to read arbitrary files accessible to the application’s service account, write threat actor-controlled content to arbitrary directories or enumerate the server filesystem layout, they explained.
Customers using ShareFile Storage Zones Controller have been urged to upgrade to ShareFile Storage Zones Controller v5.12.5 or v6.0.2.
“Currently, we have no indication of unauthorized access to any ShareFile customer account or data, and we have not identified any active threat,” they concluded.

Subscribe to our breaking news e-mail alert to never miss out on the latest breaches, vulnerabilities and cybersecurity threats. Subscribe here!
Text extracted automatically; images, tables and formatting may be missing. Original: https://www.helpnetsecurity.com/2026/07/13/progress-sharefile-security-threat/