SecTor – Security Education Conference 2012, Toronto / CA
Full article330 words · extracted from securelist.com · click to collapse
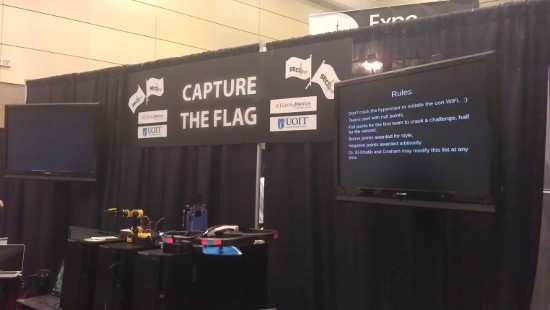

I’m sending greetings from Canada, where I’m attending the 6th annual SecTor Security Education Conference in the very impressive city of Toronto.
With almost 70 talks and nearly 50 exhibitors there are a lot of opportunities to learn about new techniques and meet interesting people from all over the world. In addition there is a “LockPick Village”, a robotics-showcase and a capture the flag competition located in the expo area.
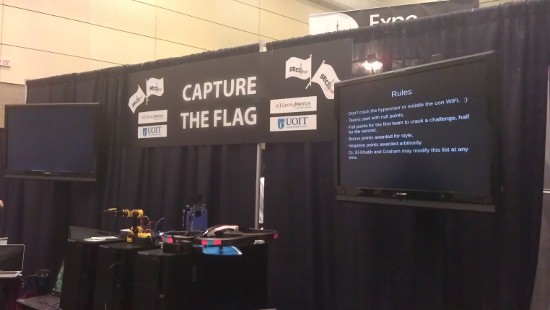
Last but not least, Kaspersky Lab is exhibiting in the expo area.
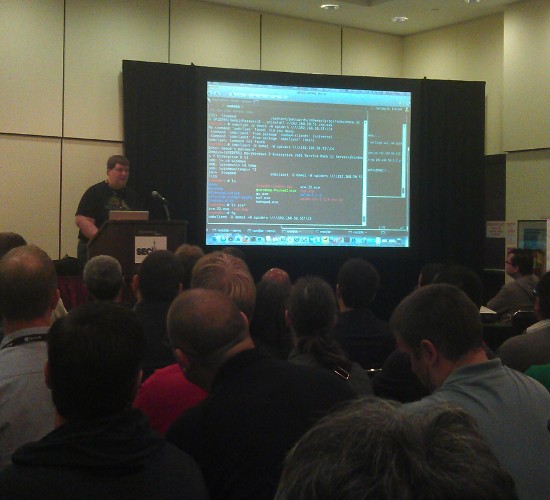
On Tuesday, representing Kaspersky Lab, Dennis Fisher gave a talk about protecting your corporate smartphones from malware and targeted attacks. Among other sessions, I attended very good talks about anti-forensic techniques and their mitigations by Michael Perklin, advanced intrusion methods and workarounds if Metasploit fails by Ryan Linn, and a talk about reversing patches for exploit creation, pen-testing or fun by Bharat Jogi.
At his talk, Jogi described how quick malware authors react on patch-releases. CVE-2012-0003 was patched on 10th of January 2012 – on 26th of January 2012 the first malware was seen in the wild exploiting that bug which leads to a remote code execution vulnerability via MIDI-files.
Over all it has been a nice conference so far, however, additional seats should be provided as some of the talks were a little bit too crowded.
Latest Webinars
Reports
Kaspersky researchers have discovered new Mirage Kitten attacks using previously undocumented malware families: NodeRabbit in Node.js and PollCat in JavaScript.
Our experts discovered a new CoolClient backdoor variant with a kernel-mode rootkit driver that hides malicious processes, files, and network connections from security tools and threat analysts.
Kaspersky experts break down a new Armored Likho campaign that poses as a fundraising efforts and delivers a new Still Toolkit aimed at stealing Telegram data and eavesdropping on victims.
Kaspersky researchers reveal previously undocumented malware attributed to Mirage Kitten (UNC1549, Smoke Sandstorm, Nimbus Manticore): NightLedger backdoor, ArcBridge, and BridgeHead tunneling tools.
Text extracted automatically; images, tables and formatting may be missing. Original: https://securelist.com/sector-security-education-conference-2012-toronto-ca/57773/